

Resources Categories
INDUSTRY FACT FILE · SAAS & ENTERPRISE SOFTWARE
Main Products and Services in SaaS and Enterprise Software
What SaaS and enterprise software vendors offer, the systems behind each product and where they create cybersecurity and compliance exposure.
|
In this document 1. How SaaS vendors earn their money 2. Products by vendor type 3. Building and releasing the product 4. Running, integrating and supporting the product 5. The systems behind the products and services 6. Trends that change the attack surface 7. Mapping products to Codec Networks engagements |
1. How SaaS vendors earn their money
|
Revenue stream |
How it works |
Security relevance |
|
Subscriptions |
Per-user or per-tenant recurring fees |
Churn follows security incidents |
|
Usage-based pricing |
Fees by transactions, API calls or data |
API abuse affects billing and data |
|
Marketplace and integrations |
Revenue from apps and partners |
Third-party access to customer data |
|
Professional services |
Implementation and customisation |
Partner and consultant admin access |
|
On-premise licences |
Licences and maintenance |
Update integrity and vulnerability handling |
2. Products by vendor type
|
Vendor type |
Main products |
Data held |
|
ERP vendors |
Finance, procurement, inventory, manufacturing |
Financial records, supplier and pricing data |
|
CRM vendors |
Sales pipelines, marketing, service desks |
Customer contacts, deals, support tickets |
|
HRMS and payroll vendors |
Payroll, attendance, benefits, recruitment |
Employee identities, salaries, bank details |
|
Collaboration platforms |
Chat, documents, meetings, workflow |
Internal communications and files |
|
Cybersecurity vendors |
Endpoint, identity, network and SOC platforms |
Telemetry and privileged access |
3. Building and releasing the product
Products are built from proprietary code and many open-source components, through CI/CD pipelines and infrastructure-as-code. Vulnerable dependencies, leaked secrets and insecure defaults introduced here reach every customer at release.
4. Running, integrating and supporting the product
In production, multi-tenant applications serve many customers from shared infrastructure. Customers connect through SSO, APIs and OAuth integrations, and support teams use admin tools to troubleshoot tenants. Each of these paths must enforce who can reach which tenant's data.
|
Highest-risk moments Cross-tenant requests, OAuth token grants, support impersonation and bulk exports are where SaaS breaches typically begin. |
5. The systems behind the products and services
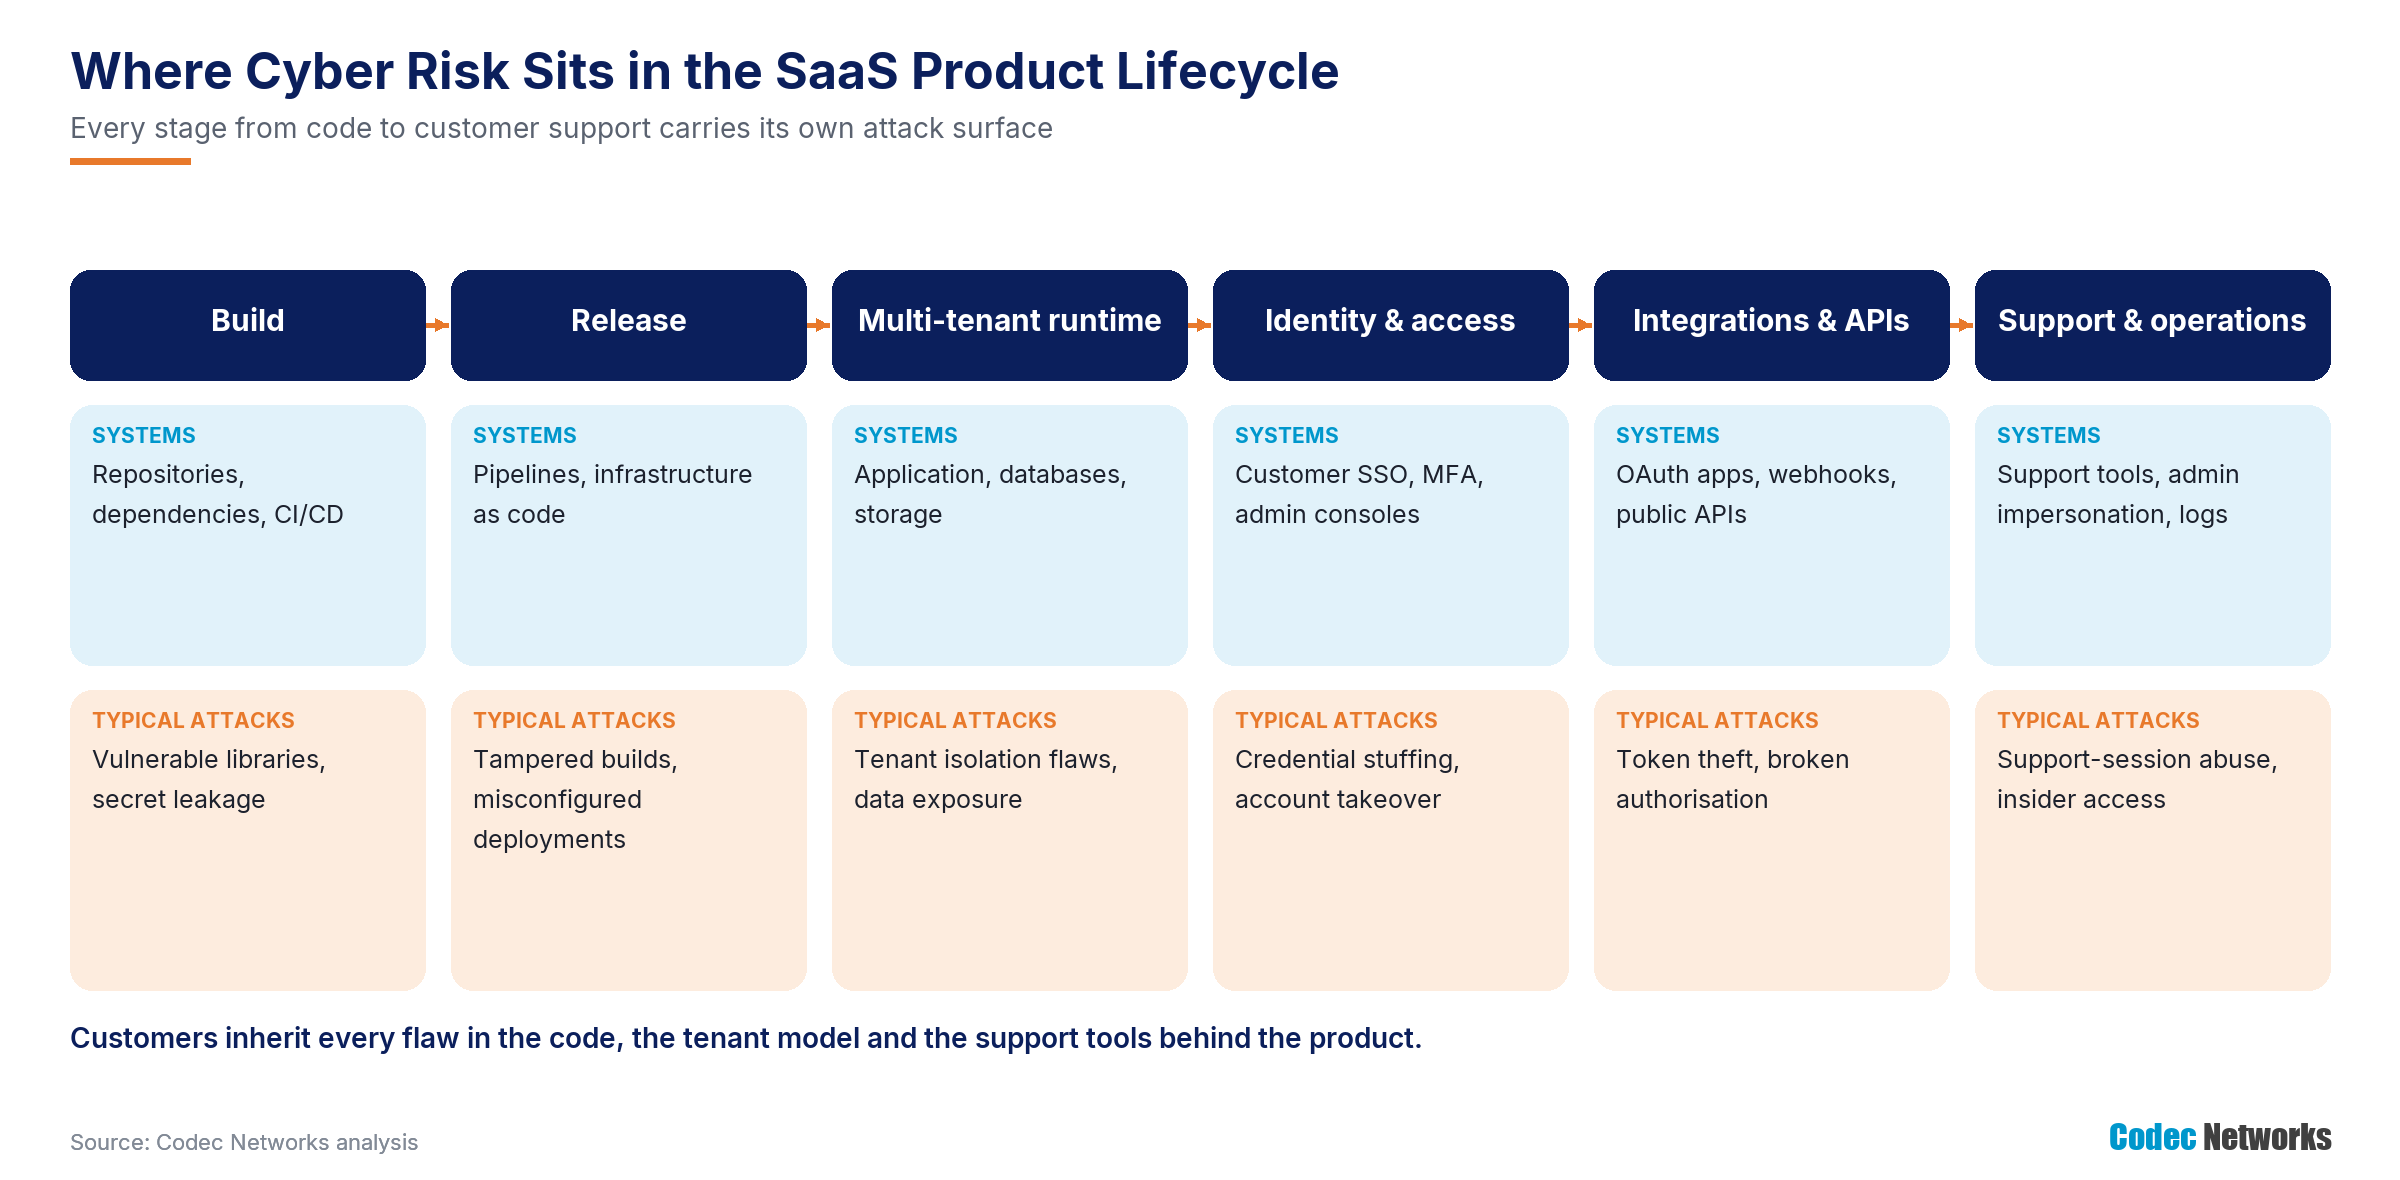
Figure 2: Where cyber risk sits in the SaaS product lifecycle.
|
Product / service |
Systems that deliver it |
Key cyber and compliance touchpoints |
|
Code and dependencies |
Repositories, package managers |
SAST, SCA, secrets scanning, SBOM |
|
Pipelines and infrastructure |
CI/CD, IaC, Kubernetes |
Pipeline and IaC reviews |
|
Multi-tenant application |
Application tier, databases, caches, queues |
Tenant isolation testing |
|
Identity |
SSO, MFA, admin roles |
Account takeover defences |
|
APIs and integrations |
Public APIs, OAuth apps, webhooks |
API and scope reviews, export monitoring |
|
Support and operations |
Support consoles, logs, observability |
Just-in-time access, audit logs |
6. Trends that change the attack surface
|
Trend |
What is changing |
Security implication |
|
AI features in products |
Assistants that query customer data |
Prompt injection and cross-tenant leakage |
|
Integration ecosystems |
More connected apps and marketplaces |
Token theft and over-broad scopes |
|
SBOM expectations |
Customers ask for component lists |
Dependency transparency required |
|
Enterprise and BFSI customers |
Deeper security reviews |
SOC 2, ISO 27001 and flow-down evidence |
|
Info-stealer malware |
Stolen sessions and passwords at scale |
MFA by default and session controls |
7. Mapping products to Codec Networks engagements
|
If the vendor offers… |
Recommended starting engagement |
|
A multi-tenant web platform |
Tenant isolation and product VAPT |
|
Public APIs and integrations |
API testing, OAuth scope review |
|
Mobile or desktop clients |
Mobile and thick-client testing |
|
Sales to enterprises or BFSI |
SOC 2 readiness, flow-down assessment |
|
AI features |
AI and LLM security testing |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: Descriptions are general and based on public information available as of October 2026.