

Resources Categories
INDUSTRY FACT FILE · RENEWABLE ENERGY & ENERGY STORAGE
Industry Overview: Renewable Energy and Energy Storage in India
Who builds and operates solar, wind, storage and smart metering, the regulations that now apply, who buys cybersecurity and why each needs a distinct approach.
|
In this document 1. Why renewable energy cybersecurity matters now 2. The ecosystem at a glance 3. Categories of renewable, storage and metering players 4. The regulatory framework at a glance 5. Government, public-sector and private participants 6. Who buys cybersecurity inside a renewable operator 7. Why each player type needs a different approach 8. How Codec Networks works with renewable operators |
|
Sector scope Sector: renewable energy and energy storage — solar and wind operators, battery storage, renewable asset managers and smart meter providers. Primary service proposition: OT/IoT security, telemetry and cloud assessment, vendor access controls and monitoring. Conventional generation, transmission and DISCOMs are covered in the Power and Electricity fact file. |
1. Why renewable energy cybersecurity matters now
India is rapidly expanding solar, wind and battery storage capacity and rolling out smart meters at national scale. Unlike conventional plants, renewable fleets are spread across hundreds of remote sites and operated through inverters, turbine controllers, battery management systems and OEM cloud platforms—often accessible from anywhere.
|
50 MW Generators and storage covered by CEA Regulations (as reported) |
1 Apr 2027 CEA Cyber Security Regulations in force |
~5,800 Wind turbines lost remote monitoring in a 2022 satellite attack (Germany) |
6 hours Incident reporting to CSIRT-Power and CERT-In (as reported) |
That remote, vendor-dependent model creates new risks. In February 2022, an attack on a satellite communications provider disrupted remote monitoring of about 5,800 wind turbines in Germany; in 2019, a denial-of-service attack interrupted communications at a US renewable operator; and in 2025, US officials reported finding undocumented communication devices in some imported inverters.
The CEA (Cyber Security in Power Sector) Regulations, 2026—notified on 31 July 2026 and in force from 1 April 2027—cover generating companies, captive plants and storage operators of 50 MW and above, as reported. Smaller entities are encouraged to adopt CERT-In's basic controls.
|
Key takeaway For renewable operators, whoever controls remote and vendor access controls generation. Securing that access—and the equipment behind it—is now both a business and a regulatory necessity. |
2. The ecosystem at a glance
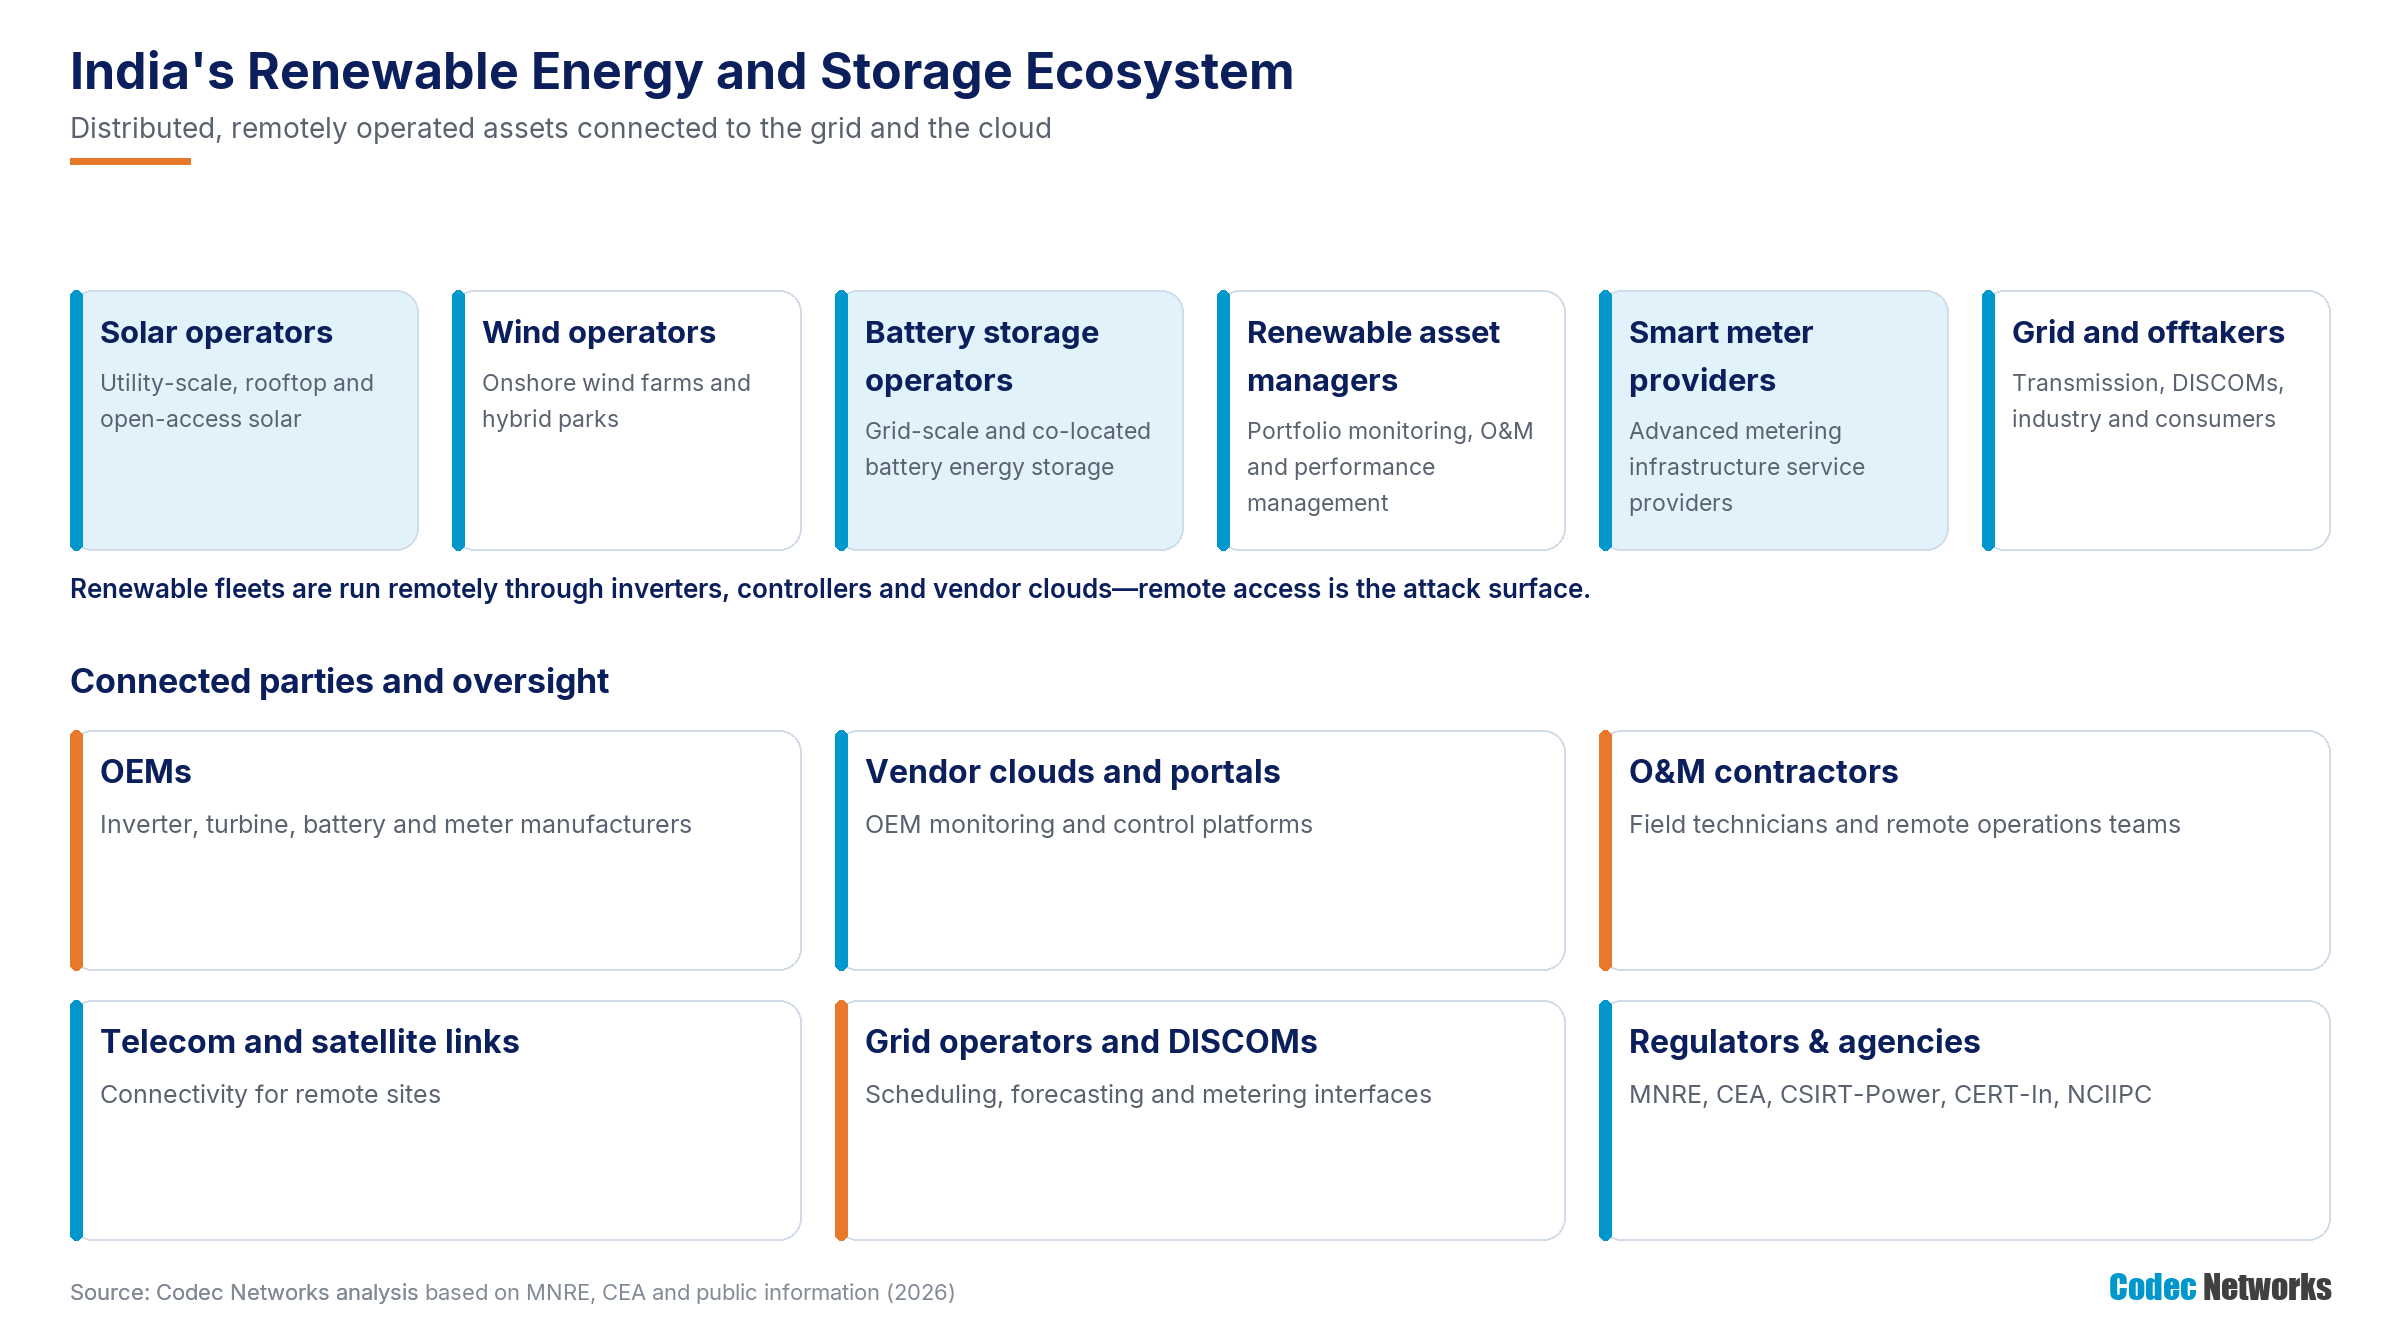
Figure 1: India's renewable energy and storage ecosystem.
3. Categories of renewable, storage and metering players
|
Category |
Who they are |
Typical ownership |
Key regulatory basis |
|
Utility-scale solar operators |
Ground-mounted solar parks selling to DISCOMs and industry |
IPPs, PSUs and developers |
Electricity Act; CEA Regulations 2026 (50 MW and above, as reported) |
|
Wind operators |
Onshore wind farms and repowering projects |
IPPs and developers |
Electricity Act; CEA Regulations 2026 |
|
Battery storage operators |
Grid-scale and co-located battery energy storage |
Developers, utilities and PSUs |
CEA Regulations 2026 (storage of 50 MW and above, as reported) |
|
Hybrid and round-the-clock parks |
Combined solar, wind and storage |
Large IPPs |
CEA Regulations 2026 |
|
Renewable asset managers and O&M |
Portfolio monitoring and maintenance |
Asset managers and O&M contractors |
Contracts; CERT-In |
|
Smart meter providers (AMISPs) |
Advanced metering infrastructure for DISCOMs |
Metering service companies |
DISCOM contracts; DPDP; CERT-In |
|
OEMs and integrators |
Inverters, turbines, batteries, controllers |
Global and Indian manufacturers |
Equipment standards; vendor accountability |
4. The regulatory framework at a glance
|
Instrument |
Key requirements (as reported) |
|
CEA (Cyber Security in Power Sector) Regulations, 2026 |
Notified 31 July 2026; in force 1 April 2027; cover OT linked to the grid and connected IT Generating companies, captive plants and storage operators of 50 MW and above are covered; smaller entities are encouraged to adopt CERT-In's basic controls for MSMEs |
|
Governance and assurance |
Senior CISO and alternate, 24-hour Information Security Division, cyber security policy, Cyber Crisis Management Plan with annual mock drill, annual audit of critical systems |
|
Technical controls and reporting |
Separation of OT networks from the internet; vendor accountability; incidents reported to CSIRT-Power and CERT-In within six hours |
|
CERT-In Directions (2022) |
Six-hour incident reporting and 180-day ICT logs for all body corporates |
|
Revamped Distribution Sector Scheme (2021) |
National smart metering roll-out through AMI service providers working with DISCOMs |
|
DPDP Act 2023 and DPDP Rules 2025 |
Consumer personal data in metering and services; most obligations from May 2027 |
|
Verify applicability Thresholds and requirements are summarised from public reporting. Confirm how the 50 MW threshold applies to your assets against the official gazette notification. |
5. Government, public-sector and private participants
- MNRE leads renewable energy policy; the Ministry of Power and CEA set power-sector rules, including the 2026 cyber regulations.
- CSIRT-Power, CERT-In and NCIIPC handle incident response and critical infrastructure protection.
- Grid operators and DISCOMs schedule, forecast and meter renewable power.
- IPPs, PSUs and developers build and operate large portfolios, often with global OEM equipment.
- AMI service providers deploy and operate smart meters for DISCOMs.
6. Who buys cybersecurity inside a renewable operator
|
Stakeholder |
What they care about |
What they buy |
|
CEO and Board |
Availability, PPAs, lender confidence |
Assurance programmes, Board briefings |
|
CISO / head of IT and OT |
Fleet security and CEA compliance |
Gap assessments, monitoring, audits |
|
Head of asset management |
Performance and remote operations |
Telemetry and vendor access reviews |
|
O&M and site operations |
Field devices and contractors |
Site assessments and access controls |
|
Procurement |
OEM and equipment risk |
Equipment inspection, supplier assessments |
|
Finance and lenders' engineers |
Due diligence and covenants |
Independent assurance reports |
|
Metering operations (AMISPs) |
Head-end and meter security |
AMI testing and monitoring |
7. Why each player type needs a different approach
|
Player type |
Highest-consequence risk |
Starting point for assurance |
|
Solar operator |
Inverter cloud control and exposed controllers |
Vendor portal and site network reviews |
|
Wind operator |
Remote connectivity and turbine controller access |
Connectivity resilience and access reviews |
|
Battery storage operator |
EMS and BMS compromise with safety impact |
EMS/BMS testing and OT monitoring |
|
Hybrid park |
Complex multi-vendor control |
Architecture review and integrated monitoring |
|
Asset manager / O&M |
Portfolio platform ransomware and contractor access |
Platform testing and access governance |
|
Smart meter provider |
Head-end and firmware update compromise |
AMI and update security testing |
8. How Codec Networks works with renewable operators
Codec Networks is a CERT-In empanelled information security auditing organisation certified to ISO 9001:2015, ISO/IEC 27001:2022 and ISO/IEC 20000-1:2018. For renewable and storage operators we deliver OT/IoT security assessments of inverters, controllers and BMS, telemetry and OEM cloud reviews, vendor access controls, fleet monitoring, equipment inspection and CEA Regulations compliance support.
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: This document is general industry guidance based on public information available as of October 2026. CEA (Cyber Security in Power Sector) Regulations, 2026 details are summarised from public reporting; confirm obligations against the official gazette notification and MNRE, CEA and CERT-In instruments.