

Resources Categories
INDUSTRY FACT FILE · MEDICAL DEVICES & MEDTECH
Main Products and Services in Medical Devices and Medtech
What medtech companies build and offer, the technology inside each product and where it creates cybersecurity and compliance exposure.
|
In this document 1. How medtech companies earn their money 2. Products by company type 3. Inside the device 4. Connectivity, cloud and service 5. The systems behind the products and services 6. Trends that change the attack surface 7. Mapping products to Codec Networks engagements |
1. How medtech companies earn their money
|
Revenue stream |
How it works |
Security relevance |
|
Device sales |
Equipment sold to hospitals, labs and consumers |
Every unit carries its security for years |
|
Service and maintenance |
Contracts for servicing installed devices |
Service tools and remote access |
|
Consumables |
Sensors, strips and accessories |
Authenticity and anti-cloning |
|
Software and subscriptions |
SaMD and monitoring platform fees |
Cloud and data security |
|
Exports |
Sales to regulated international markets |
Cybersecurity evidence for approvals |
2. Products by company type
|
Company type |
Main products |
Technology involved |
|
Bedside device makers |
Monitors, pumps, ventilators |
Embedded firmware, network interfaces, central stations |
|
Imaging and lab vendors |
Scanners, analysers |
Workstations, OS platforms, DICOM, remote service |
|
Wearable and home device makers |
Meters, monitors, wearables |
BLE, mobile apps, cloud sync |
|
SaMD developers |
Diagnostic and monitoring software |
Applications, AI models, APIs |
|
Platform providers |
Remote monitoring and IoMT platforms |
Cloud, device identity, dashboards |
3. Inside the device
Devices combine microcontrollers or embedded processors, real-time operating systems, bootloaders, third-party libraries and communications modules. Debug interfaces used in development, hard-coded credentials and keys shared across units are common weaknesses, and third-party components may contain undocumented functions.
4. Connectivity, cloud and service
Devices connect over BLE, Wi-Fi, Ethernet or cellular to gateways, apps and cloud platforms. Firmware updates are delivered over the air or by service engineers using service tools. Remote monitoring platforms aggregate readings from thousands of patients—making identity, update integrity and API authorisation critical.
|
Highest-risk moments Firmware update channels, device-to-cloud authentication, debug interfaces left open in production and third-party communication modules are where device security most often fails. |
5. The systems behind the products and services
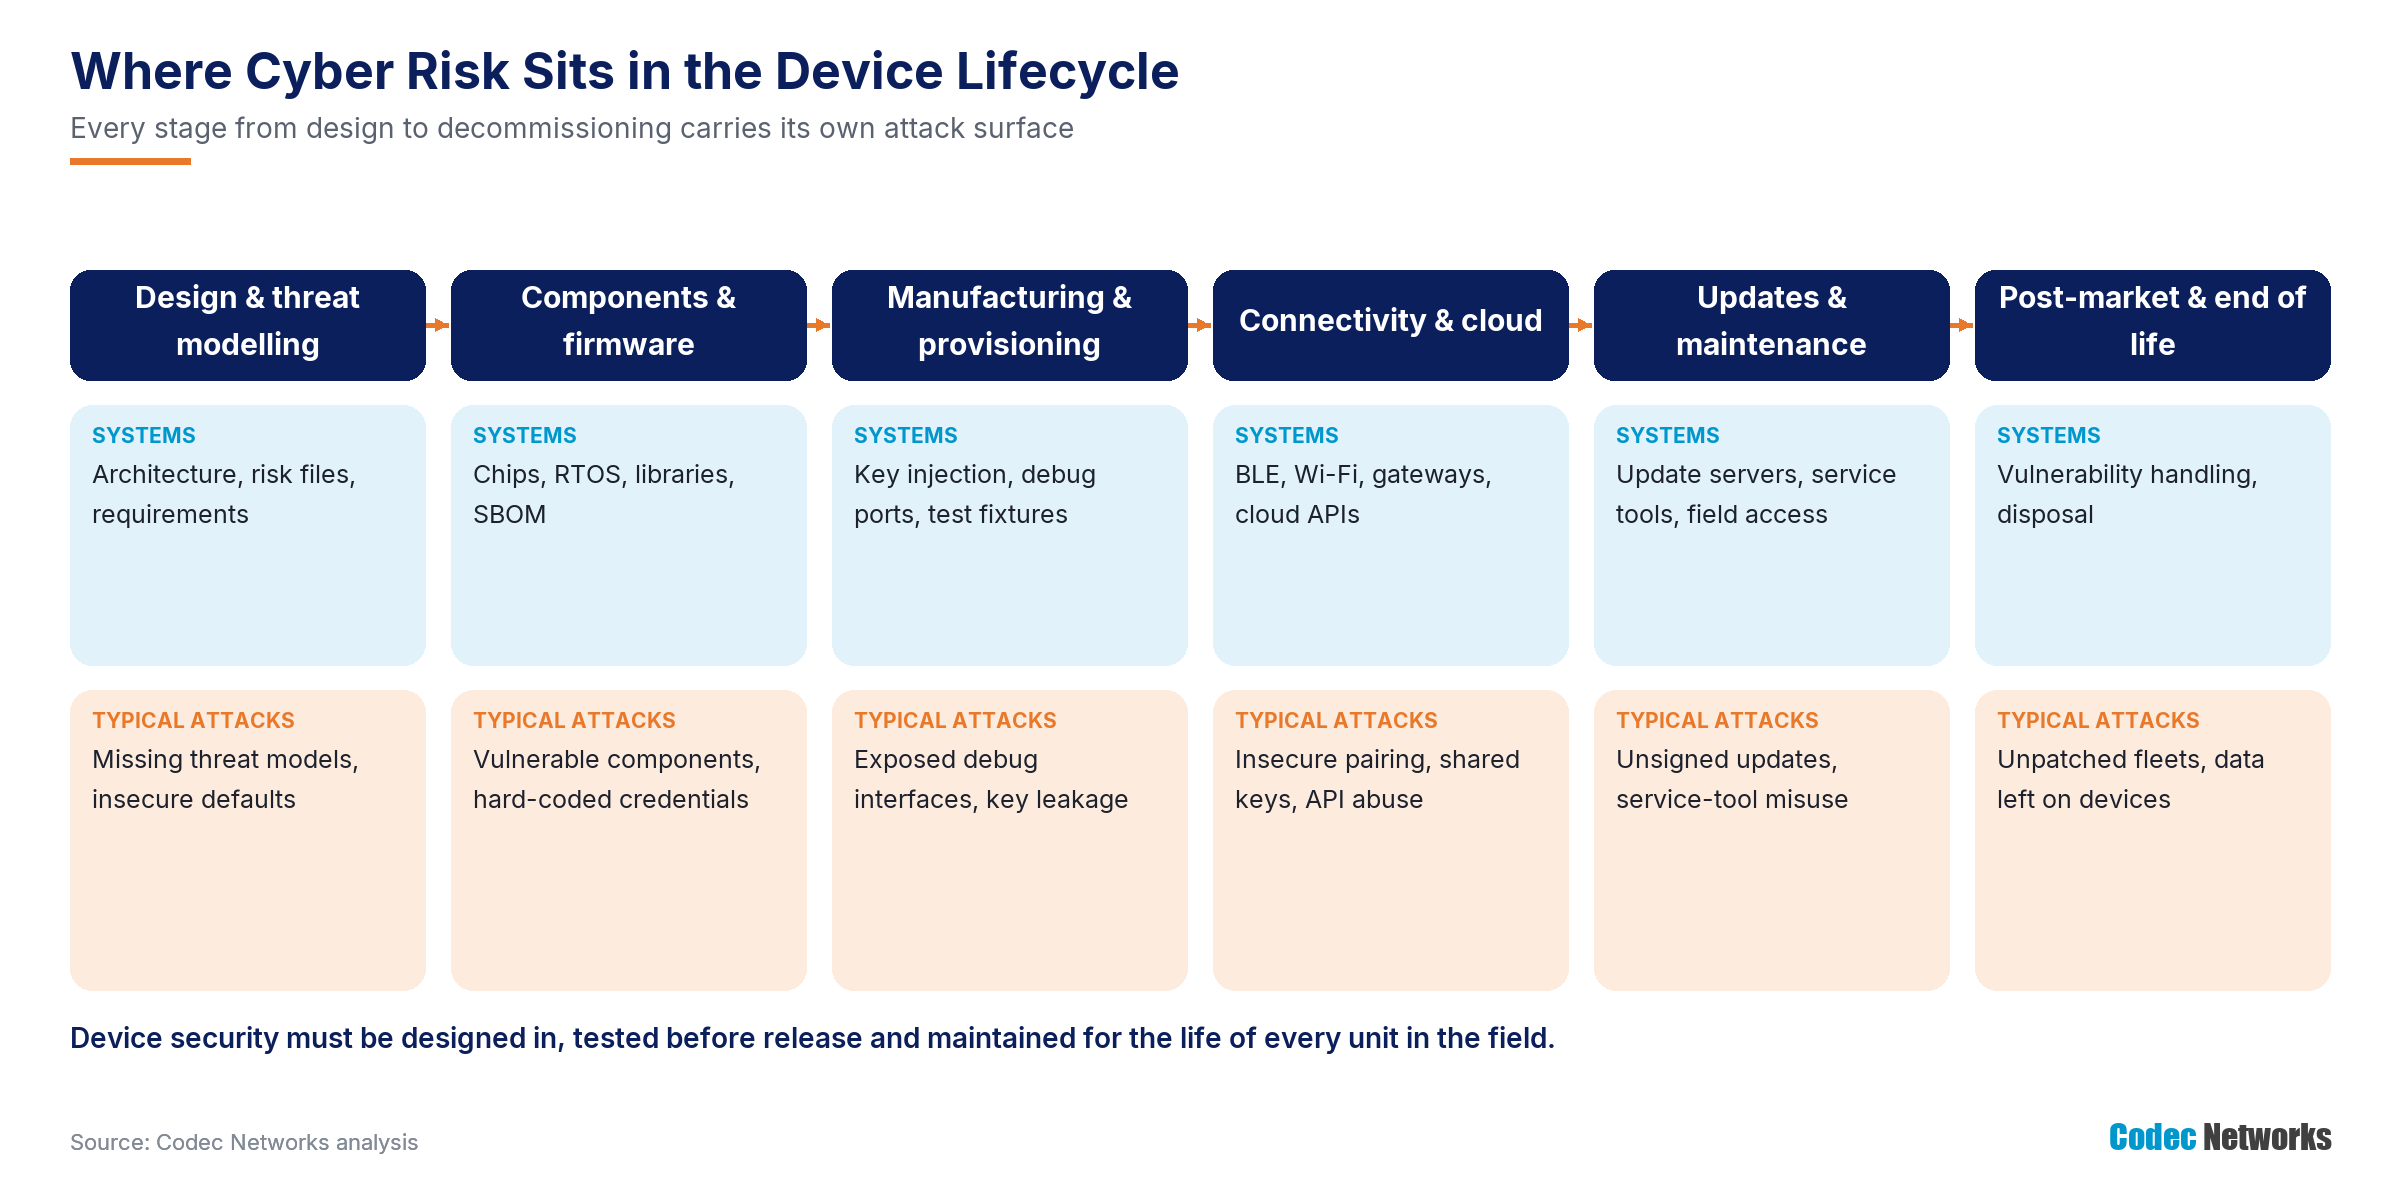
Figure 2: Where cyber risk sits in the device lifecycle.
|
Product / service |
Systems that deliver it |
Key cyber and compliance touchpoints |
|
Hardware and firmware |
MCUs, RTOS, bootloaders, libraries |
Firmware analysis, secure boot, debug lockdown |
|
Wireless interfaces |
BLE, Wi-Fi, cellular |
Pairing and protocol testing |
|
Companion apps |
Mobile apps for patients and clinicians |
Mobile app testing |
|
Cloud platforms |
Device identity, APIs, dashboards |
Cloud, API and authorisation testing |
|
Update and service |
Update servers, service tools |
Signing, hardening, access control |
|
Manufacturing and provisioning |
Key injection, test fixtures |
Unique keys, secure provisioning |
6. Trends that change the attack surface
|
Trend |
What is changing |
Security implication |
|
Regulatory evidence |
Regulators require threat models and SBOMs |
Security documentation is part of approval |
|
Home and remote care |
More devices outside hospitals |
Consumer networks and apps in scope |
|
AI-enabled devices |
AI models in diagnostics |
Model and data integrity |
|
Domestic manufacturing growth |
More Indian OEMs and exports |
Need for mature product security |
|
Longer support lifecycles |
Devices in service for many years |
Post-market vulnerability management |
7. Mapping products to Codec Networks engagements
|
If the company builds… |
Recommended starting engagement |
|
Connected bedside or imaging devices |
Firmware and network testing, hardening, service-tool review |
|
Wearables or home devices |
BLE and mobile app testing, cloud API testing |
|
Products for US or EU markets |
Threat modelling, SBOM and submission evidence |
|
Remote monitoring platforms |
Cloud, identity and API testing, platform SOC |
|
SaMD or AI software |
Application, API and AI security testing |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: Descriptions are general and based on public information available as of October 2026.