

Resources Categories
INDUSTRY FACT FILE · LOGISTICS, WAREHOUSING & SUPPLY CHAINS
Market Landscape and the Drivers of Cybersecurity Demand in Logistics and Supply Chains
The business, technology, regulatory, legal and customer forces that create cybersecurity, audit and assurance work for 3PLs, couriers, forwarders, fleets, warehouses and supply-chain platforms.
|
In this document 1. Market landscape 2. Business drivers 3. Technology drivers 4. Regulatory drivers: CERT-In, DPDP, SEBI, NCIIPC, MoRTH and government platforms 5. Legal and statutory drivers 6. How the drivers differ by operator type 7. What this means for buyers and for Codec Networks |
1. Market landscape
India's logistics sector is large, fragmented and in the middle of a policy-driven transformation. Logistics cost stood at 7.97% of GDP in 2023-24 according to the DPIIT–NCAER assessment, and PM Gati Shakti, the National Logistics Policy, ULIP, dedicated freight corridors and multimodal logistics parks aim to bring it down through integration. Grade A warehousing stock in the top eight markets is approaching 500 million square feet, express networks handle millions of parcels a day, and freight-tech platforms are digitising a trucking market still dominated by small operators. Global 3PLs and forwarders, listed Indian express and logistics groups, REIT-backed warehouse platforms and venture-funded supply-chain companies all compete—and increasingly integrate—with each other.
Cybersecurity demand follows that integration. Shippers audit their logistics partners, EU customers push NIS2 clauses down the chain, marketplaces require API security from couriers, CERT-In expects six-hour reporting and independent audits that include OT, listed companies disclose incidents, and the DPDP Act will make consignee and driver data a regulated asset. Spending is shifting from basic IT security to partner API testing, fleet and warehouse OT assurance, BEC and payment fraud controls, continuity planning and monitoring that covers hubs, fleets and SaaS.
|
7.97% Of GDP: India's logistics cost (FY24) |
~500 mn sq ft Warehousing stock in India's top eight markets (2025) |
Sep 2022 National Logistics Policy and ULIP launched |
May 2027 Most DPDP obligations take effect |
|
Market segment |
Landscape and buying behaviour |
Cybersecurity opportunity |
|
Global and listed 3PLs, express and logistics groups |
Multi-site networks, automation, formal Boards, shipper audits, SEBI disclosure |
Programme-level security, OT and fleet assurance, red teaming, SOC, Board reporting |
|
Freight forwarders and customs brokers |
Email- and document-heavy workflows, global carrier and customs integrations, mid-sized IT |
BEC and payment controls, access reviews, portal testing, managed SOC |
|
Trucking fleets and fleet aggregators |
Fragmented ownership, telematics on every vehicle, thin security teams |
Fleet and IoT assessments, platform access controls, baseline hygiene |
|
Warehouse developers and fulfilment operators |
Grade A parks, automation, multi-client sites, REIT governance |
Warehouse OT assessments, segmentation, vendor access, tenant assurance |
|
Supply-chain SaaS and freight-tech platforms |
Multi-tenant cloud platforms serving many shippers and carriers |
Secure SDLC, cloud posture, SOC 2 and ISO 27001, customer assurance |
2. Business drivers
|
Business driver |
Buying trigger |
Relevant services |
|
Operational continuity |
A ransomware incident stops hubs, filings and deliveries and accrues demurrage |
Continuity planning, segmentation, backups, SOC |
|
Shipper contracts and audits |
Manufacturers, retailers and marketplaces require security evidence |
ISO 27001, questionnaire readiness, independent audits |
|
Freight payment fraud |
BEC diverts invoices and bank-detail changes |
Payment controls, mailbox monitoring, BEC simulation |
|
Cargo security |
Leaked load and route data enables theft |
Telematics security, data minimisation, access reviews |
|
Customer trust and brand |
Consignee data leaks fuel scams against customers |
API testing, privacy programme, scam monitoring |
|
Board accountability and disclosure |
Listed companies disclose incidents; Boards own risk |
Board advisory, incident records, audit programmes |
|
Cyber and cargo insurance |
Insurers require MFA, backups, monitoring and telematics controls |
Control validation, ransomware readiness reviews |
3. Technology drivers
|
Technology driver |
Exposure created |
Codec Networks opportunity |
|
TMS, WMS and supply-chain SaaS |
Everything stops when the platform stops; multi-tenant concentration |
Platform assessments, cloud posture, continuity planning |
|
Telematics and fleet IoT |
Internet-facing platforms with location data and remote commands |
Fleet and IoT security assessment, access controls |
|
Warehouse automation |
PLCs, sorters and AS/RS on flat networks with vendor access |
OT assessment, segmentation, brokered access, monitoring |
|
Partner APIs and EDI |
Keys and integrations with shippers, carriers, merchants and government |
API testing, key scoping, rate limiting, monitoring |
|
Driver, rider and consignee apps |
OTP delivery, addresses, COD and identity at scale |
Mobile and API testing, fraud controls |
|
AI routing, forecasting and agents |
Models and agents acting on operational data |
AI risk reviews, data governance |
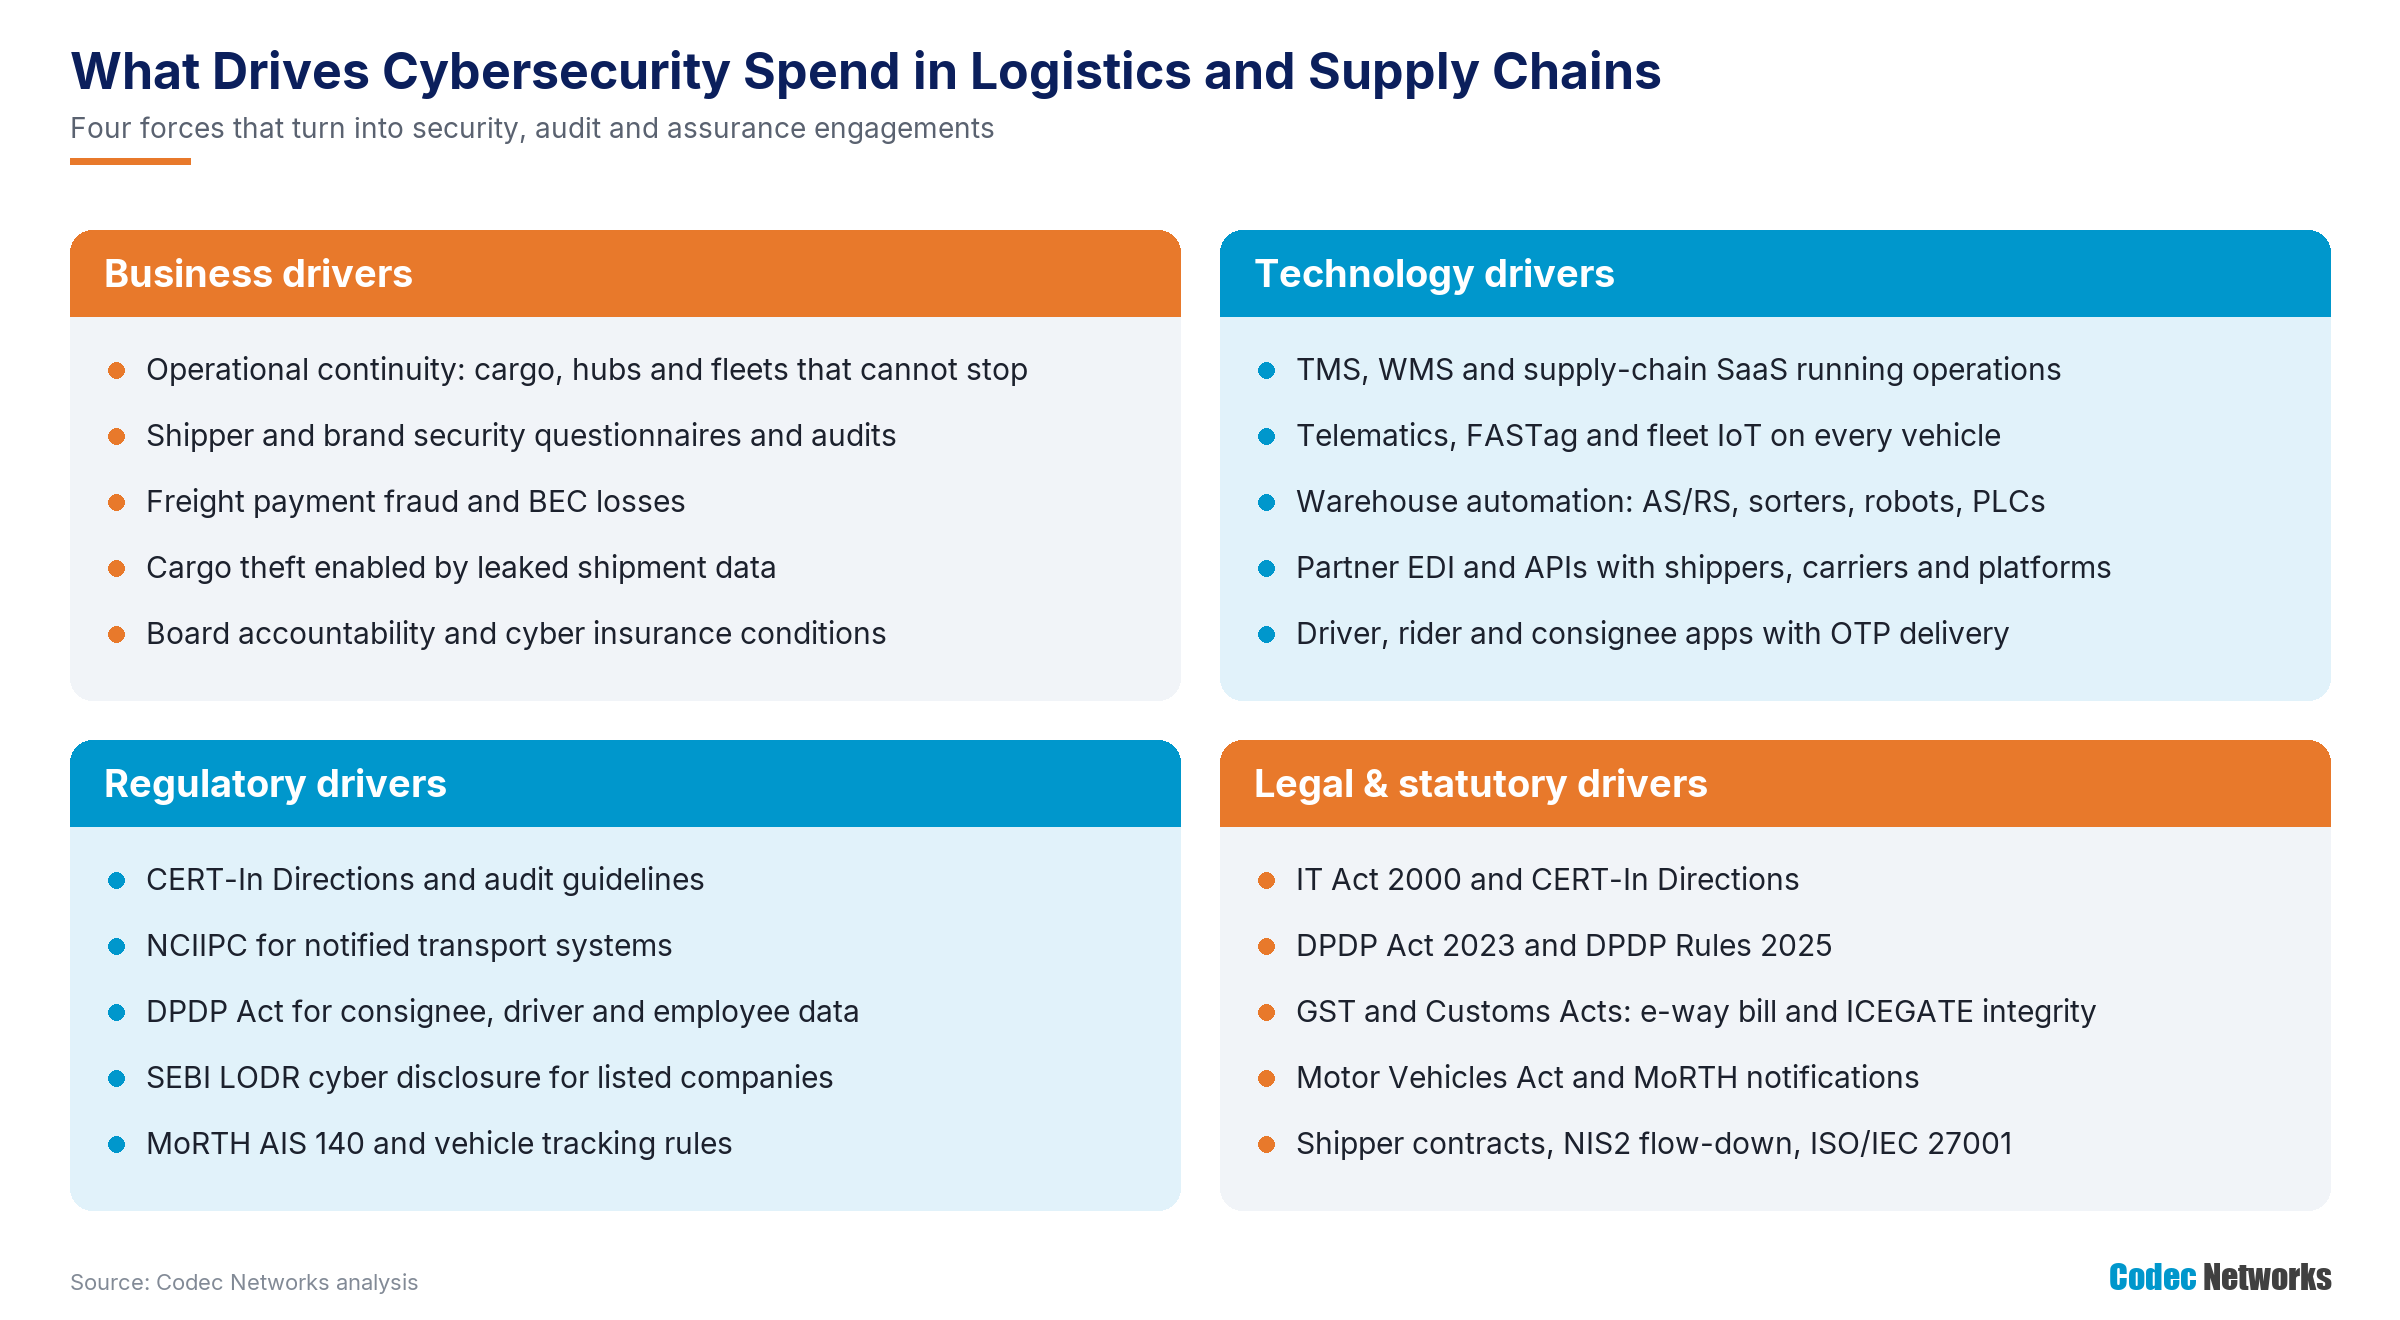
Figure 3: The four groups of drivers behind cybersecurity spending in logistics and supply chains.
4. Regulatory drivers: CERT-In, DPDP, SEBI, NCIIPC, MoRTH and government platforms
|
Instrument |
Key requirements |
|
CERT-In Directions (2022) |
Six-hour incident reporting; 180-day ICT logs in India; applies to bodies corporate including logistics companies |
|
CERT-In audit policy guidelines (July 2025) |
Risk-based, independent cyber audits covering IT, OT/ICS, cloud and applications |
|
NCIIPC (IT Act Section 70A) |
Transport is a critical sector; notified protected systems carry additional duties |
|
SEBI LODR Regulations (listed companies) |
Quarterly disclosure of cyber incidents in the corporate governance report |
|
DPDP Act 2023 and Rules 2025 |
Consignee, driver, rider, customer and employee data; most obligations from May 2027 |
|
MoRTH AIS 140 notifications; GST and Customs systems |
Vehicle location tracking devices and platforms; e-way bill and ICEGATE credentials and integrations |
|
National Logistics Policy and ULIP |
API-based integration with government logistics systems under data-sharing agreements |
|
Confirm applicability Obligations depend on listing status, services, vehicles and cargo, any NCIIPC notifications and your shipper contracts. Confirm against the official instruments. |
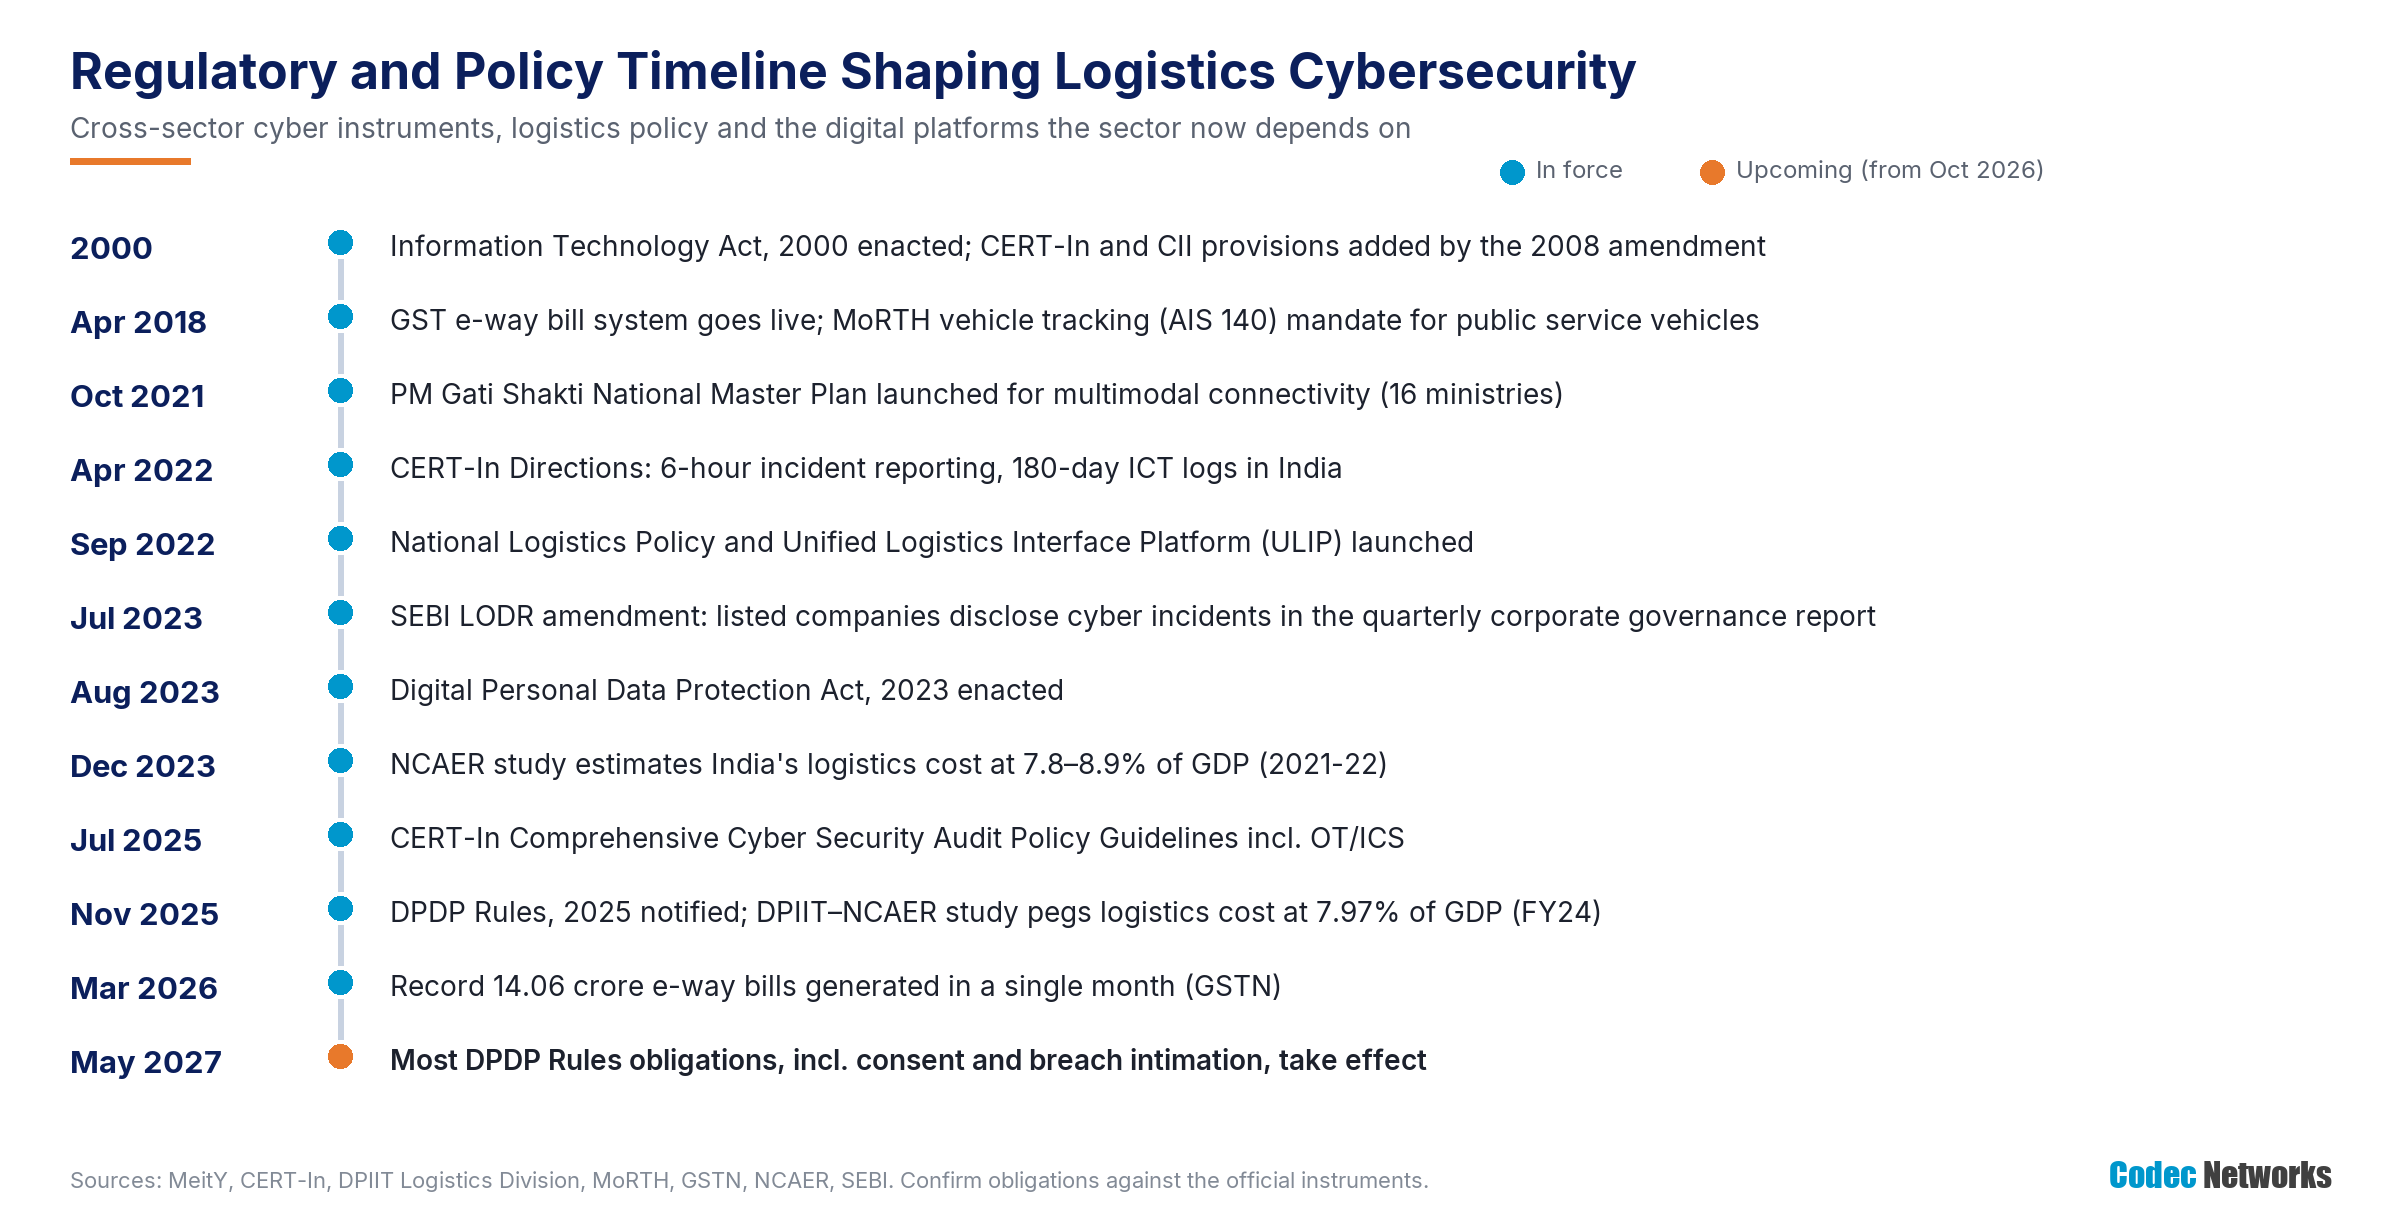
Figure 4: Regulatory and policy timeline shaping logistics cybersecurity, as of October 2026.
5. Legal and statutory drivers
|
Law or obligation |
Relevance |
Demand created |
|
IT Act, 2000 and CERT-In Directions |
Incident reporting, logging and protected systems |
SOC, logging, audits and incident response |
|
Companies Act, 2013 and SEBI LODR |
Board risk management; listed-company disclosure |
Board reporting, incident records |
|
DPDP Act, 2023 and Rules, 2025 |
Personal data of consignees, drivers, riders and employees |
Privacy programmes and breach workflows |
|
Motor Vehicles Act and MoRTH notifications |
Vehicle tracking devices, permits and fleet compliance |
Telematics security, data protection |
|
GST and Customs Acts |
E-way bill, ICEGATE filing and bonded warehouse integrity |
Credential and access controls, filing monitoring |
|
Carriage by Road Act, 2007 and contracts of carriage |
Carrier liability for goods and documentation |
Document integrity, evidence and forensics |
|
Shipper contracts, NIS2 flow-down and insurance policies |
Security clauses, audits, notification duties, warranties |
Independent testing, certifications, evidence |
6. How the drivers differ by operator type
|
Operator type |
Dominant business drivers |
Dominant technology drivers |
Principal regulatory drivers |
|
3PLs and express groups |
Continuity, shipper audits, disclosure |
Multi-client WMS/TMS, automation, apps |
CERT-In, SEBI LODR, DPDP, contracts |
|
Forwarders and brokers |
Payment fraud, customs continuity |
Email workflows, ICEGATE, carrier portals |
Customs rules, CERT-In, DPDP |
|
Trucking fleets |
Cargo security, insurance |
Telematics, FASTag, driver apps |
MoRTH AIS 140, GST e-way bill, CERT-In |
|
Warehouse operators |
Site uptime, tenant assurance |
WMS, AS/RS, PLCs, vendor access |
CERT-In audits incl. OT, contracts |
|
Supply-chain platforms |
Customer trust, concentration risk |
Multi-tenant cloud, APIs |
CERT-In, DPDP as processor, SOC 2/ISO |
7. What this means for buyers and for Codec Networks
|
Customer buying need |
Recommended offering |
Natural recurring engagement |
|
“Would ransomware stop our hubs and our customs filings?” |
Continuity review: dependency mapping, segmentation, backups, playbooks |
Annual resilience testing and exercises |
|
“Our shipper sent a security questionnaire before renewal.” |
Questionnaire readiness and ISO 27001 gap assessment |
Annual recertification support |
|
“A customer paid our invoice to a fraudster's account.” |
BEC investigation, payment controls, mailbox hardening |
Mailbox monitoring and annual simulation |
|
“Merchants and carriers hold keys to our APIs.” |
Partner API testing, key scoping, monitoring |
Release testing and quarterly reviews |
|
“Our automation vendor has a VPN into the warehouse.” |
Warehouse OT and vendor access review |
Vendor access recertification |
|
“We need 24x7 monitoring that covers hubs and fleets.” |
Logistics SOC with BEC and API detection |
Continuous monitoring |
|
“We need an independent cyber audit.” |
CERT-In-aligned IT/OT audit |
Annual audits |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: This document is general industry guidance based on public information available as of October 2026. It is not legal, safety or regulatory advice. Obligations differ by company size, listing status, services, customers and any NCIIPC notifications; confirm them against the official CERT-In, MeitY, SEBI, NCIIPC, MoRTH, GST and Customs instruments and your shipper and platform contracts.