

Resources Categories
INDUSTRY FACT FILE · FINTECH
Applicable Cybersecurity Services and Codec Networks Bundles for Fintech
How Codec Networks services and bundled service models help fintechs resolve their threats, satisfy regulated partners and regulators, and keep pace with release cycles.
|
In this document 1. Our approach 2. Mapping threats to services 3. Codec Networks service catalogue for the sector 4. Codec Networks bundles for the sector 5. Sector programmes built from the bundles 6. Packages: Foundation, Assurance and Continuous Resilience 7. Regulatory requirement-to-bundle mapping 8. Threat-to-bundle coverage matrix 9. Delivery methodology and deliverables 10. Why Codec Networks 11. Annex: indicative commercial ranges |
1. Our approach
Fintechs need security that is fast, automated where possible and documented in a way their partners accept. Codec Networks works on four principles:
- Shift left: build testing into CI/CD so most issues are caught before release.
- Test what attackers test: APIs, authorisation, secrets, cloud and business logic first.
- Produce partner-ready evidence: reports structured for bank, NBFC, investor and enterprise due diligence.
- Prove closure: retest at sprint speed and track remediation transparently.
2. Mapping threats to services
The table maps the 18 threats identified in Document 4 of this set to the Codec Networks services that help mitigate them.
|
Threat / challenge |
Applicable Codec Networks services |
Intended outcome |
|
Broken API authorisation |
API security testing (REST, GraphQL, SOAP), secure code review, threat modelling |
Authorisation flaws found before release |
|
Excessive data exposure |
API response review, data minimisation assessment |
Smaller breach impact |
|
Leaked keys and secrets |
Secrets scanning, vault and rotation review, CI/CD security |
No long-lived exposed credentials |
|
Cloud misconfiguration |
Cloud security audit, Kubernetes and serverless testing, IAM review |
Continuous posture visibility |
|
Insecure webhooks |
Webhook signature and replay testing, partner integration testing |
Trusted partner callbacks |
|
Account takeover |
Mobile app testing, IAM & MFA bypass testing, session security review |
Stronger authentication and session controls |
|
Synthetic identity and deepfake KYC |
AI-powered deepfake testing, onboarding fraud simulation |
Onboarding that resists deepfakes |
|
Mule accounts and fraud rings |
Fraud analytics review, SOC fraud use cases |
Earlier detection of coordinated fraud |
|
Consent abuse and over-collection |
DPDPA readiness, consent-flow review, DPIA |
Purpose-bound data use |
|
Malicious or vulnerable SDKs |
Software composition analysis, SDK review, SBOM |
Known and trusted components |
|
CI/CD and supply-chain compromise |
Pipeline security review, build integrity, dependency controls |
Trusted builds |
|
Business-logic abuse |
Business-logic and workflow testing, process-bypass testing |
Closed loopholes in limits and rewards |
|
Fake apps and brand abuse |
Brand and rogue-app monitoring, takedown support |
Faster removal of impersonation |
|
Insider and support-access misuse |
Privileged and support-access review, insider simulation |
Accountable access to customer data |
|
Ransomware and extortion |
Ransomware simulation, backup testing, IR retainer |
Tested recovery |
|
AI and LLM abuse |
AI/LLM security testing, prompt-injection testing, ISO 42001 readiness |
Safer AI features |
|
Partner and vendor compromise |
Third-party risk management, vendor assessments |
Visible and managed supplier risk |
|
Weak logging and detection |
Managed SOC, cloud and API log monitoring, playbooks |
Reliable 6-hour reporting |
3. Codec Networks service catalogue for the sector
|
Service line |
Sector-relevant services |
|
Security Vulnerability Assessment & Penetration Testing |
Web, mobile (iOS/Android, SDK) and API (REST, GraphQL, SOAP) testing; cloud-native app testing; cloud infrastructure testing; partner-ready VAPT reports |
|
Application security & DevSecOps |
SAST, DAST and SCA in CI/CD, secure code review, threat modelling, supply-chain testing, CI/CD pipeline security |
|
Offensive security & fraud simulation |
Red teaming, IAM & MFA bypass testing, business-logic and approval-workflow bypass testing, AI-powered deepfake testing |
|
Information security consulting & compliance |
Applicability assessments for NBFC-AAs and NBFC-P2Ps, partner-readiness programmes, ISO/IEC 27001:2022, SOC 2 Type 1/2 readiness, PCI DSS where applicable |
|
Data privacy & protection |
DPDPA readiness, consent management and privacy design, DPIA, data discovery, AI and big-data privacy risk assessment |
|
24/7 Managed SOC & threat monitoring |
SOC-as-a-Service, cloud security monitoring, SIEM, EDR/XDR, dark web intelligence, fraud-signal use cases |
|
Cyber forensics & threat analysis |
Cloud forensics, breach triage, malware analysis, mobile forensics |
|
Emerging technology security |
AI and LLM security, ISO 42001 readiness, smart contract audits, post-quantum readiness |
|
Centre for Professional Excellence (CoPE) |
Secure coding and security awareness for engineering and operations teams |
4. Codec Networks bundles for the sector
Eleven of the twelve bundles in the Codec Networks Bundled Service Models apply directly to fintech companies; the Global Cyber Back-Office SPV Program (Bundle 12) is offered separately for international clients.
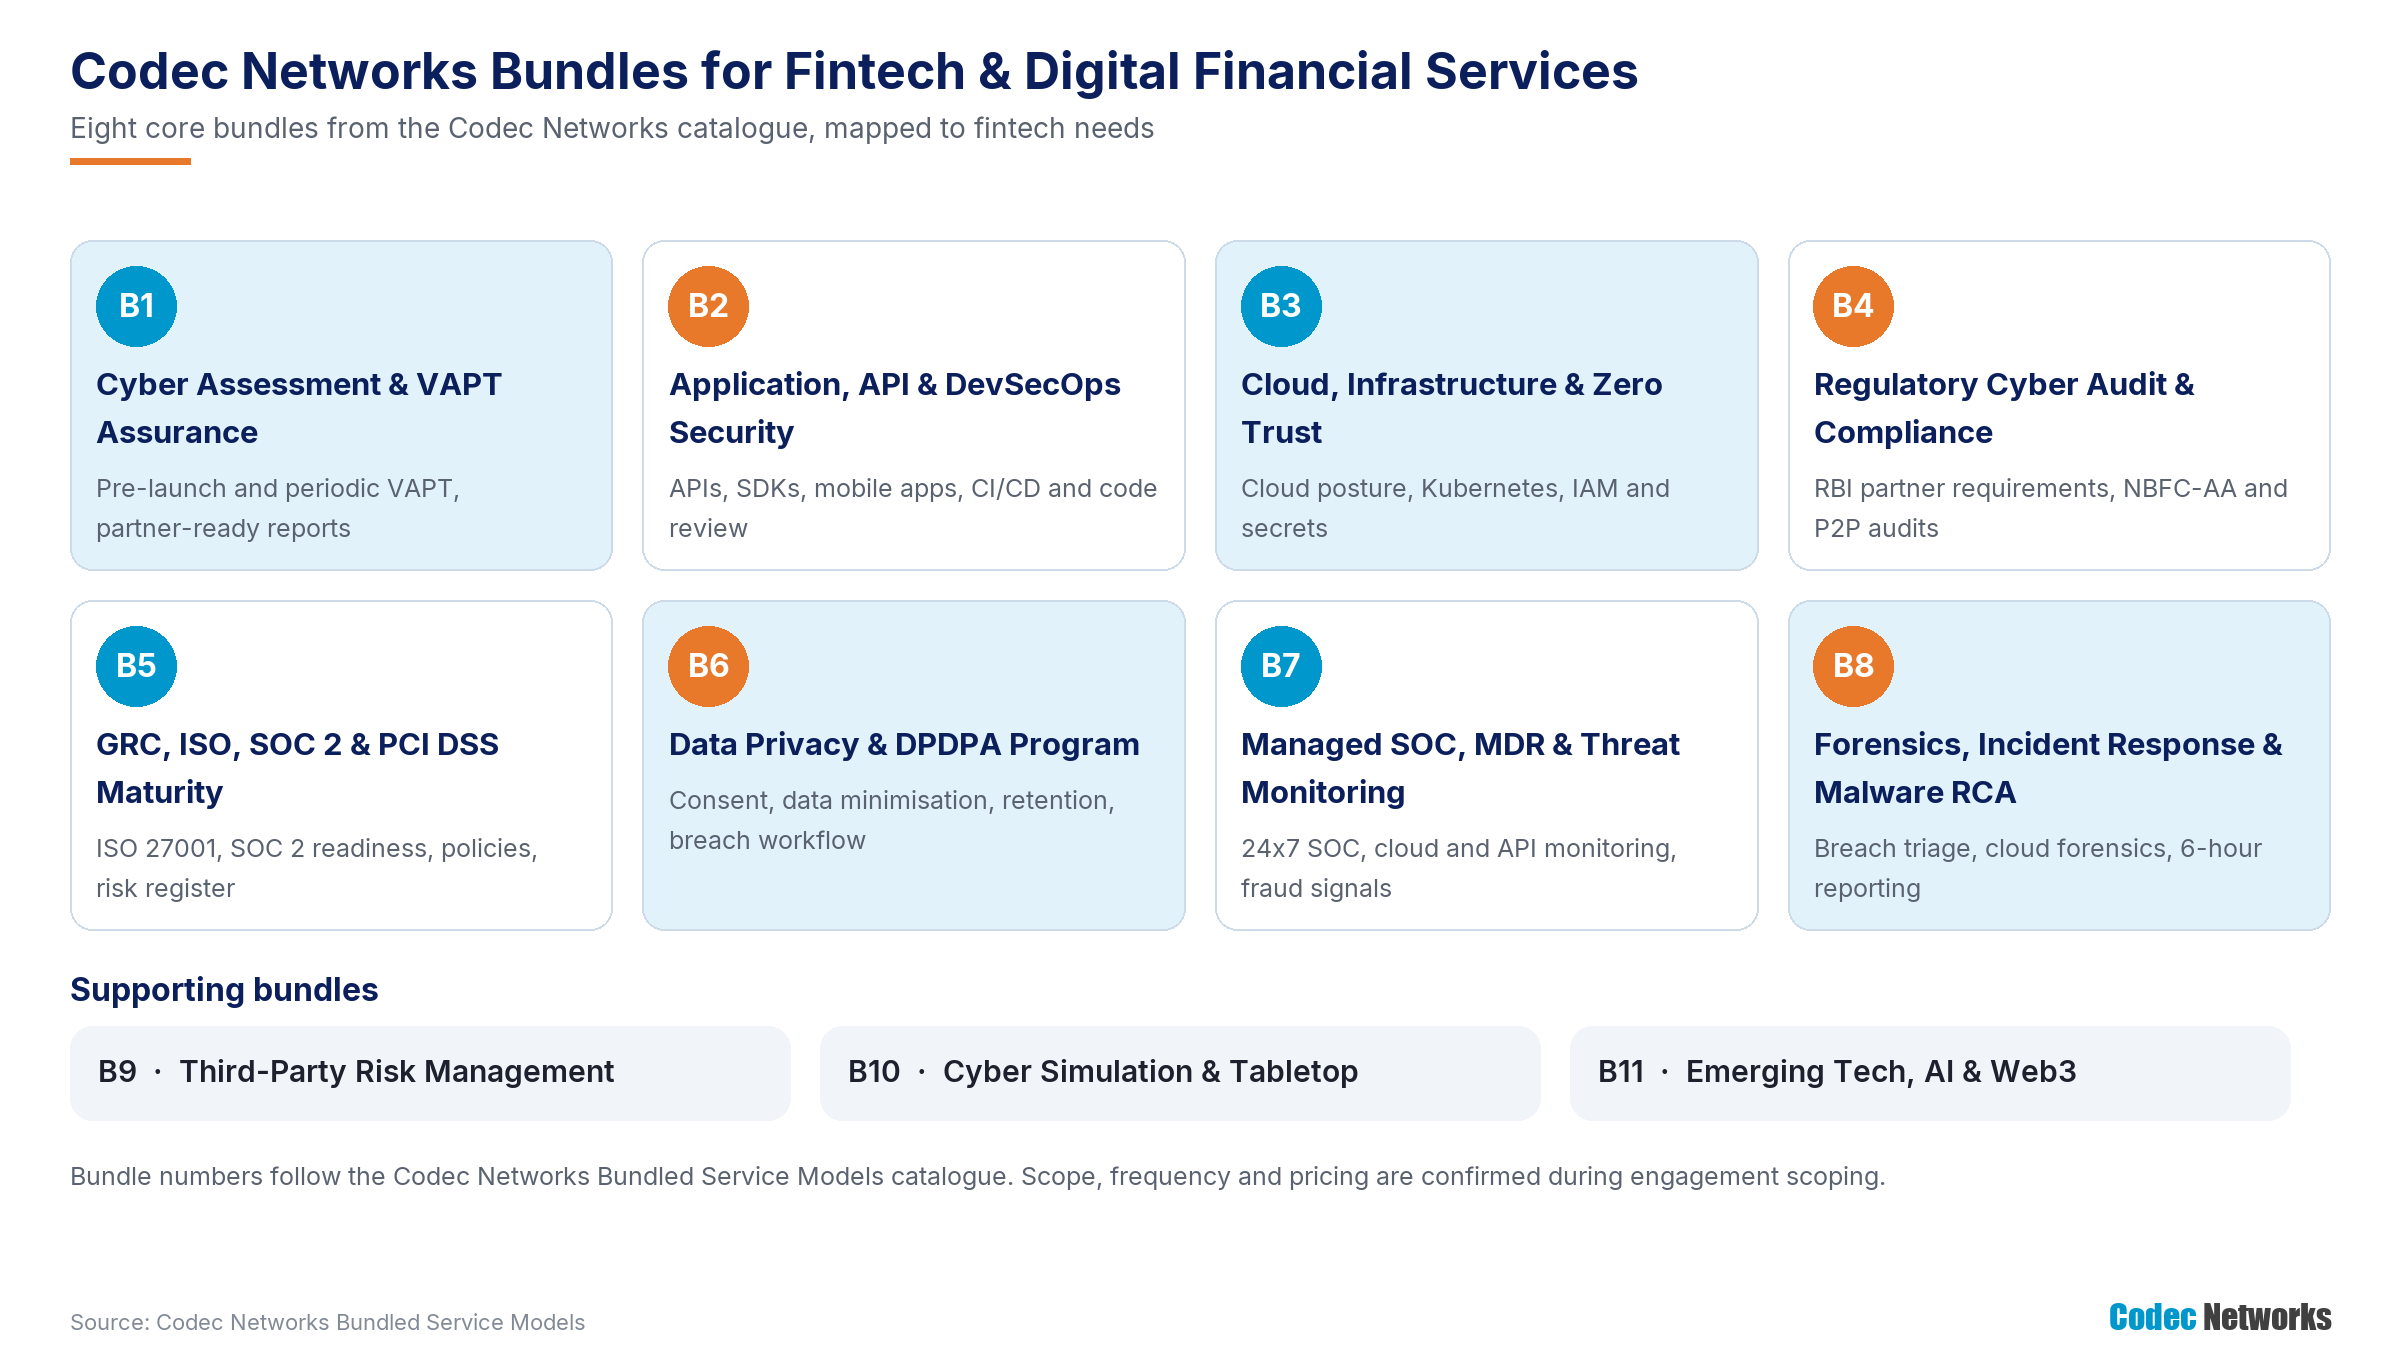
Figure 6: Codec Networks bundles applied to the sector.
|
Bundle |
Name |
Sector-relevant scope |
Best suited for |
Key deliverables |
|
B1 |
Cyber Assessment & VAPT Assurance Program |
Pre-launch and periodic VAPT, partner-ready reports, retest |
All fintechs before partner go-live |
VAPT reports, remediation tracker, retest report |
|
B2 |
Application, API & DevSecOps Security Program |
APIs, webhooks, SDKs, mobile apps, CI/CD, code review |
API-first and mobile-first fintechs |
API risk report, code review report, DevSecOps maturity report |
|
B3 |
Cloud, Infrastructure & Zero Trust Security Program |
Cloud posture, Kubernetes, IAM, secrets, Zero Trust |
Cloud-native platforms |
Cloud posture report, IAM and secrets review |
|
B4 |
Regulatory Cybersecurity Audit & Compliance Assurance Program |
Applicability for NBFC-AAs and NBFC-P2Ps; partner requirement mapping |
Licensed fintechs and partner-led models |
Applicability matrix, gap assessment, evidence index |
|
B5 |
GRC, ISO, SOC 2 & Cyber Maturity Program |
ISO 27001, SOC 2 readiness, policies, risk register |
Fintechs selling to banks and enterprises |
Readiness report, policy framework, control tracker |
|
B6 |
Data Privacy, DPDPA & Data Protection Program |
Consent, minimisation, retention, DPIA, breach workflow |
All fintechs handling personal and financial data |
Privacy gap assessment, data inventory, DPIA |
|
B7 |
Managed SOC, MDR & Continuous Threat Monitoring Program |
24x7 SOC, cloud and API monitoring, fraud signals |
Fintechs without 24x7 in-house monitoring |
SOC reports, incident tickets, MTTD/MTTR |
|
B8 |
Digital Forensics, Incident Response & Malware RCA Program |
Breach triage, cloud forensics, reporting support |
Any fintech facing a suspected compromise |
Triage report, forensic RCA |
|
B9 |
Third-Party Risk Management & Supply Chain Cyber Risk Program |
Vendor, SDK and partner assessments |
Fintechs with many vendors and SDKs |
Vendor risk register, remediation plan |
|
B10 |
Cyber Simulation, Awareness, Tabletop & Crisis Readiness Program |
Fraud, phishing, deepfake and tabletop simulations |
Founders, engineering, risk and support teams |
Simulation and tabletop reports |
|
B11 |
Emerging Technology, AI, Web3 & Future Security Program |
AI/LLM testing, ISO 42001, smart contracts |
Fintechs deploying AI or tokenisation |
AI/LLM risk assessment |
5. Sector programmes built from the bundles
Codec Networks packages the catalogue bundles into six fintech programmes that match common buying needs.
|
Programme |
Built from bundles |
Challenges addressed |
|
Partner-Ready Assurance |
B1, B5, B4 |
Bank, NBFC, investor and enterprise due diligence |
|
API and Product Security |
B2, B1 |
API authorisation, webhooks, SDKs and business logic |
|
Cloud and Secrets Assurance |
B3, B7 |
Misconfiguration, leaked keys and cloud monitoring |
|
Fraud and Identity Resilience |
B10, B11, B7 |
Synthetic identities, deepfakes, ATO and mule rings |
|
Consent and Privacy Programme |
B6, B9 |
DPDP readiness, AA consent and vendor data access |
|
Detect and Respond |
B7, B8 |
24x7 monitoring and 6-hour reporting |
6. Packages: Foundation, Assurance and Continuous Resilience
|
Package element |
Foundation |
Assurance |
Continuous Resilience |
|
Typical fintech |
Seed and early-stage fintechs |
Growth-stage fintechs and NBFC-AAs |
Scale-ups and multi-partner platforms |
|
Testing |
B1: pre-launch API and app VAPT |
B1 + B2: release-based testing and DevSecOps |
B1 + B2 + B10: continuous testing, red teaming, fraud simulation |
|
Regulatory and GRC |
B5: ISO 27001 / SOC 2 gap review |
B4 + B5: applicability and partner evidence |
B4 + B5 + B9: multi-partner assurance, vendor programme |
|
Cloud and privacy |
B3: cloud quick review |
B3 + B6: cloud posture and DPDPA readiness |
B3 + B6 + B11: continuous assurance, privacy and AI governance |
|
Monitoring and response |
Optional IR retainer (B8) |
B7: extended-hours SOC + B8 |
B7: 24x7 SOC with fraud correlation + B8 |
|
Reporting |
Partner questionnaire pack |
Consolidated risk and remediation reporting |
Board and investor reporting |
7. Regulatory requirement-to-bundle mapping
|
Requirement (source) |
How Codec Networks helps |
Bundle |
|
Digital Lending Directions 2025: lenders accountable for LSPs; borrower-data restrictions |
LSP security assessment, data-flow and API review |
B2, B6 |
|
RBI 2026 NBFC Directions: requirements by layer and size for NBFC-AAs and NBFC-P2Ps |
Applicability assessment, IS audit, gap remediation |
B4 |
|
RBI 2026 NBFC Directions: cyber incidents to RBI on DAKSH within six hours |
IR retainer, playbooks and reporting support |
B7, B8 |
|
Partners' outsourcing and cybersecurity Directions: due diligence, audit and RBI access rights |
Partner-ready evidence, VAPT and certifications |
B1, B5 |
|
CERT-In Directions: 6-hour reporting, 180-day logs, clock sync, point of contact |
Logging review, SOC and IR readiness |
B7 |
|
DPDP Act and Rules: consent, minimisation, safeguards, breach intimation |
DPDPA programme, consent review, breach drills |
B6 |
|
AA ecosystem technical standards and SRO codes |
Consent-flow, cryptography and API testing |
B2, B4 |
|
KYC directions including V-CIP (for partners) |
Onboarding and deepfake resistance testing |
B10, B11 |
|
Auditor eligibility and independence Where a regulator, standard or contract requires CERT-In empanelled or independent auditors, Codec Networks—CERT-In empanelled for information security auditing services—confirms eligibility and independence in each proposal. |
8. Threat-to-bundle coverage matrix
|
Threat / challenge |
Primary bundle |
Supporting bundles |
|
Broken API authorisation |
B2 |
B1 |
|
Excessive data exposure |
B2 |
B6 |
|
Leaked keys and secrets |
B3 |
B2 |
|
Cloud misconfiguration |
B3 |
B7 |
|
Insecure webhooks |
B2 |
B7 |
|
Account takeover |
B2 |
B7, B10 |
|
Synthetic identity and deepfake KYC |
B10 |
B11 |
|
Mule accounts and fraud rings |
B7 |
B8 |
|
Consent abuse |
B6 |
B9 |
|
Malicious SDKs |
B2 |
B9 |
|
CI/CD compromise |
B2 |
B3 |
|
Business-logic abuse |
B2 |
B10 |
|
Fake apps |
B7 |
B10 |
|
Insider and support access |
B7 |
B3 |
|
Ransomware |
B7 |
B8, B10 |
|
AI and LLM abuse |
B11 |
B2 |
|
Partner and vendor compromise |
B9 |
B3 |
|
Weak logging and detection |
B7 |
B8 |
“Primary” and “supporting” indicate suggested combinations, not guaranteed mitigation or complete coverage.
9. Delivery methodology and deliverables
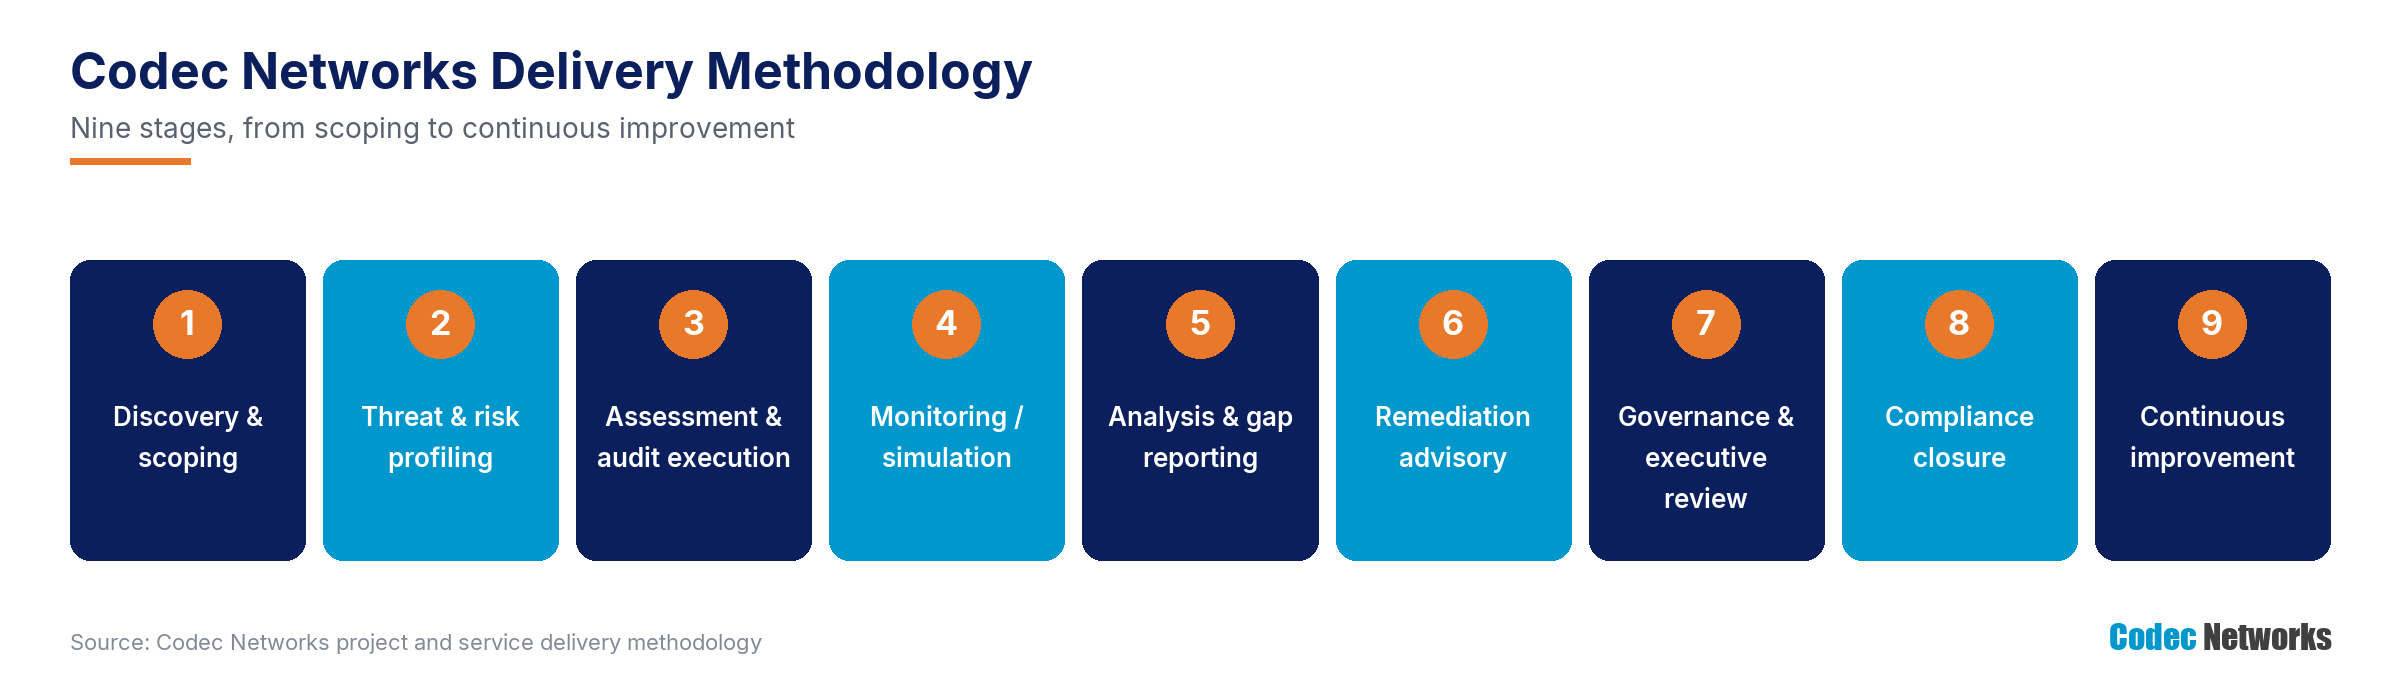
Figure 7: The Codec Networks delivery methodology.
Typical deliverables include partner-ready VAPT reports with evidence and CVSS ratings, an API inventory and risk register, a cloud posture report, a DevSecOps maturity report, an applicability matrix for licensed entities, a privacy gap assessment and an evidence pack for bank, NBFC, investor and enterprise reviews.
10. Why Codec Networks
- CERT-In empanelled for information security auditing services, and empanelled with NICSI for application audit and compliance services (start-up category).
- Certified to ISO 9001:2015, ISO/IEC 27001:2022 and ISO/IEC 20000-1:2018.
- Full stack: VAPT, regulatory audit, managed SOC, forensics, privacy and Board advisory from one partner, so findings, monitoring and closure stay connected.
- Fintech depth: API, webhook, SDK, cloud-native and fraud-scenario testing delivered at release speed, with partner-ready reporting.
- Recognised frameworks and tools: OWASP ASVS/MASVS and API Top 10, MITRE ATT&CK, NIST CSF, ISO 27001 and PCI DSS; tools such as Burp Suite, Nessus, Metasploit, Prowler and leading SIEM/EDR platforms.
- Certified people: CEH, OSCP, CPENT, CISA, ISO 27001 LA/LI, CHFI, CTIA and ECIH professionals.
Annex: Indicative commercial ranges
For internal sales reference only—remove this annex before sharing externally. Ranges are taken from the Codec Networks Bundled Service Models and are subject to scoping, asset counts, frequency and service levels.
|
Bundle |
Package examples and indicative ranges |
|
B1 VAPT Assurance |
Essential ₹1.5–5 lakh; Professional ₹5–15 lakh; Enterprise ₹15–40 lakh; Annual retainer ₹25 lakh–₹1.5 crore |
|
B2 AppSec & DevSecOps |
API Quick Check ₹2–6 lakh; AppSec Professional ₹8–20 lakh; DevSecOps Maturity ₹12–35 lakh; Secure SDLC retainer ₹3–15 lakh/month |
|
B3 Cloud & Zero Trust |
Cloud Essential ₹3–8 lakh; Professional ₹8–25 lakh; Enterprise ₹25–75 lakh; Continuous assurance ₹2–10 lakh/month |
|
B4 Regulatory Audit |
Gap review ₹5–15 lakh; Full regulatory audit ₹15–50 lakh; Multi-framework audit ₹30 lakh–₹1.25 crore; Annual retainer ₹3–20 lakh/month |
|
B5 GRC, ISO, SOC 2 |
ISO readiness ₹5–15 lakh; ISO implementation ₹15–45 lakh; SOC 2 readiness ₹15–60 lakh; GRC retainer ₹2–12 lakh/month |
|
B6 Privacy & DPDPA |
Quick assessment ₹3–10 lakh; Implementation ₹10–40 lakh; DPO-as-a-Service ₹2–8 lakh/month; Privacy retainer ₹3–15 lakh/month |
|
B7 Managed SOC |
Starter ₹2–5 lakh/month; Professional ₹5–15 lakh/month; Enterprise ₹15–50 lakh/month; co-managed per FTE/shift |
|
B8 Forensics & IR |
Triage ₹3–15 lakh; Full investigation ₹15–75 lakh; Ransomware response ₹25 lakh–₹1.5 crore; IR retainer ₹5–50 lakh/year |
|
B9 TPRM |
₹25,000–₹2 lakh per vendor; batch pricing for 50–500 vendors; retainer ₹3–25 lakh/month |
|
B10 Simulation & Tabletop |
Awareness ₹1–5 lakh; Phishing simulation ₹2–10 lakh; Tabletop ₹5–20 lakh; Cyber war-game ₹15–75 lakh; Annual retainer ₹10 lakh–₹1 crore/year |
|
B11 Emerging Tech |
AI/LLM risk review ₹5–25 lakh; Smart contract audit ₹5–50 lakh; Emerging tech retainer ₹5–25 lakh/month |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: Service scope, deliverables, monitoring coverage and service levels are confirmed during engagement scoping. Services support risk reduction and assurance but do not guarantee prevention of all cyber incidents or regulatory compliance. Regulatory references are summaries; confirm against the official instruments applicable to each entity.