

Resources Categories
INDUSTRY FACT FILE · CREDIT INFORMATION & FINANCIAL DATA
Market Landscape and the Drivers of Cybersecurity Demand in Credit Information
The business, technology, regulatory, legal and statutory forces that create cybersecurity, audit and assurance work for credit bureaus, analytics firms, KYC utilities and data processors.
|
In this document 1. Market landscape 2. Business drivers 3. Technology drivers 4. Regulatory drivers: CICRA, RBI, SEBI and CERT-In 5. Legal and statutory drivers 6. How the drivers differ by player type 7. What this means for buyers and for Codec Networks |
1. Market landscape
India's credit information market is built around RBI-registered credit bureaus that receive data from banks, NBFCs and other lenders, supported by analytics firms, KYC utilities, identity providers and data processors. Growth in digital lending and API-based decisioning has increased both the volume of credit data and the number of parties that touch it.
|
Fortnightly Credit data reporting to CICs since January 2025 |
31 Jul 2026 RBI cyber Directions issued, incl. CICs |
180 days ICT log retention in India under CERT-In |
May 2027 Most DPDP obligations take effect |
|
Market segment |
Landscape and buying behaviour |
Cybersecurity opportunity |
|
Credit bureaus |
Large data platforms, many members, high regulatory scrutiny |
IS audits, red teaming, SOC, member assurance |
|
Analytics and data processors |
Data-heavy, cloud-based, client-driven |
Access and leakage assessments, cloud reviews, ISO 27001 |
|
KYC utilities and KRAs |
Identity data at national scale |
CSCRF assessments, VAPT, access reviews |
|
Lenders and fintechs |
Both supply and consume credit data |
Submission integrity and API security |
2. Business drivers
|
Business driver |
Buying trigger |
Relevant services |
|
Regulatory compliance |
RBI Directions, CICRA safeguards, SEBI CSCRF |
Gap assessments, IS audits |
|
Data trust and accuracy |
Disputes and data-quality issues damage confidence |
Integrity assessments, reconciliation reviews |
|
Fraud prevention |
Stolen reports fuel loan fraud and scams |
API monitoring, member security reviews |
|
Client and partner requirements |
Lenders and partners demand security evidence |
ISO 27001, audit reports, questionnaires |
|
Reputation |
A large leak becomes national news |
Leakage assessments, incident readiness |
3. Technology drivers
|
Technology driver |
Exposure created |
Codec Networks opportunity |
|
Report APIs |
Credential theft and unauthorised pulls |
API security testing and abuse monitoring |
|
Cloud data lakes |
Misconfiguration and broad access |
Cloud and data-lake reviews |
|
Analytics sandboxes |
Insider exports and data leakage |
DLP, masking and access reviews |
|
Bulk file transfers |
Tampering and interception |
Integrity and secure transfer reviews |
|
AI scoring models |
Model tampering and training-data misuse |
AI governance and security testing |
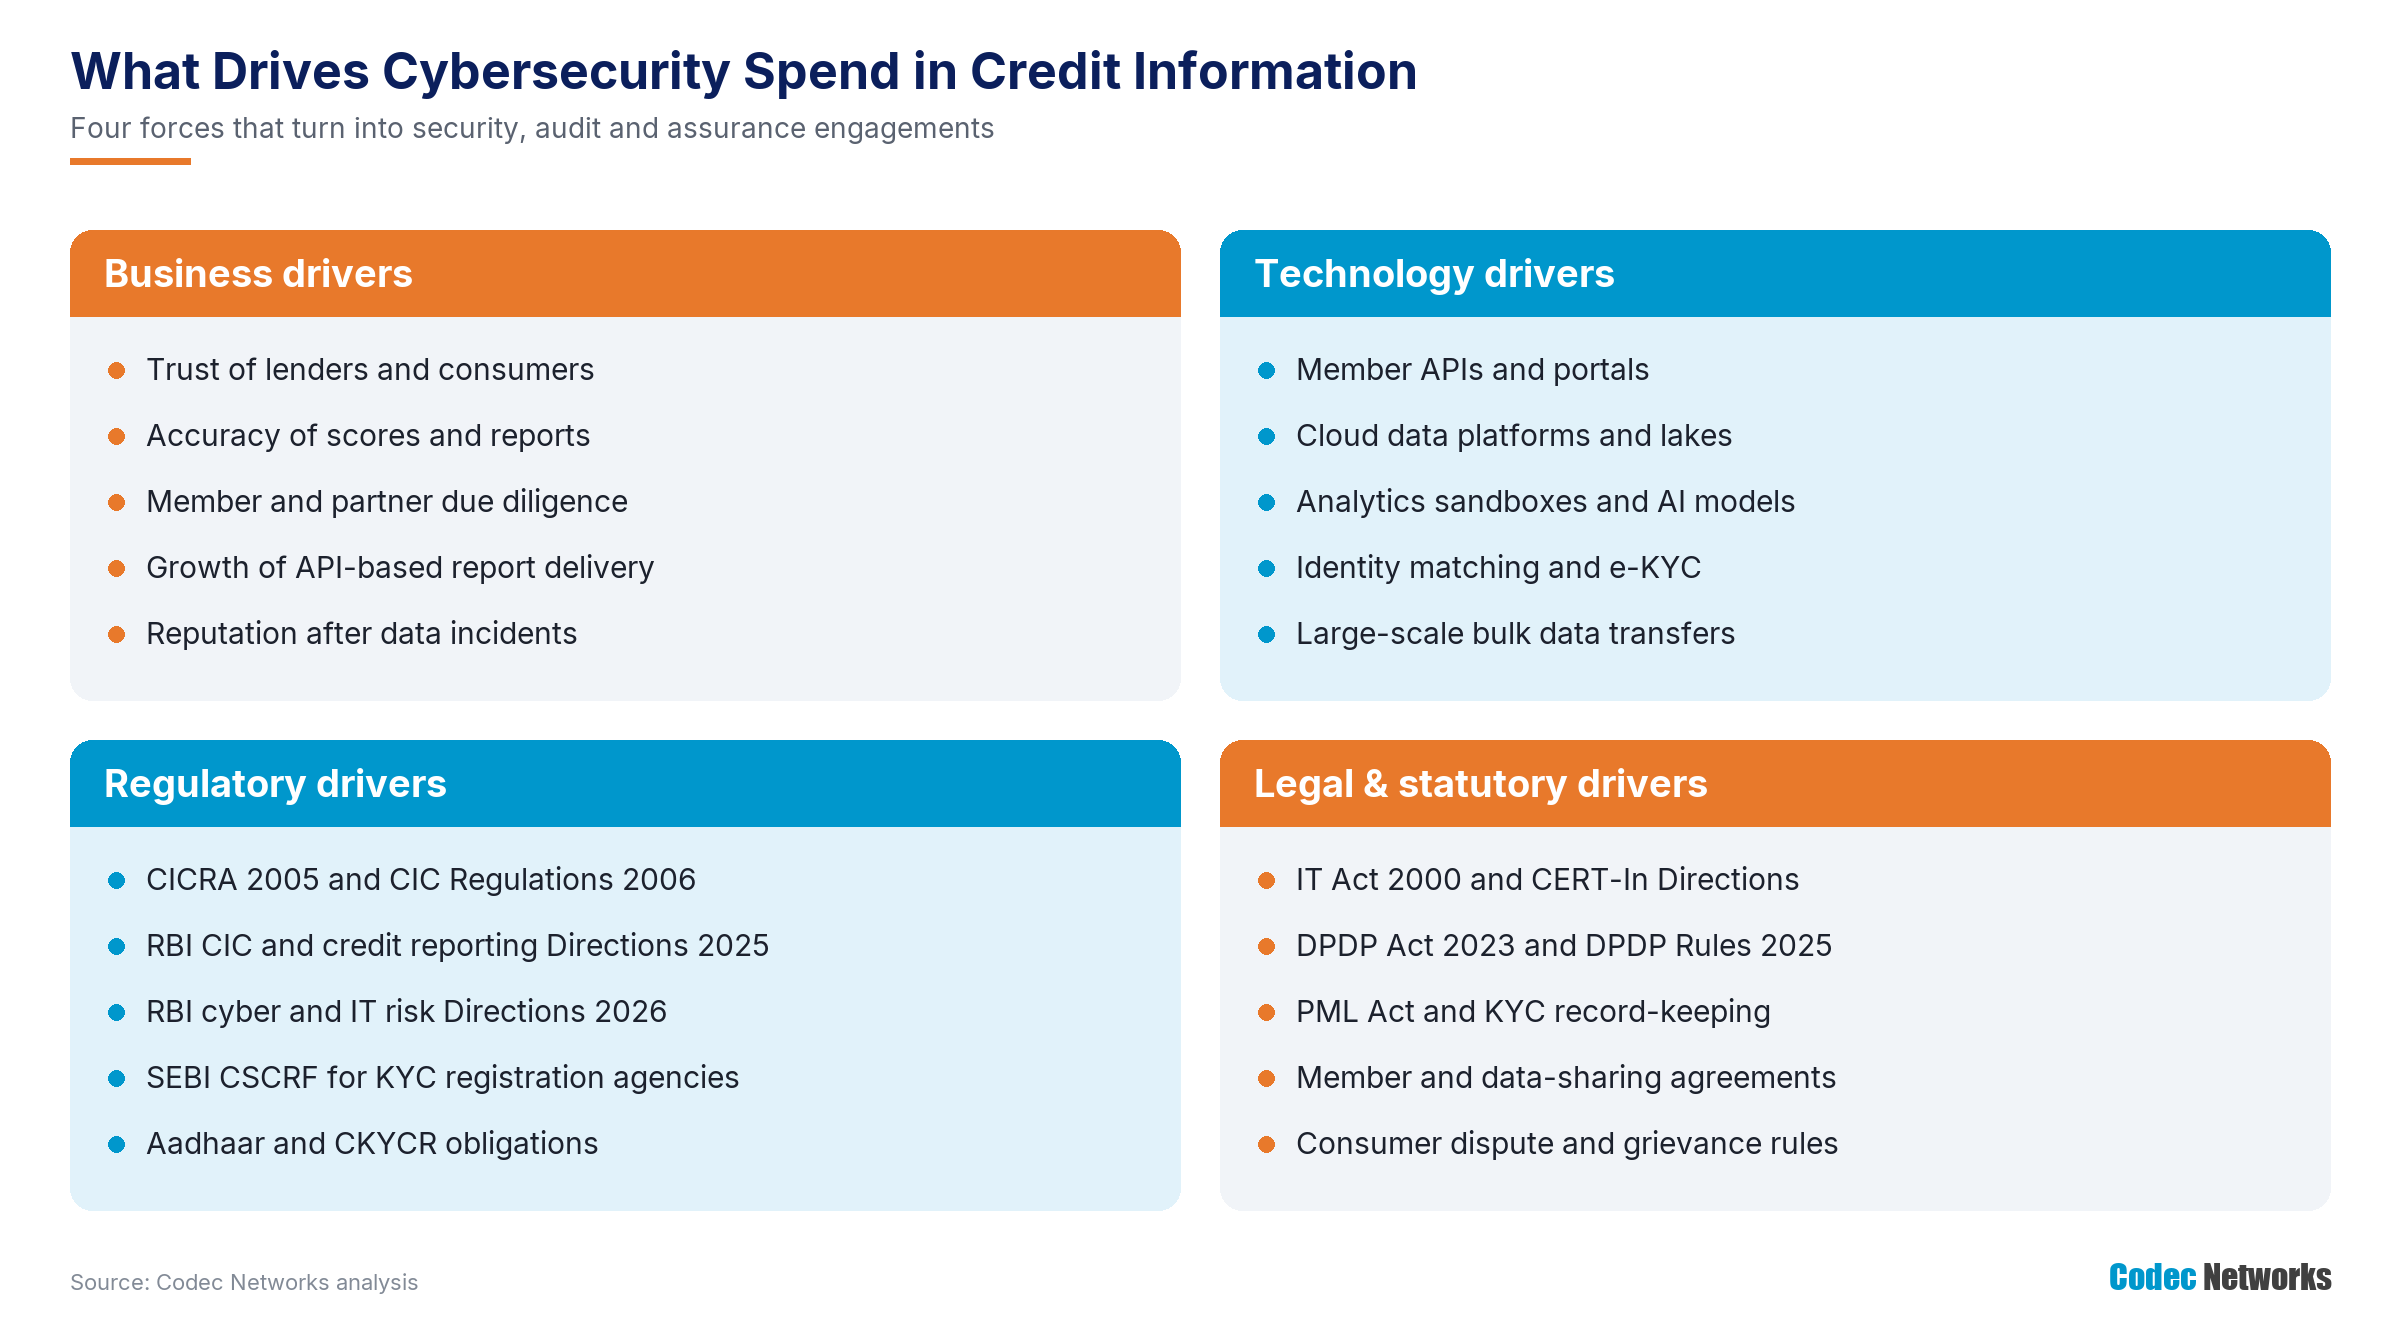
Figure 3: The four groups of drivers behind cybersecurity spending in credit information.
4. Regulatory drivers: CICRA, RBI, SEBI and CERT-In
|
Instrument |
Key requirements |
|
CICRA 2005 and CIC Regulations 2006 |
Security safeguards and privacy principles for credit information Rules on accuracy, access, disclosure and disputes |
|
RBI (CIC) Directions and credit reporting Directions, 2025 |
Governance and operational requirements for CICs Fortnightly reporting by credit institutions |
|
RBI cyber, technology risk and assurance Directions (31 July 2026) |
As reported, includes a Direction for CICs covering cybersecurity, technology risk, resilience and assurance |
|
SEBI CSCRF |
Cyber resilience requirements for SEBI-regulated entities, including KYC registration agencies |
|
CERT-In Directions (2022) |
Six-hour incident reporting; 180-day ICT logs in India |
|
Confirm against the official texts RBI's July 2026 Directions are summarised from public sources. Confirm the Direction applicable to your entity, its scope and its timelines against the official RBI text. |
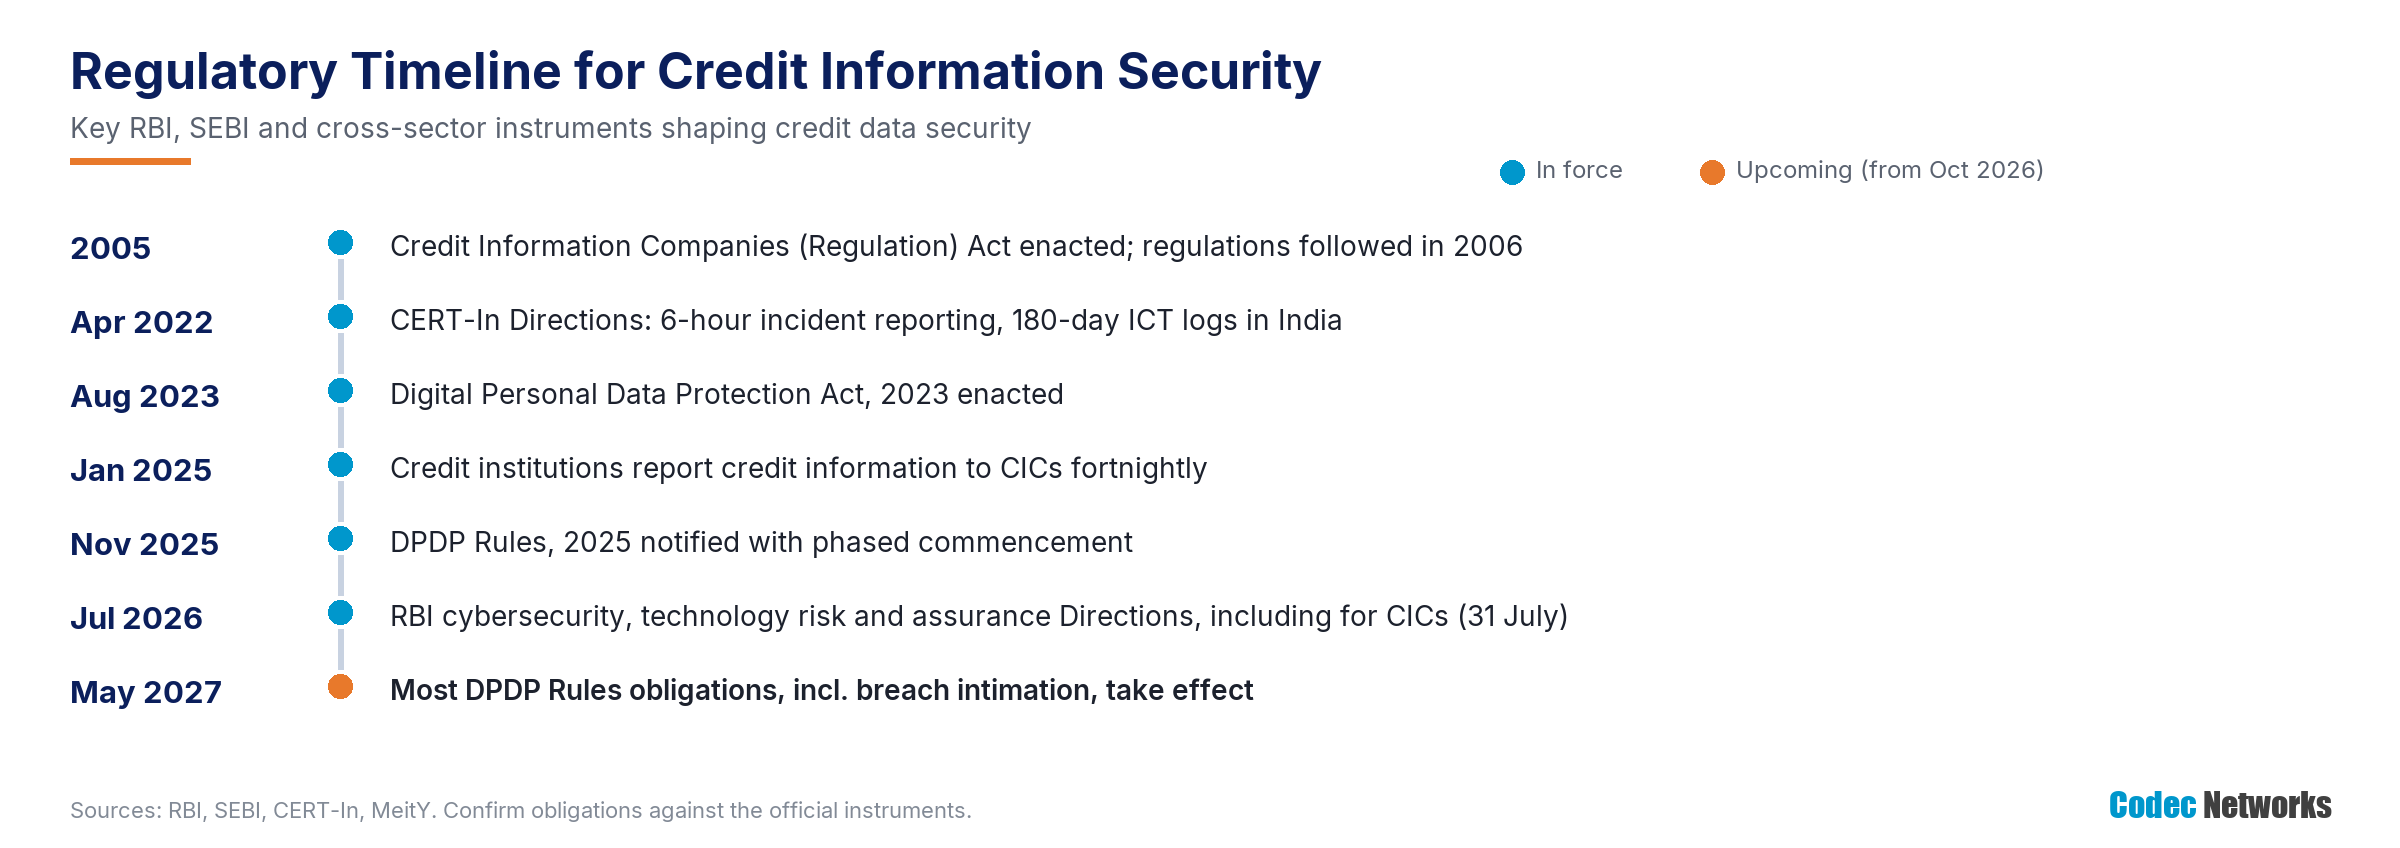
Figure 4: Regulatory timeline for credit information security, as of October 2026.
5. Legal and statutory drivers
|
Law or obligation |
Relevance |
Demand created |
|
Credit Information Companies (Regulation) Act, 2005 |
Registration, safeguards and privacy principles |
IS audits and access controls |
|
IT Act, 2000 and CERT-In Directions |
6-hour reporting; 180-day logs |
Logging, SOC, incident readiness |
|
DPDP Act, 2023 and Rules, 2025 |
Consent, purpose limits, safeguards, breach intimation |
Privacy programmes and leakage controls |
|
Prevention of Money Laundering Act, 2002 |
KYC record-keeping obligations |
Secure KYC record management |
|
Contracts |
Member, data-sharing and vendor agreements |
Assurance evidence and audits |
6. How the drivers differ by player type
|
Player type |
Dominant business drivers |
Dominant technology drivers |
Principal regulatory drivers |
|
Credit bureaus |
Trust, accuracy, fraud prevention |
APIs, data lakes, matching engines |
CICRA, RBI Directions, DPDP |
|
Analytics firms |
Client trust, contracts |
Sandboxes, cloud, AI |
Contracts, DPDP, RBI flow-down |
|
KYC utilities and KRAs |
Identity integrity |
KYC repositories and APIs |
PMLA, SEBI CSCRF, DPDP |
|
Data processors |
Client requirements |
Cloud and pipelines |
Contracts, DPDP, CERT-In |
7. What this means for buyers and for Codec Networks
|
Customer buying need |
Recommended offering |
Natural recurring engagement |
|
“Who can access and export our data?” |
Data access control review |
Annual access recertification |
|
“Are our report APIs safe?” |
API security testing |
Release-linked testing |
|
“Could our data be tampered with?” |
Data integrity assessment |
Periodic pipeline reviews |
|
“Are we aligned to RBI's new Directions?” |
Gap assessment and IS audit |
Annual audit and closure tracking |
|
“Are we ready for DPDP?” |
DPDPA programme and leakage assessment |
Periodic privacy reviews |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: This document is general industry guidance based on public information available as of October 2026. RBI 2026 Direction details are summarised from reported sources. Confirm obligations against the official RBI, SEBI, CERT-In and MeitY instruments before making compliance decisions.