

Resources Categories
INDUSTRY FACT FILE · CREDIT INFORMATION & FINANCIAL DATA
Applicable Cybersecurity Services and Codec Networks Bundles for Credit Data Firms
How Codec Networks services and bundled service models help credit bureaus, analytics firms, KYC utilities and data processors resolve their threats and meet RBI, SEBI, CERT-In and DPDP obligations.
|
In this document 1. Our approach 2. Mapping threats to services 3. Codec Networks service catalogue for the sector 4. Codec Networks bundles for the sector 5. Sector programmes built from the bundles 6. Packages: Foundation, Assurance and Continuous Resilience 7. Regulatory requirement-to-bundle mapping 8. Threat-to-bundle coverage matrix 9. Delivery methodology and deliverables 10. Why Codec Networks 11. Annex: indicative commercial ranges |
1. Our approach
Credit data firms need assurance that follows the data. Codec Networks works on four principles:
- Map to obligations: align every engagement to CICRA, RBI Directions, SEBI CSCRF, CERT-In and DPDP.
- Follow the data: test submission, storage, analytics, delivery and disputes end to end.
- Protect integrity as well as confidentiality: treat tampering as seriously as theft.
- Prove closure: track remediation and keep evidence for auditors, regulators and members.
2. Mapping threats to services
The table maps the 18 threats identified in Document 4 of this set to the Codec Networks services that help mitigate them.
|
Threat / challenge |
Applicable Codec Networks services |
Intended outcome |
|
Bulk data exfiltration |
DLP and egress testing, segmentation review, SOC monitoring |
Early detection of bulk movement |
|
API abuse |
API security testing, consent and purpose checks review |
Pulls only for valid purposes |
|
Member credential theft |
Secrets management review, member assurance |
Revocable, monitored credentials |
|
Submission-file tampering |
Data integrity assessment, reconciliation review |
Trustworthy credit histories |
|
Insider misuse |
Access reviews, UEBA, insider simulation |
Visible, accountable access |
|
Identity fraud |
Onboarding and e-KYC flow testing |
Harder synthetic identities |
|
Ransomware |
Ransomware simulation, backup testing, EDR validation |
Tested recovery |
|
Cloud misconfiguration |
Cloud and data-lake review, posture monitoring |
No public exposure |
|
Test and analytics leakage |
Leakage assessment, masking review |
Controlled data copies |
|
Vendor compromise |
Third-party risk management |
Enforceable vendor controls |
|
Consumer account takeover |
Portal and app testing |
Stronger consumer accounts |
|
Fraudulent disputes |
Dispute workflow testing |
Verified corrections |
|
Model tampering |
AI and model governance review |
Controlled model changes |
|
Phishing and impersonation |
Brand monitoring, takedown, awareness |
Faster removal of fakes |
|
Weak detection |
Managed SOC, playbooks, tabletop exercises |
Reliable 6-hour reporting |
|
Insecure file transfer |
Secure transfer and encryption review |
Protected bulk transfers |
|
Excessive retention |
Retention and deletion review |
Smaller breach impact |
|
Recovery failure |
BCP/DR drills |
Proven recovery |
3. Codec Networks service catalogue for the sector
|
Service line |
Sector-relevant services |
|
Security Vulnerability Assessment & Penetration Testing |
Member portals, report and upload APIs, consumer apps, data platforms and infrastructure |
|
Information security audit & compliance |
IS audits aligned to CICRA and RBI Directions, SEBI CSCRF for KRAs, ISO/IEC 27001:2022 |
|
Offensive security & simulation |
Insider, phishing and ransomware simulations, red teaming, tabletop exercises |
|
Data privacy & protection |
DPDPA readiness, consent and purpose reviews, data inventory, DLP, retention |
|
24/7 Managed SOC & threat monitoring |
SIEM, UEBA and API-abuse use cases for pulls, exports and privileged activity |
|
Cyber forensics |
Leak and insider investigations, incident triage, root-cause analysis |
|
Third-party risk management |
Member, processor, analytics and cloud vendor assessments |
|
Cloud security |
Data-lake and warehouse reviews, IAM, posture monitoring |
|
Emerging technology security |
AI and scoring-model governance and security testing |
4. Codec Networks bundles for the sector
Eleven of the twelve bundles in the Codec Networks Bundled Service Models apply directly to credit information and financial data firms; the Global Cyber Back-Office SPV Program (Bundle 12) is offered separately for international clients.
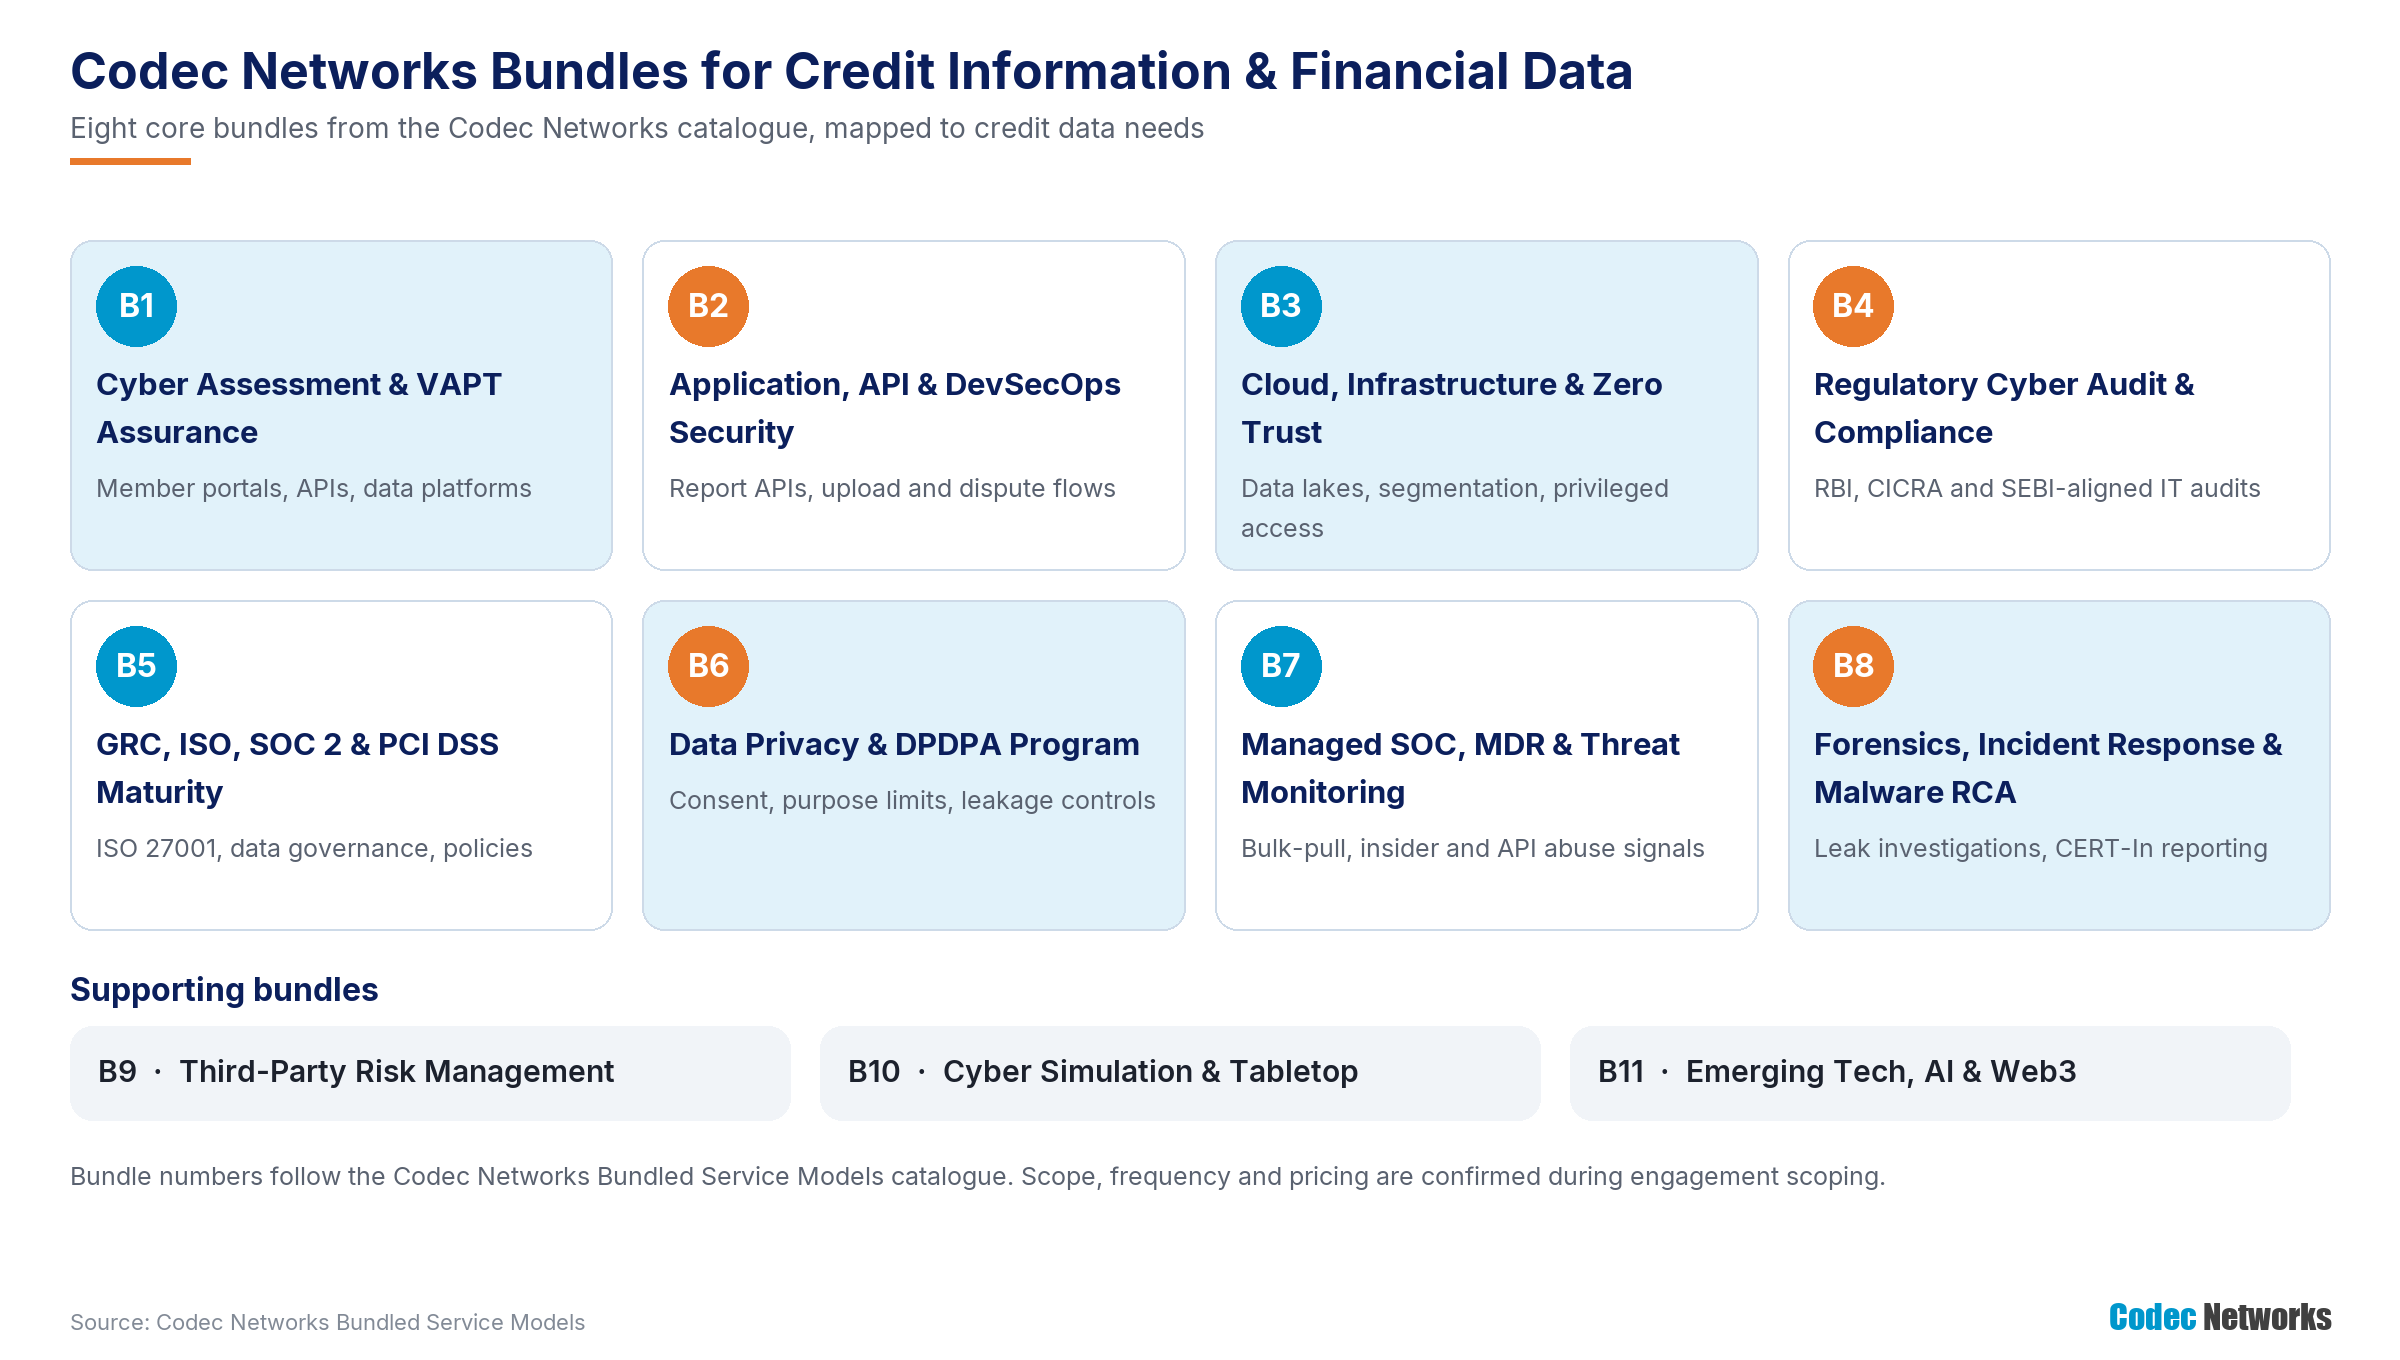
Figure 6: Codec Networks bundles applied to the sector.
|
Bundle |
Name |
Sector-relevant scope |
Best suited for |
Key deliverables |
|
B1 |
Cyber Assessment & VAPT Assurance Program |
Portals, APIs and data platform PT with retest |
All credit data firms |
PT reports and closure tracker |
|
B2 |
Application, API & DevSecOps Security Program |
Report, upload and dispute API testing; secure SDLC |
Bureaus and data platforms |
Application and API risk report |
|
B3 |
Cloud, Infrastructure & Zero Trust Security Program |
Data lakes, segmentation, privileged access |
Cloud-based data platforms |
Cloud review report |
|
B4 |
Regulatory Cybersecurity Audit & Compliance Assurance Program |
IS audits for RBI, CICRA and SEBI CSCRF |
Bureaus, KYC utilities, KRAs |
Audit report, gap matrix |
|
B5 |
GRC, ISO, SOC 2 & Cyber Maturity Program |
ISO 27001, data governance, policies |
Analytics firms and processors |
Maturity scorecard |
|
B6 |
Data Privacy, DPDPA & Data Protection Program |
Consent, purpose, inventory, DLP, retention |
All firms ahead of May 2027 |
Privacy gap assessment |
|
B7 |
Managed SOC, MDR & Continuous Threat Monitoring Program |
24x7 SOC with pull, export and insider signals |
Bureaus and large platforms |
SOC reports, MTTD/MTTR |
|
B8 |
Digital Forensics, Incident Response & Malware RCA Program |
Leak and insider investigations |
Any firm facing exposure |
Forensic report and RCA |
|
B9 |
Third-Party Risk Management & Supply Chain Cyber Risk Program |
Member, processor and vendor assessments |
Bureaus and platforms with many connections |
Vendor risk assessments |
|
B10 |
Cyber Simulation, Awareness, Tabletop & Crisis Readiness Program |
Insider, phishing and ransomware exercises |
Leadership, data and operations teams |
Exercise reports |
|
B11 |
Emerging Technology, AI, Web3 & Future Security Program |
AI and scoring-model security |
Analytics firms and bureaus using AI |
AI risk assessment |
5. Sector programmes built from the bundles
Codec Networks packages the catalogue bundles into six credit data programmes.
|
Programme |
Built from bundles |
Challenges addressed |
|
Regulatory Assurance Programme |
B4, B5, B1 |
RBI, CICRA and SEBI obligations |
|
Data Access & Insider Control |
B6, B7, B10 |
Insider exports and privileged misuse |
|
API & Member Security |
B2, B9, B7 |
Credential abuse and unauthorised pulls |
|
Data Integrity Assurance |
B2, B4 |
Submission tampering and pipeline integrity |
|
Leakage Prevention |
B6, B3 |
Cloud, test and analytics exposure |
|
Incident Readiness |
B7, B8, B10 |
Detection, response and 6-hour reporting |
6. Packages: Foundation, Assurance and Continuous Resilience
|
Package element |
Foundation |
Assurance |
Continuous Resilience |
|
Typical organisation |
Analytics firms and processors |
KYC utilities, KRAs, mid-sized platforms |
Credit bureaus and large data platforms |
|
Testing |
B1: annual PT |
B1 + B2: PT, API and integrity testing |
B1 + B2 + B10: red teaming and simulations |
|
Audit and GRC |
B5: ISO 27001 pack |
B4 + B5: IS audit, gap closure |
B4 + B5 + B9: audit, member assurance |
|
Cloud and privacy |
B6: DPDPA quick assessment |
B3 + B6: cloud and DPDPA readiness |
B3 + B6 + B11: continuous assurance, AI governance |
|
Monitoring and response |
IR retainer (B8) |
B7: managed SOC + B8 |
B7: SOC with insider and API signals + B8 |
|
Reporting |
Compliance checklist |
Management reporting |
Board and regulator reporting |
7. Regulatory requirement-to-bundle mapping
|
Requirement (source) |
How Codec Networks helps |
Bundle |
|
Security safeguards and privacy principles (CICRA 2005; CIC Regulations 2006) |
IS audit and data access control review |
B4 |
|
RBI cyber, technology risk and assurance Directions for CICs (July 2026, as reported) |
Gap assessment and audit support |
B4, B5 |
|
SEBI CSCRF for KRAs |
CSCRF gap assessment and audit support |
B4 |
|
Secure report delivery and access |
API and application security testing |
B2 |
|
Incidents to CERT-In within six hours; 180-day logs |
SOC, IR retainer, reporting support |
B7, B8 |
|
Third-party and outsourcing controls |
Vendor and member assurance |
B9 |
|
DPDP consent, safeguards, breach intimation |
DPDPA programme, DLP and leakage review |
B6 |
|
Data accuracy and integrity |
Data integrity assessment |
B2, B4 |
|
Auditor eligibility and independence Where a regulator, standard or contract requires CERT-In empanelled or independent auditors, Codec Networks—CERT-In empanelled for information security auditing services—confirms eligibility and independence in each proposal. |
8. Threat-to-bundle coverage matrix
|
Threat / challenge |
Primary bundle |
Supporting bundles |
|
Bulk exfiltration |
B6 |
B7, B3 |
|
API abuse |
B2 |
B7 |
|
Member credential theft |
B9 |
B2 |
|
Submission tampering |
B2 |
B4 |
|
Insider misuse |
B7 |
B6, B10 |
|
Identity fraud |
B2 |
B7 |
|
Ransomware |
B7 |
B8, B10 |
|
Cloud misconfiguration |
B3 |
B7 |
|
Test and analytics leakage |
B6 |
B3 |
|
Vendor compromise |
B9 |
B3 |
|
Consumer account takeover |
B2 |
B7 |
|
Fraudulent disputes |
B2 |
B4 |
|
Model tampering |
B11 |
B5 |
|
Phishing and impersonation |
B7 |
B10 |
|
Weak detection |
B7 |
B8 |
|
Insecure file transfer |
B3 |
B1 |
|
Excessive retention |
B6 |
B5 |
|
Recovery failure |
B10 |
B1 |
“Primary” and “supporting” indicate suggested combinations, not guaranteed mitigation or complete coverage.
9. Delivery methodology and deliverables
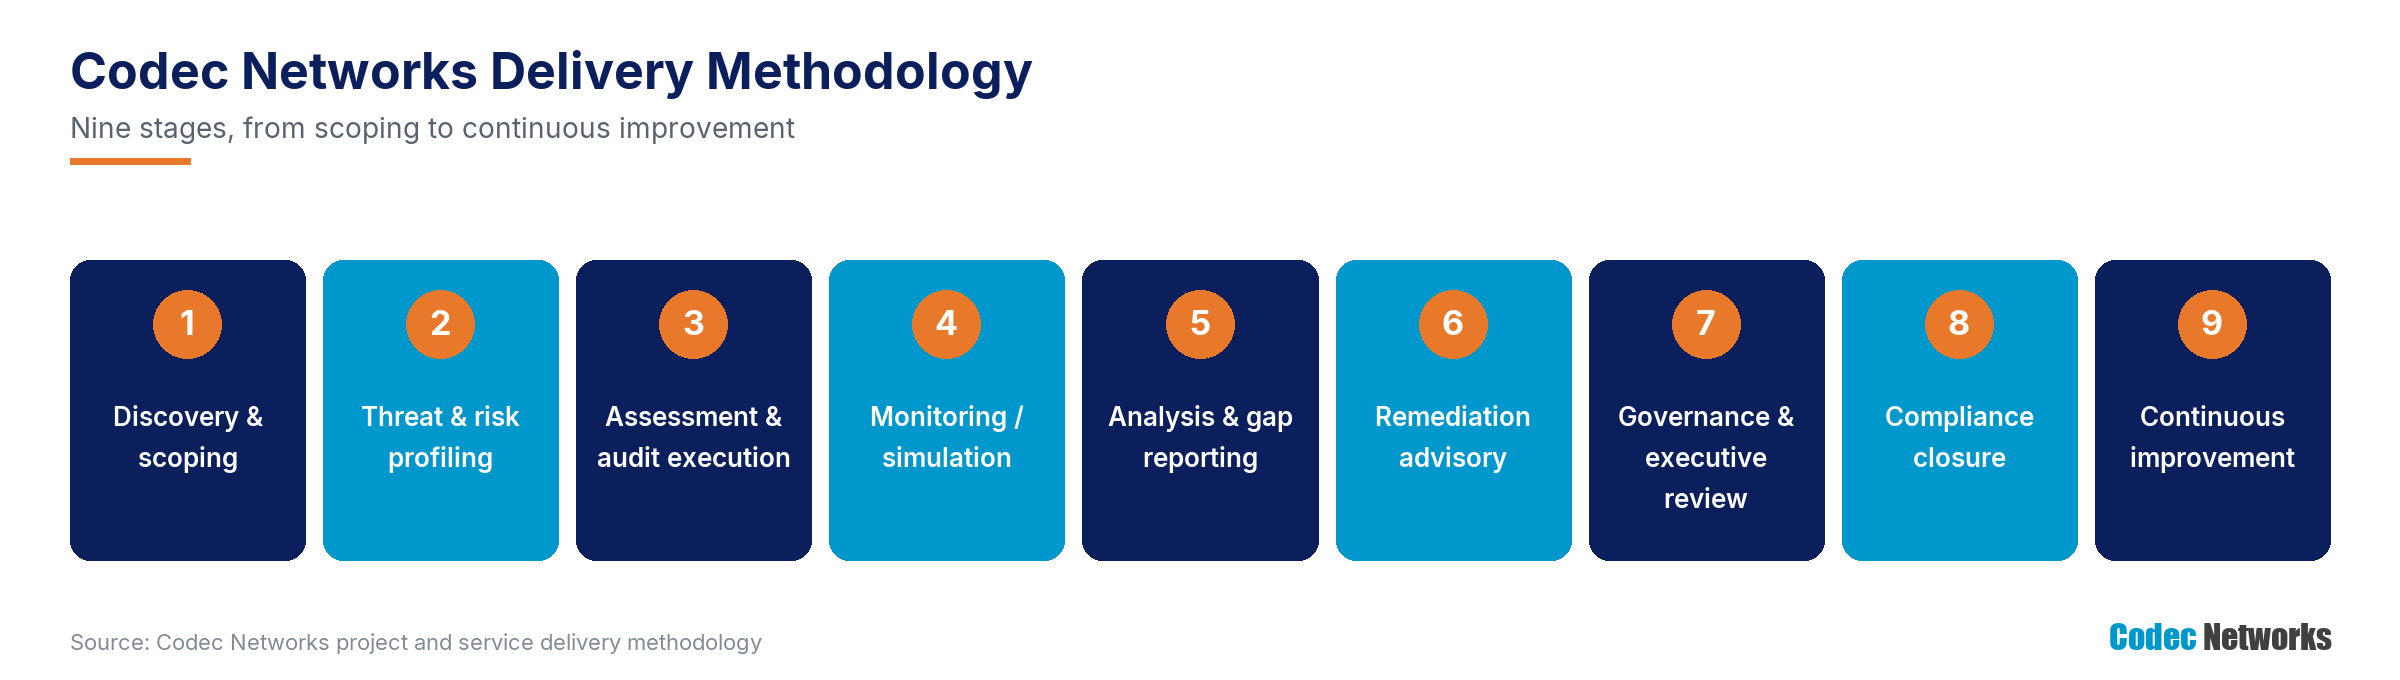
Figure 7: The Codec Networks delivery methodology.
Typical deliverables include an IS audit report and gap matrix, a data access control review, API and integrity test reports with retests, a leakage assessment, a privacy and data-inventory assessment, a cloud review, a member and vendor risk register and Board-ready reporting.
10. Why Codec Networks
- CERT-In empanelled for information security auditing services, and empanelled with NICSI for application audit and compliance services (start-up category).
- Certified to ISO 9001:2015, ISO/IEC 27001:2022 and ISO/IEC 20000-1:2018.
- Full stack: VAPT, regulatory audit, managed SOC, forensics, privacy and Board advisory from one partner, so findings, monitoring and closure stay connected.
- Credit data depth: member access, report APIs, submission integrity, analytics leakage and dispute workflows tested end to end.
- Recognised frameworks and tools: OWASP ASVS/MASVS and API Top 10, MITRE ATT&CK, NIST CSF, ISO 27001 and PCI DSS; tools such as Burp Suite, Nessus, Metasploit, Prowler and leading SIEM/EDR platforms.
- Certified people: CEH, OSCP, CPENT, CISA, ISO 27001 LA/LI, CHFI, CTIA and ECIH professionals.
Annex: Indicative commercial ranges
For internal sales reference only—remove this annex before sharing externally. Ranges are taken from the Codec Networks Bundled Service Models and are subject to scoping, asset counts, frequency and service levels.
|
Bundle |
Package examples and indicative ranges |
|
B1 VAPT Assurance |
Essential ₹1.5–5 lakh; Professional ₹5–15 lakh; Enterprise ₹15–40 lakh; Annual retainer ₹25 lakh–₹1.5 crore |
|
B2 AppSec & DevSecOps |
API Quick Check ₹2–6 lakh; AppSec Professional ₹8–20 lakh; DevSecOps Maturity ₹12–35 lakh; Secure SDLC retainer ₹3–15 lakh/month |
|
B3 Cloud & Zero Trust |
Cloud Essential ₹3–8 lakh; Professional ₹8–25 lakh; Enterprise ₹25–75 lakh; Continuous assurance ₹2–10 lakh/month |
|
B4 Regulatory Audit |
Gap review ₹5–15 lakh; Full regulatory audit ₹15–50 lakh; Multi-framework audit ₹30 lakh–₹1.25 crore; Annual retainer ₹3–20 lakh/month |
|
B5 GRC, ISO, SOC 2 |
ISO readiness ₹5–15 lakh; ISO implementation ₹15–45 lakh; SOC 2 readiness ₹15–60 lakh; GRC retainer ₹2–12 lakh/month |
|
B6 Privacy & DPDPA |
Quick assessment ₹3–10 lakh; Implementation ₹10–40 lakh; DPO-as-a-Service ₹2–8 lakh/month; Privacy retainer ₹3–15 lakh/month |
|
B7 Managed SOC |
Starter ₹2–5 lakh/month; Professional ₹5–15 lakh/month; Enterprise ₹15–50 lakh/month; co-managed per FTE/shift |
|
B8 Forensics & IR |
Triage ₹3–15 lakh; Full investigation ₹15–75 lakh; Ransomware response ₹25 lakh–₹1.5 crore; IR retainer ₹5–50 lakh/year |
|
B9 TPRM |
₹25,000–₹2 lakh per vendor; batch pricing for 50–500 vendors; retainer ₹3–25 lakh/month |
|
B10 Simulation & Tabletop |
Awareness ₹1–5 lakh; Phishing simulation ₹2–10 lakh; Tabletop ₹5–20 lakh; Cyber war-game ₹15–75 lakh; Annual retainer ₹10 lakh–₹1 crore/year |
|
B11 Emerging Tech |
AI/LLM risk review ₹5–25 lakh; Smart contract audit ₹5–50 lakh; Emerging tech retainer ₹5–25 lakh/month |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: Service scope, deliverables, monitoring coverage and service levels are confirmed during engagement scoping. Services support risk reduction and assurance but do not guarantee prevention of all cyber incidents or regulatory compliance. Regulatory references are summaries; confirm against the official instruments applicable to each entity.