

Resources Categories
INDUSTRY FACT FILE · BLOCKCHAIN, WEB3 & VIRTUAL DIGITAL ASSETS
Applicable Cybersecurity Services and Codec Networks Bundles for Web3 and VDAs
How Codec Networks services and bundled service models help VDA exchanges, custodians, Web3 and DeFi projects and blockchain platforms resolve their threats and meet FIU-IND, CERT-In, tax record and DPDP expectations.
|
In this document 1. Our approach 2. Mapping threats to services 3. Codec Networks service catalogue for the sector 4. Codec Networks bundles for the sector 5. Sector programmes built from the bundles 6. Packages: Foundation, Assurance and Continuous Resilience 7. Regulatory requirement-to-bundle mapping 8. Threat-to-bundle coverage matrix 9. Delivery methodology and deliverables 10. Why Codec Networks 11. Annex: indicative commercial ranges |
1. Our approach
Digital asset businesses need security that protects funds that cannot be recalled and that stands up to auditors, partners and regulators. Codec Networks works on four principles:
- Follow the keys: every engagement starts from where value can move: keys, MPC shares, signers, hot and operational wallets, admin keys and bridges, and the people and tools that can trigger them.
- Test code before and after it ships: smart contracts, upgrades, apps and APIs are audited before deployment and retested after every significant change, because exploits arrive within minutes of a flaw going live.
- Watch the chain and the platform: on-chain monitoring of every address and contract is combined with platform, identity and infrastructure monitoring in one SOC.
- Prove it: findings mapped to the PMLA and FIU-IND's Guidelines and registration requirements, CERT-In's Directions and audit guidelines, Income-tax record duties and the DPDP Act.
2. Mapping threats to services
The table maps the 18 threats identified in Document 4 of this set to the Codec Networks services that help mitigate them.
|
Threat / challenge |
Applicable Codec Networks services |
Intended outcome |
|
Hot wallet and signing key compromise |
Custody architecture review, key and secrets review, red team of withdrawal paths |
Keys that stay out of reach |
|
Multisig and signing interface manipulation |
Signing policy review, independent decoding controls, tooling assurance |
Signers who see the truth |
|
Smart contract logic and upgrade flaws |
Smart contract audit, fuzzing, upgrade and timelock review |
Code that holds |
|
Cross-chain bridge and validator compromise |
Bridge and validator review, node hardening, monitoring |
Bridges that need more than a few keys |
|
Oracle and price manipulation in DeFi |
Oracle and economic risk review, scenario testing |
Prices that cannot be bent |
|
Account takeover and credential stuffing |
Login, recovery and session testing, risk signals, SOC alerts |
Accounts that stay with their owners |
|
API key theft and trading bot abuse |
API security testing, key scoping and rate-limit review |
APIs that resist abuse |
|
Phishing, wallet drainers and malicious approvals |
Wallet UX and approval review, awareness, brand monitoring |
Users who are hard to trick |
|
Fake apps, lookalike domains and impersonation |
Brand and domain monitoring, takedown support |
Fewer fakes, removed faster |
|
Insider misuse and privileged access abuse |
PAM review, dual control, activity monitoring, investigations |
Access used only for its purpose |
|
Third-party wallet, custody and SDK supply chain |
Vendor and tooling assessments, integrity checks |
Suppliers held to account |
|
Node, RPC and cloud infrastructure compromise |
Infrastructure and cloud VAPT, node hardening review |
Infrastructure that tells the truth |
|
Developer and DevOps environment compromise |
Secure SDLC and pipeline review, secrets scanning, simulations |
Clean code and clean pipelines |
|
Mule accounts, synthetic identities and KYC fraud |
KYC flow testing, liveness and device checks, fraud monitoring |
Fewer mule accounts |
|
Travel rule, unhosted wallet and mixer exposure |
AML control review, on-chain screening and monitoring review |
Transfers with the right data |
|
DDoS and outages during market volatility |
Resilience and DDoS readiness review, failover testing |
Platforms that stay up |
|
Customer KYC and personal data exposure |
Data discovery, DPDP programme, cloud storage review |
KYC data kept safe and minimal |
|
Weak logs, audit trails and 6-hour reporting |
Log architecture review, managed SOC, IR retainer |
Provable trails, on-time reporting |
3. Codec Networks service catalogue for the sector
|
Service line |
Sector-relevant services |
|
Security Vulnerability Assessment & Penetration Testing |
Exchange and broker platforms, withdrawal paths, nodes, RPCs, validators, external attack surface, red teaming of custody and withdrawal processes |
|
Smart contract & Web3 security |
Smart contract audits for Ethereum, Solana and Polygon, fuzzing and invariant testing, DeFi oracle and economic risk, upgrade and admin-key reviews, using tools such as Slither, Mythril and Tenderly |
|
Application, API & mobile security |
Exchange web and mobile apps, trading APIs, wallet apps and browser extensions, KYC and travel rule applications, secure SDLC |
|
Infrastructure, cloud & zero trust |
Custody architecture, MPC, multisig and HSM reviews, key ceremonies, secrets management, cloud and container security, privileged access |
|
Information security audit & compliance |
CERT-In empanelled cyber security audits supporting FIU-IND registration, CERT-In risk-based audits, AML control and record reviews |
|
Supply chain & third-party risk |
Custody software, wallet tooling, KYC, analytics and travel rule vendors, node and RPC providers, liquidity partners |
|
GRC & ISO/IEC 27001 |
ISMS implementation, policies and evidence for audits, SOC 2 readiness for custodians and platform providers |
|
Data privacy & protection |
KYC data discovery and minimisation, DPDP programmes, retention aligned with five-year record duties, breach workflows |
|
24/7 Managed SOC & threat monitoring |
On-chain monitoring of treasury addresses and contracts, account takeover and API abuse alerts, admin and developer activity, cloud and node alerts |
|
Cyber forensics & incident response |
Hack response, blockchain and crypto forensics, Chainalysis-supported fund tracing, evidence for law enforcement and CERT-In reporting support |
4. Codec Networks bundles for the sector
Eleven of the twelve bundles in the Codec Networks Bundled Service Models apply directly to VDA exchanges, custodians, Web3 and DeFi projects and tokenisation platforms; the Global Cyber Back-Office SPV Program (Bundle 12) is offered separately for international clients.
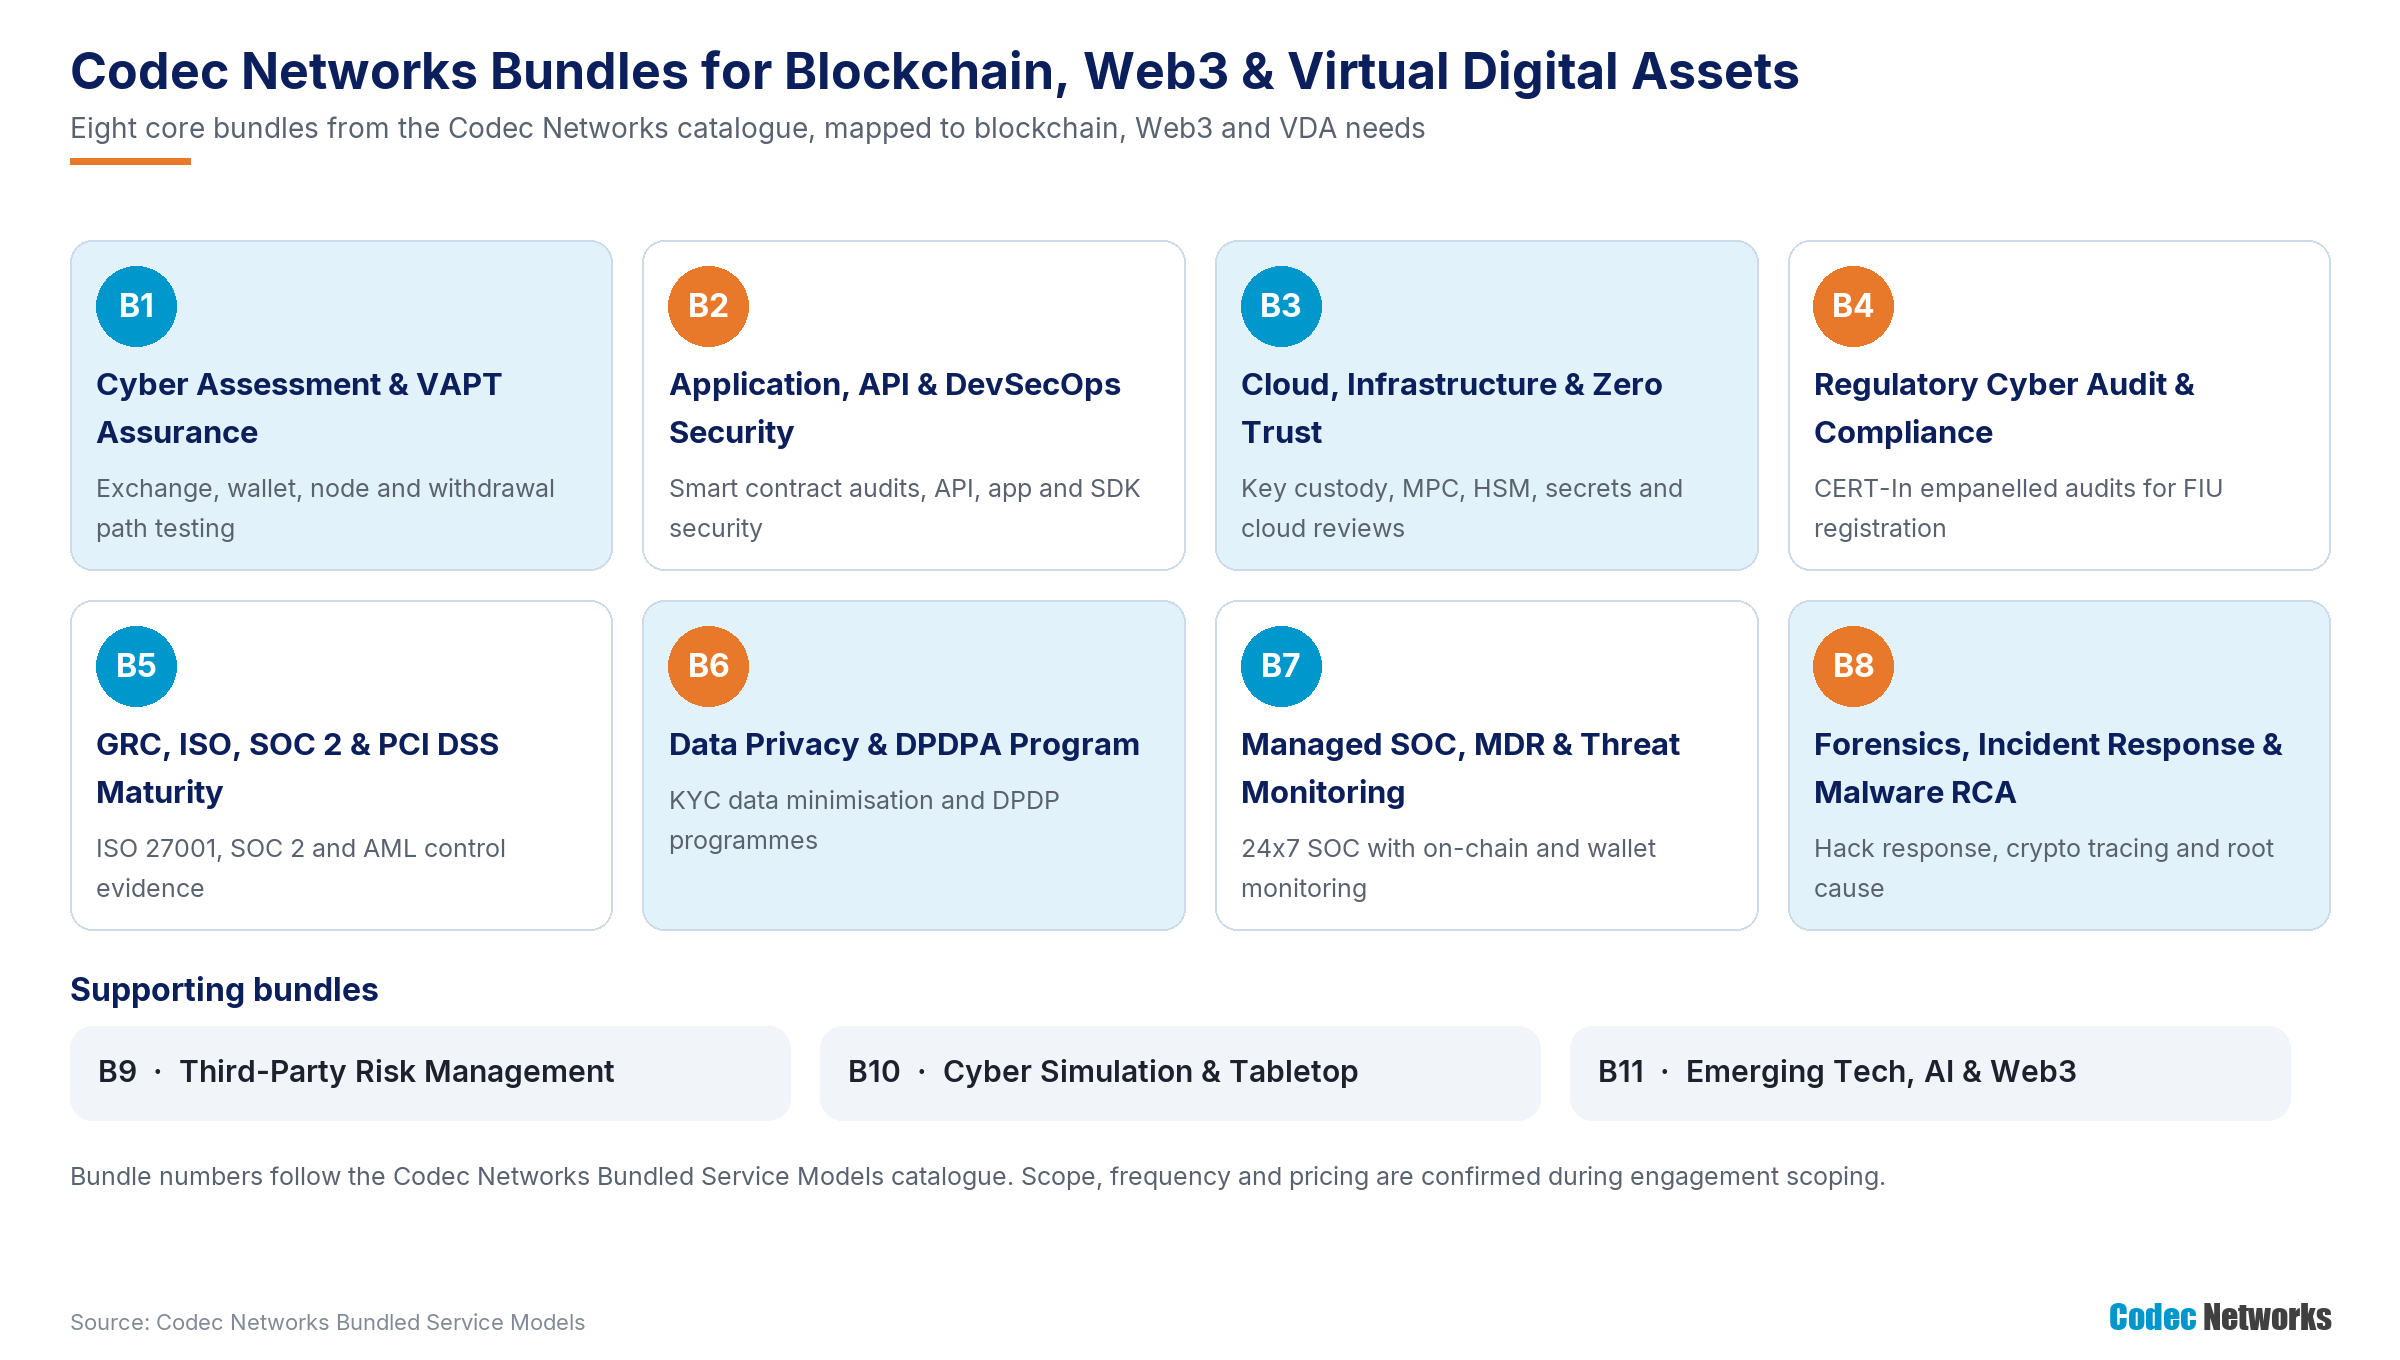
Figure 6: Codec Networks bundles applied to the sector.
|
Bundle |
Name |
Sector-relevant scope |
Best suited for |
Key deliverables |
|
B1 |
Cyber Assessment & VAPT Assurance Program |
Exchange and broker platforms, withdrawal paths, nodes, validators and red teaming |
Exchanges, brokers, custodians and bridges |
Assessment reports, retests and closure tracker |
|
B2 |
Application, API & DevSecOps Security Program |
Smart contracts, trading APIs, exchange and wallet apps, KYC and travel rule apps |
Web3 and DeFi teams, exchanges, wallet providers |
Audit and test reports, fix verification |
|
B3 |
Cloud, Infrastructure & Zero Trust Security Program |
Custody architecture, MPC, multisig, HSMs, secrets, cloud and privileged access |
Exchanges, custodians and enterprise ledgers |
Architecture review and remediation roadmap |
|
B4 |
Regulatory Cybersecurity Audit & Compliance Assurance Program |
CERT-In empanelled audits for FIU-IND registration, AML control and record reviews |
Every registered or registering VDA service provider |
Audit report, gap matrix, evidence tracker |
|
B5 |
GRC, ISO, SOC 2 & Cyber Maturity Program |
ISO/IEC 27001 ISMS, SOC 2 readiness, policies and audit evidence |
Custodians, platforms and B2B providers |
Maturity scorecard, policies, ISMS documents |
|
B6 |
Data Privacy, DPDPA & Data Protection Program |
KYC data minimisation, retention, data discovery and DPDP |
Exchanges, brokers and wallet providers ahead of May 2027 |
Privacy gap assessment, data map, roadmap |
|
B7 |
Managed SOC, MDR & Continuous Threat Monitoring Program |
24x7 SOC with on-chain, wallet, contract and platform monitoring |
Exchanges, custodians, DeFi protocols |
SOC reports, MTTD/MTTR, incident records |
|
B8 |
Digital Forensics, Incident Response & Malware RCA Program |
Hack response, blockchain forensics, fund tracing and RCA |
Any organisation facing a theft or breach |
Forensic report, tracing report, reporting support |
|
B9 |
Third-Party Risk Management & Supply Chain Cyber Risk Program |
Custody software, wallet tooling, KYC, analytics and node provider assurance |
Exchanges, custodians and consortia |
Vendor risk register and assessment reports |
|
B10 |
Cyber Simulation, Awareness, Tabletop & Crisis Readiness Program |
Theft scenario exercises, signer and developer social engineering simulations |
Leadership, treasury, engineering and community teams |
Exercise reports and playbooks |
|
B11 |
Emerging Technology, AI, Web3 & Future Security Program |
Smart contract audits, DeFi risk, tokenisation and AI risk reviews |
Web3, DeFi, NFT and tokenisation projects |
Audit report with severity ratings and retest |
5. Sector programmes built from the bundles
Codec Networks packages the catalogue bundles into six blockchain, Web3 and VDA programmes.
|
Programme |
Built from bundles |
Challenges addressed |
|
FIU-IND Registration Assurance |
B4, B5, B1 |
CERT-In empanelled audit, evidence, closure |
|
Custody & Signing Assurance |
B3, B1, B9 |
Keys, MPC, multisig, signer tooling, withdrawal paths |
|
Smart Contract & Protocol Security |
B11, B2, B7 |
Audits, fuzzing, upgrades, live contract monitoring |
|
Exchange Platform Security |
B1, B2, B3 |
Apps, APIs, nodes, cloud, account takeover |
|
AML Technology & Data Protection |
B4, B6, B2 |
KYC, travel rule, records, DPDP |
|
Crypto SOC & Hack Response |
B7, B8, B10 |
On-chain monitoring, tracing, six-hour reporting |
6. Packages: Foundation, Assurance and Continuous Resilience
|
Package element |
Foundation |
Assurance |
Continuous Resilience |
|
Typical organisation |
Web3 start-ups, DeFi and NFT projects |
Exchanges, brokers and wallet apps |
Large exchanges, custodians, DLT platforms |
|
Testing |
B11 + B2: smart contract audit, web and wallet app test |
B1 + B2: exchange, API and mobile testing |
B1 + B2 + B10: red team of withdrawal paths and signers |
|
Audit and GRC |
B5: security policy and launch checklist |
B4 + B5: CERT-In empanelled audit for FIU-IND, ISO 27001 |
B4 + B5 + B9: audits, SOC 2 and vendor assurance |
|
Architecture and privacy |
B3: admin key and upgrade review |
B3 + B6: wallet and custody review, DPDP programme |
B3 + B6 + B11: MPC, HSM and key ceremony review, DPDP, tokenisation risk |
|
Monitoring and response |
Launch-day monitoring (B7) and IR retainer (B8) |
B7: managed SOC + B8 |
B7: SOC with on-chain watch + B8 retainer |
|
Reporting |
Audit report for users and investors |
CISO, Principal Officer and partner reporting |
Board, FIU-IND, partner and client-ready reporting |
7. Regulatory requirement-to-bundle mapping
|
Requirement (source) |
How Codec Networks helps |
Bundle |
|
Registration with FIU-IND as a reporting entity for VDA activities (PMLA notification of 7 March 2023) |
Registration readiness and control evidence review |
B4, B5 |
|
Cyber security audit certificate from a CERT-In empanelled auditor (FIU-IND circular of 15 September 2025, as reported) |
CERT-In empanelled cyber security audit with gap closure |
B4, B1 |
|
CDD with liveness, geo-location and penny drop; tamper-proof audit trails (FIU-IND Guidelines 2026) |
KYC flow testing, log integrity and record review |
B2, B4 |
|
Real-time travel rule; unhosted wallet monitoring; no facilitation of mixers (FIU-IND Guidelines 2026) |
AML technology and on-chain screening review |
B4, B7, B11 |
|
KYC information and transaction records kept for five years (CERT-In Directions, 2022) |
Record retention and log architecture review |
B3, B7 |
|
Cyber incidents to CERT-In within six hours; 180-day logs in India (CERT-In Directions, 2022) |
Managed SOC, log architecture, IR retainer and reporting support |
B7, B8 |
|
Risk-based independent audits with auditor independence (CERT-In audit guidelines, 2025) |
Independent audit scoping and evidence management |
B4 |
|
Reasonable security safeguards and breach intimation (DPDP Act 2023 and Rules 2025) |
DPDP gap assessment, data maps, breach workflow |
B6, B8 |
|
Auditor eligibility and independence FIU-IND's September 2025 circular, as reported, calls for VDA service providers to obtain a cyber security audit certificate from a CERT-In empanelled auditor for registration and continued registration. Codec Networks is CERT-In empanelled for information security auditing services and empanelled with NICSI for application audit and compliance services (start-up category); it confirms eligibility and independence against FIU-IND's, CERT-In's and the client's requirements in each proposal, and does not audit systems it has designed or operates. |
8. Threat-to-bundle coverage matrix
|
Threat / challenge |
Primary bundle |
Supporting bundles |
|
Hot wallet and signing key compromise |
B3 |
B1, B7, B8 |
|
Multisig and signing interface manipulation |
B3 |
B9, B10 |
|
Smart contract logic and upgrade flaws |
B11 |
B2, B7 |
|
Cross-chain bridge and validator compromise |
B11 |
B1, B3, B7 |
|
Oracle and price manipulation in DeFi |
B11 |
B2 |
|
Account takeover and credential stuffing |
B2 |
B7 |
|
API key theft and trading bot abuse |
B2 |
B1, B7 |
|
Phishing, wallet drainers and malicious approvals |
B10 |
B2, B7 |
|
Fake apps, lookalike domains and impersonation |
B7 |
B10 |
|
Insider misuse and privileged access abuse |
B3 |
B7, B8 |
|
Third-party wallet, custody and SDK supply chain |
B9 |
B2, B3 |
|
Node, RPC and cloud infrastructure compromise |
B1 |
B3, B7 |
|
Developer and DevOps environment compromise |
B2 |
B3, B10 |
|
Mule accounts, synthetic identities and KYC fraud |
B2 |
B4, B7 |
|
Travel rule, unhosted wallet and mixer exposure |
B4 |
B7, B11 |
|
DDoS and outages during market volatility |
B3 |
B1, B7 |
|
Customer KYC and personal data exposure |
B6 |
B3, B8 |
|
Weak logs, audit trails and 6-hour reporting |
B7 |
B4, B8 |
“Primary” and “supporting” indicate suggested combinations, not guaranteed mitigation or complete coverage.
9. Delivery methodology and deliverables
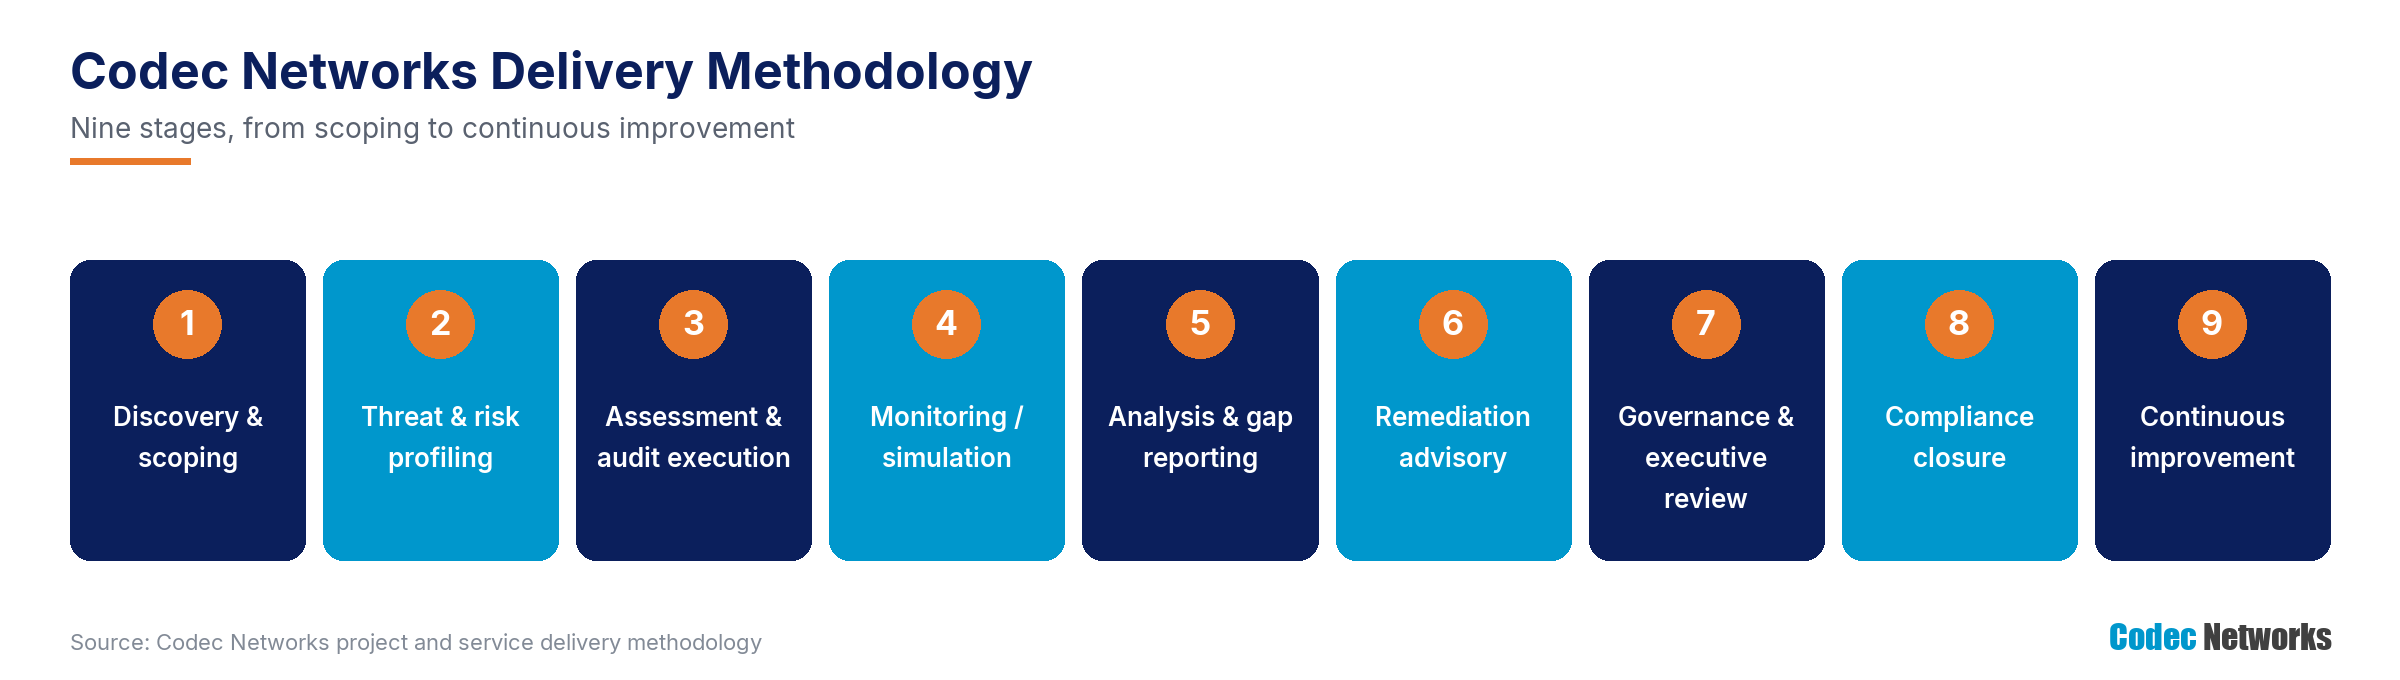
Figure 7: The Codec Networks delivery methodology.
Typical deliverables include CERT-In empanelled cyber security audit reports with gap matrices and closure trackers for FIU-IND registration, smart contract audit reports with severity-rated findings, fuzzing and invariant test results and fix verification, upgrade and admin-key review reports, custody architecture, MPC, multisig, HSM and signing policy review reports, signer interface and tooling assurance findings, exchange web, mobile and API test reports with retests, node, validator, bridge and cloud assessment reports, AML technology, travel rule and record retention review reports, vendor assessment reports for custody software and wallet tooling, ISO 27001 and SOC 2 readiness reports, a DPDP gap assessment, managed SOC reports covering on-chain and platform monitoring, blockchain forensic and fund tracing reports with evidence for law enforcement and CERT-In reporting support, and exercise reports.
10. Why Codec Networks
- CERT-In empanelled for information security auditing services, and empanelled with NICSI for application audit and compliance services (start-up category).
- Certified to ISO 9001:2015, ISO/IEC 27001:2022 and ISO/IEC 20000-1:2018.
- Full stack: VAPT, regulatory audit, managed SOC, forensics, privacy and Board advisory from one partner, so findings, monitoring and closure stay connected.
- Web3 and digital asset depth: smart contract audits for Ethereum, Solana and Polygon, DeFi and oracle risk reviews, custody, MPC and multisig assessments and blockchain forensics with Chainalysis-supported tracing, combined with FIU-IND-aligned CERT-In empanelled audits, CERT-In's Directions and the DPDP Act.
- Recognised frameworks and tools: OWASP ASVS/MASVS and API Top 10, MITRE ATT&CK, NIST CSF, ISO 27001 and PCI DSS; tools such as Burp Suite, Nessus, Metasploit, Prowler and leading SIEM/EDR platforms.
- Certified people: CEH, OSCP, CPENT, CISA, ISO 27001 LA/LI, CHFI, CTIA and ECIH professionals.
Annex: Indicative commercial ranges
For internal sales reference only—remove this annex before sharing externally. Ranges are taken from the Codec Networks Bundled Service Models and are subject to scoping, asset counts, frequency and service levels.
|
Bundle |
Package examples and indicative ranges |
|
B1 VAPT Assurance |
Essential ₹1.5–5 lakh; Professional ₹5–15 lakh; Enterprise ₹15–40 lakh; Annual retainer ₹25 lakh–₹1.5 crore |
|
B2 AppSec & DevSecOps |
API Quick Check ₹2–6 lakh; AppSec Professional ₹8–20 lakh; DevSecOps Maturity ₹12–35 lakh; Secure SDLC retainer ₹3–15 lakh/month |
|
B3 Cloud & Zero Trust |
Cloud Essential ₹3–8 lakh; Professional ₹8–25 lakh; Enterprise ₹25–75 lakh; Continuous assurance ₹2–10 lakh/month |
|
B4 Regulatory Audit |
Gap review ₹5–15 lakh; Full regulatory audit ₹15–50 lakh; Multi-framework audit ₹30 lakh–₹1.25 crore; Annual retainer ₹3–20 lakh/month |
|
B5 GRC, ISO, SOC 2 |
ISO readiness ₹5–15 lakh; ISO implementation ₹15–45 lakh; SOC 2 readiness ₹15–60 lakh; GRC retainer ₹2–12 lakh/month |
|
B6 Privacy & DPDPA |
Quick assessment ₹3–10 lakh; Implementation ₹10–40 lakh; DPO-as-a-Service ₹2–8 lakh/month; Privacy retainer ₹3–15 lakh/month |
|
B7 Managed SOC |
Starter ₹2–5 lakh/month; Professional ₹5–15 lakh/month; Enterprise ₹15–50 lakh/month; co-managed per FTE/shift |
|
B8 Forensics & IR |
Triage ₹3–15 lakh; Full investigation ₹15–75 lakh; Ransomware response ₹25 lakh–₹1.5 crore; IR retainer ₹5–50 lakh/year |
|
B9 TPRM |
₹25,000–₹2 lakh per vendor; batch pricing for 50–500 vendors; retainer ₹3–25 lakh/month |
|
B10 Simulation & Tabletop |
Awareness ₹1–5 lakh; Phishing simulation ₹2–10 lakh; Tabletop ₹5–20 lakh; Cyber war-game ₹15–75 lakh; Annual retainer ₹10 lakh–₹1 crore/year |
|
B11 Emerging Tech |
AI/LLM risk review ₹5–25 lakh; Smart contract audit ₹5–50 lakh; Emerging tech retainer ₹5–25 lakh/month |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: Service scope, deliverables, monitoring coverage and service levels are confirmed during engagement scoping. Services support risk reduction and assurance but do not guarantee prevention of all cyber incidents or regulatory compliance. Regulatory references are summaries; confirm against the official instruments applicable to each entity.