A. Service Scope and Client Fit
A1We already follow ISO/IEC 27001. Why do we need industry-specific advice?
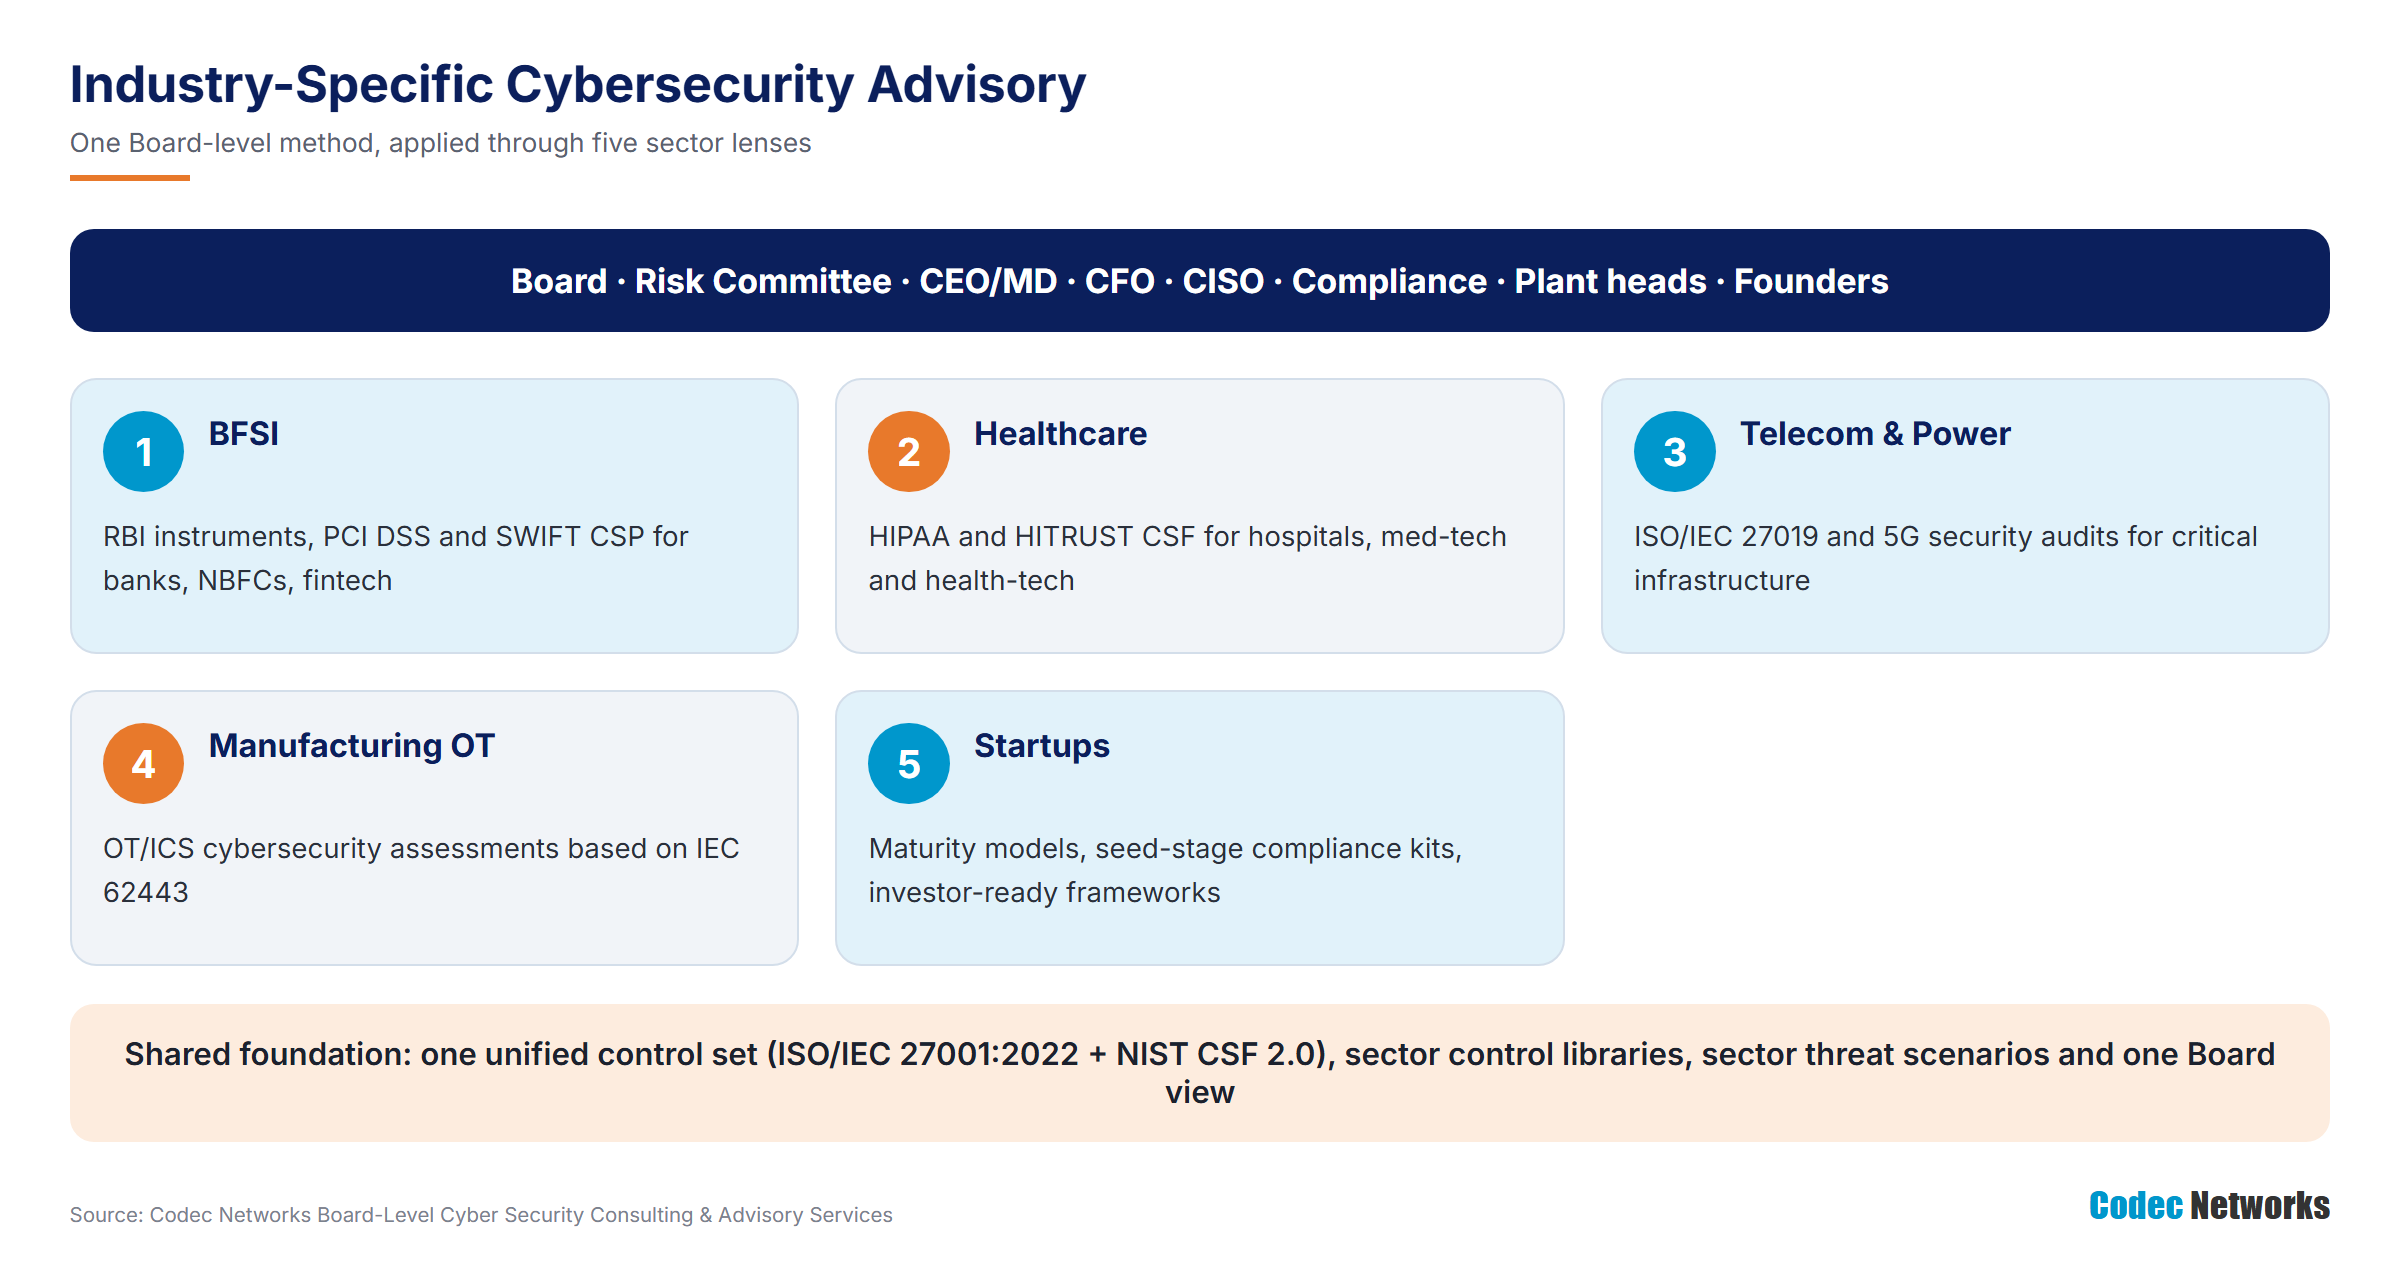
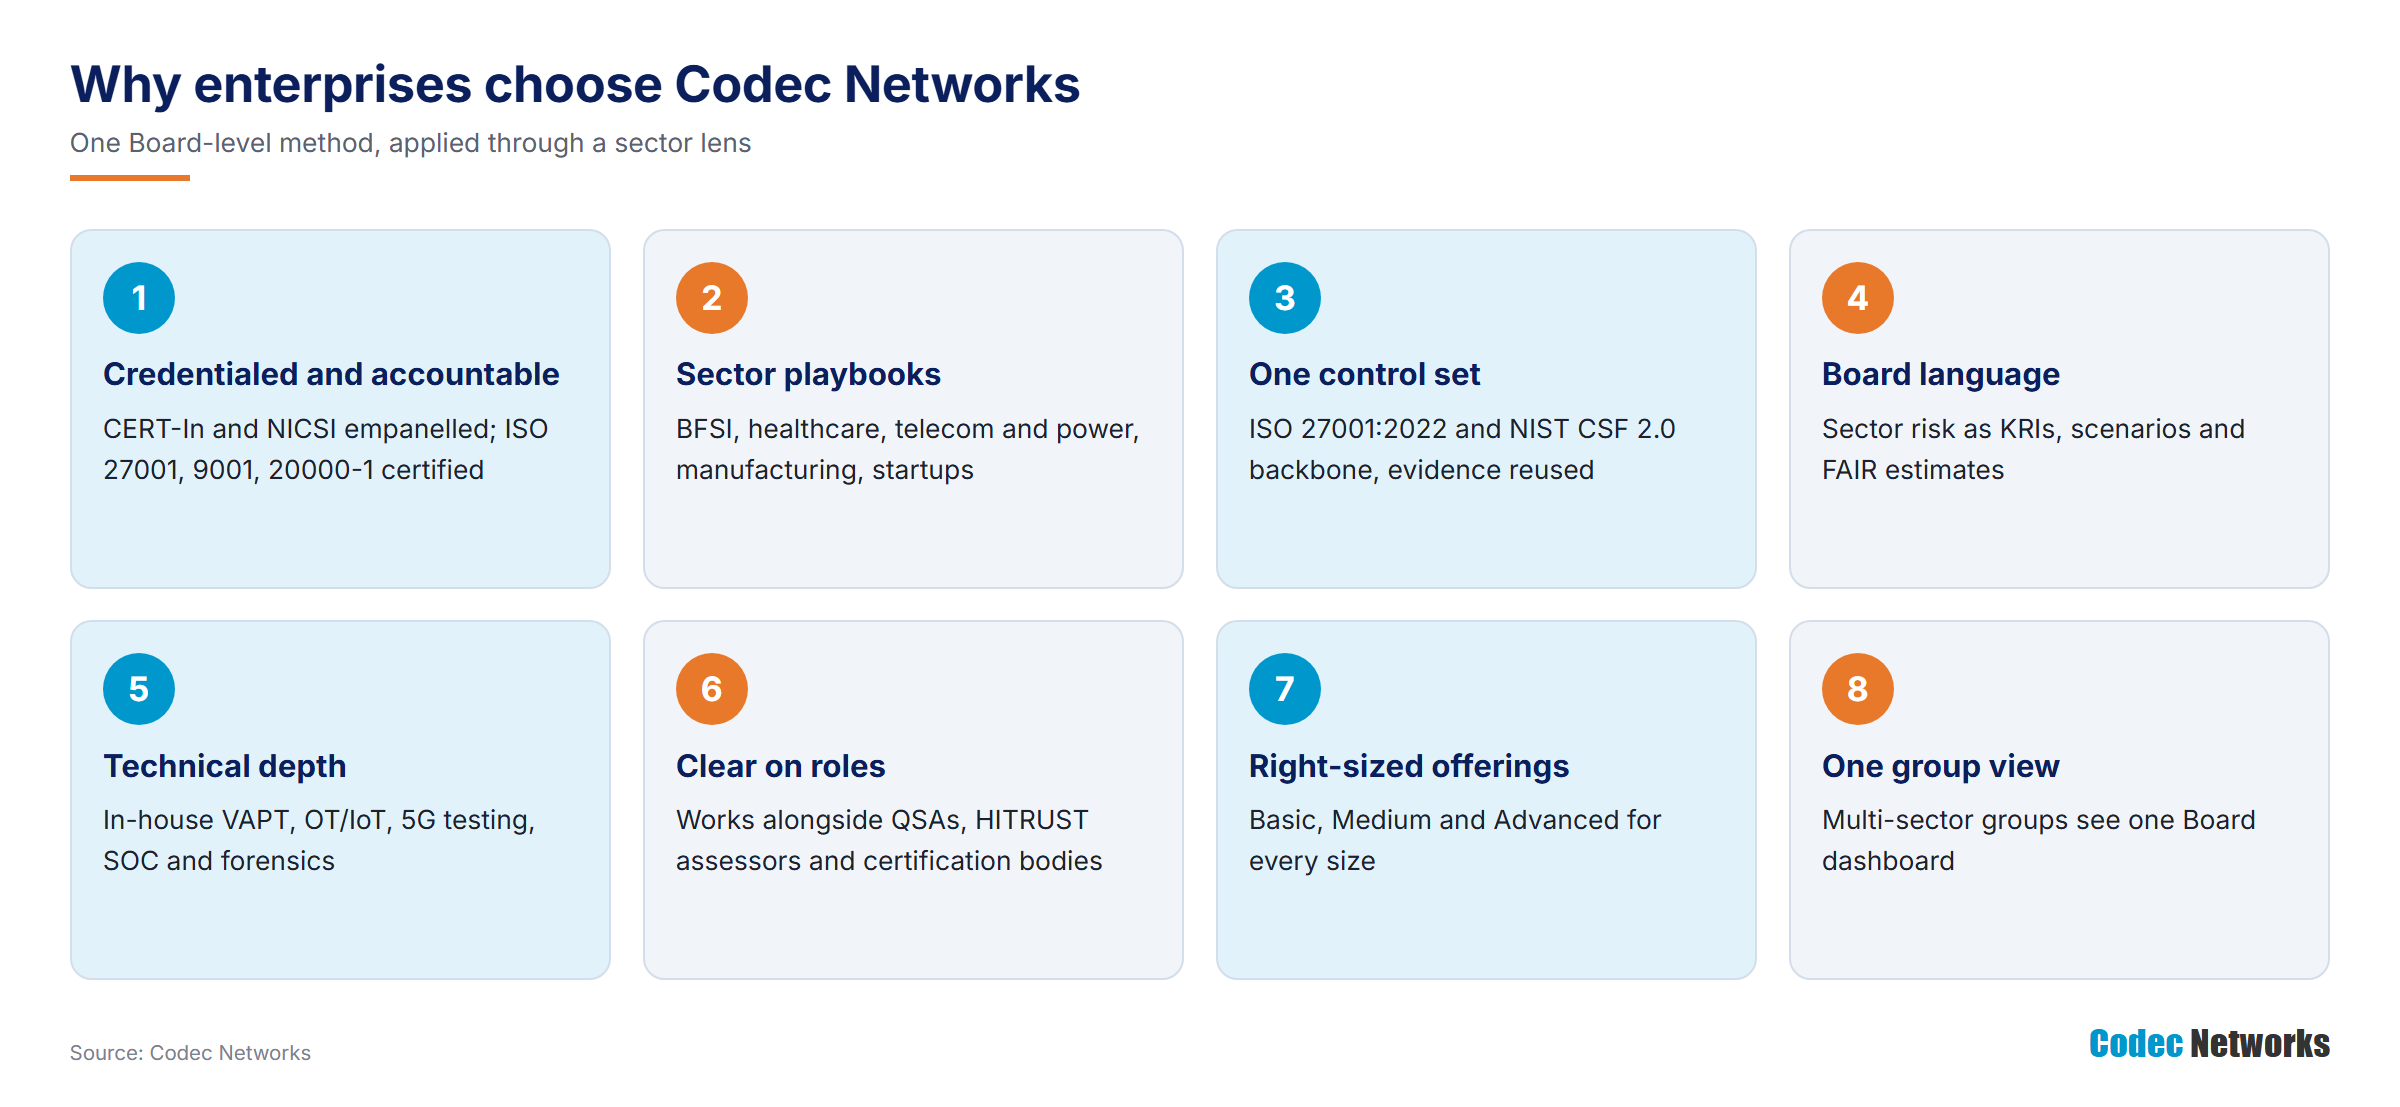
ISO/IEC 27001:2022 gives you a management system and a control set. It does not tell you what your sector's regulators, standards bodies, customers and investors will ask about. Codec Networks maps each sector's requirements onto one unified control set built on ISO/IEC 27001:2022 and NIST CSF 2.0, so you implement a control once and use the evidence many times.
A2Which sectors does Codec Networks cover?
Five: BFSI (banks, NBFCs and fintech), Healthcare (hospitals, med-tech and health-tech), Telecom & Power (critical infrastructure), Manufacturing OT (plants and industrial control systems) and Startups (seed stage to pre-IPO).
A3We are a group with businesses in several sectors. Can you give us one Board view?
Yes. Each business gets its own sector programme, but all of them sit on one control set and report into one Board pack. The Board sees each business in its sector's language and the group's overall position on one page.
Multi-sector group
A4Why does the Board need sector-specific reporting?
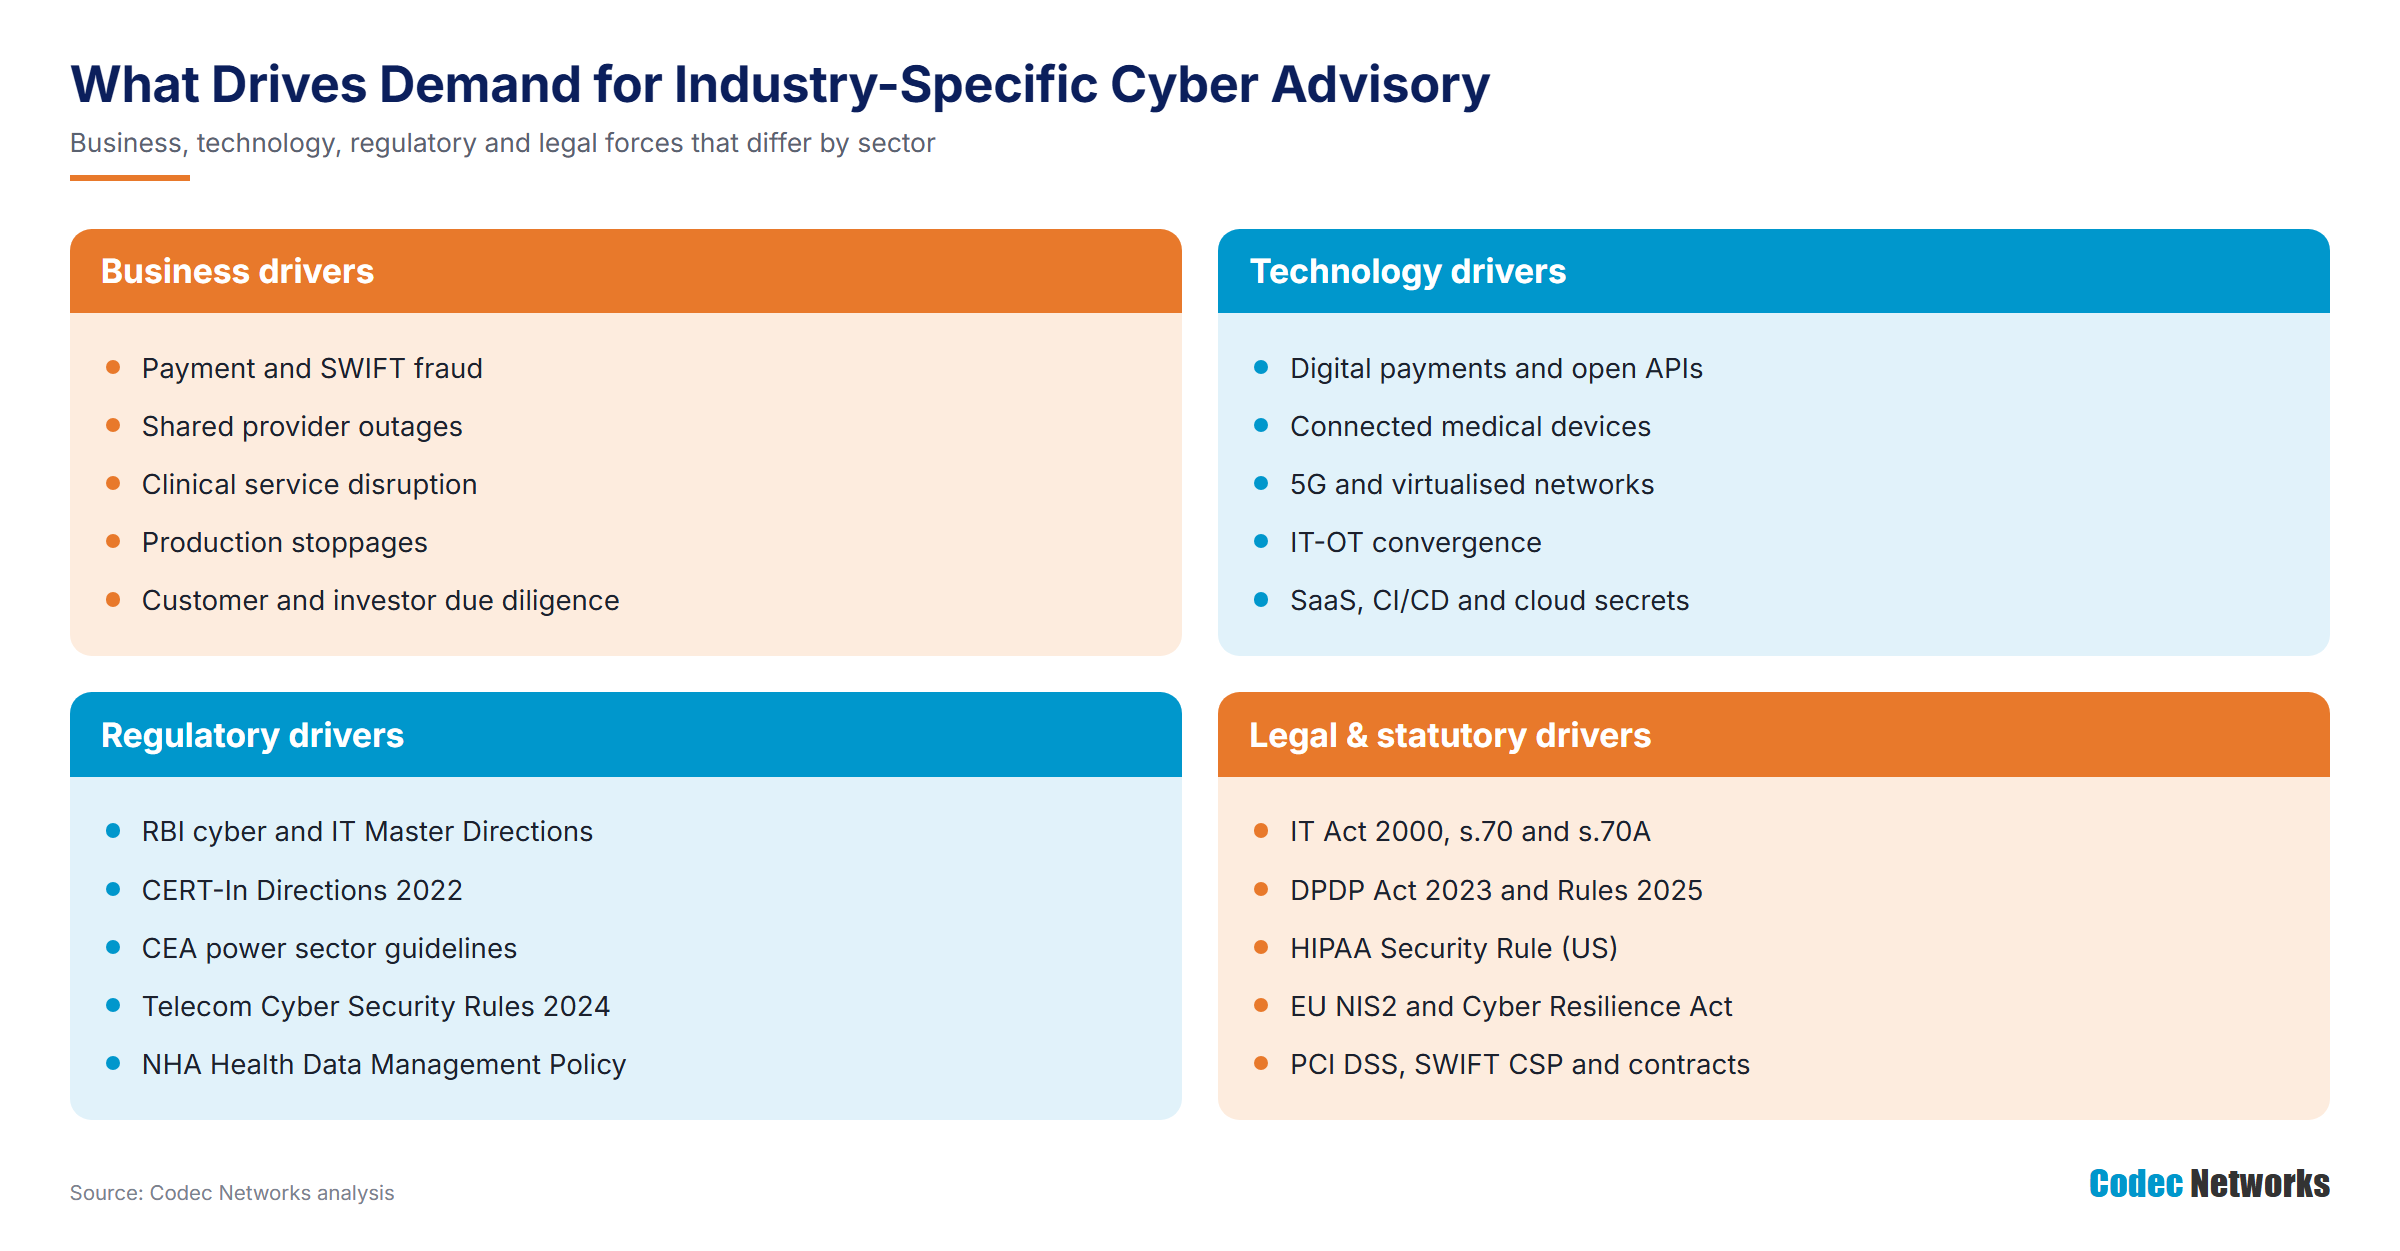
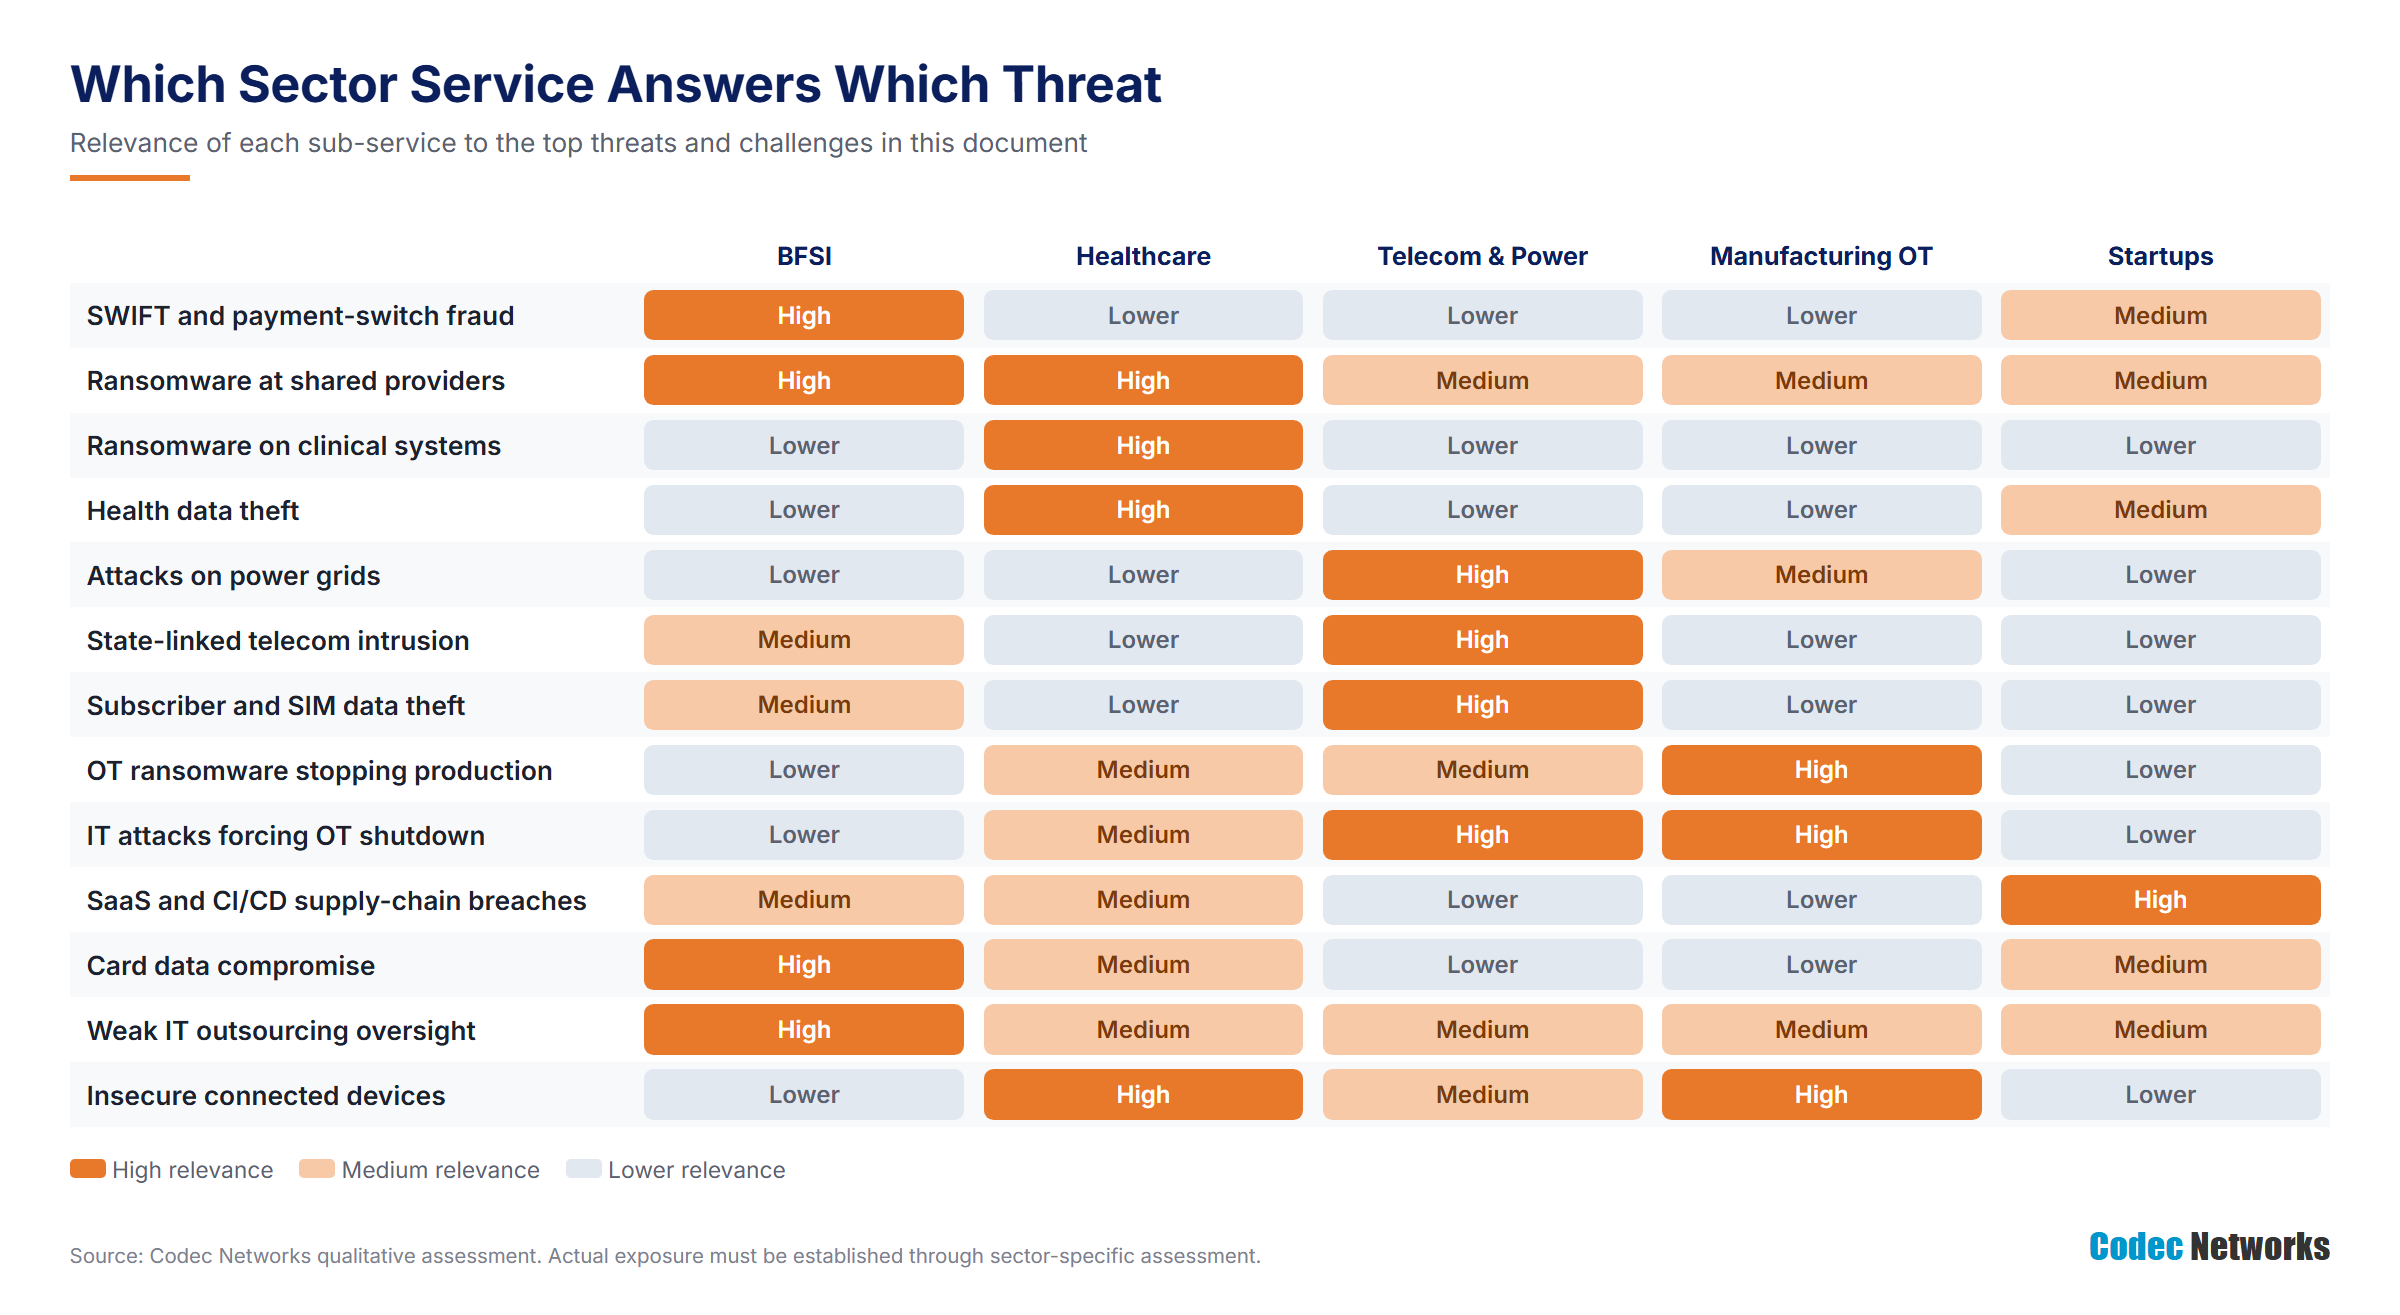
Because directors are asked sector questions: card data, SWIFT attestation, patient safety, grid and network availability, plant downtime or investor due diligence. A generic cyber report does not answer them. Sector reporting shows the risks and obligations that matter in that business.
A5Can you assess plant or substation OT without disrupting operations?
Yes. Codec Networks' ICS/OT specialists use passive and read-only methods first, work in agreed change windows and do not run active tests on live controllers without the plant owner's written approval.
Manufacturing OTTelecom & Power
A6We are a small fintech or startup. Is this too heavy for us?
No. The Startups sub-service is sized for seed to Series B: a maturity baseline, a seed-stage compliance kit of policies and evidence templates, and an investor-ready framework. A small fintech can add a BFSI Basic assessment through the Sector Starter bundle.
StartupsBFSI
A7Is Codec Networks a PCI QSA or a HITRUST assessor?
No. Codec Networks is not a PCI QSA, a HITRUST External Assessor organisation or a certification body. It prepares the client and works alongside the client's QSA, HITRUST External Assessor or certification body. For SWIFT CSP, it prepares the client for independent assessment and attestation.
BFSIHealthcare
A8Who in our organisation will you work with?
The Board and Risk Committee, CEO or MD, CFO, CISO, CIO or CTO, and the Chief Compliance Officer or Company Secretary. Depending on the sector, also plant and operations heads, the hospital CMIO and medical device heads, or founders and investors.
B. Standards, Laws and Regulatory Alignment
B1Which RBI instruments do you map for banks and NBFCs?
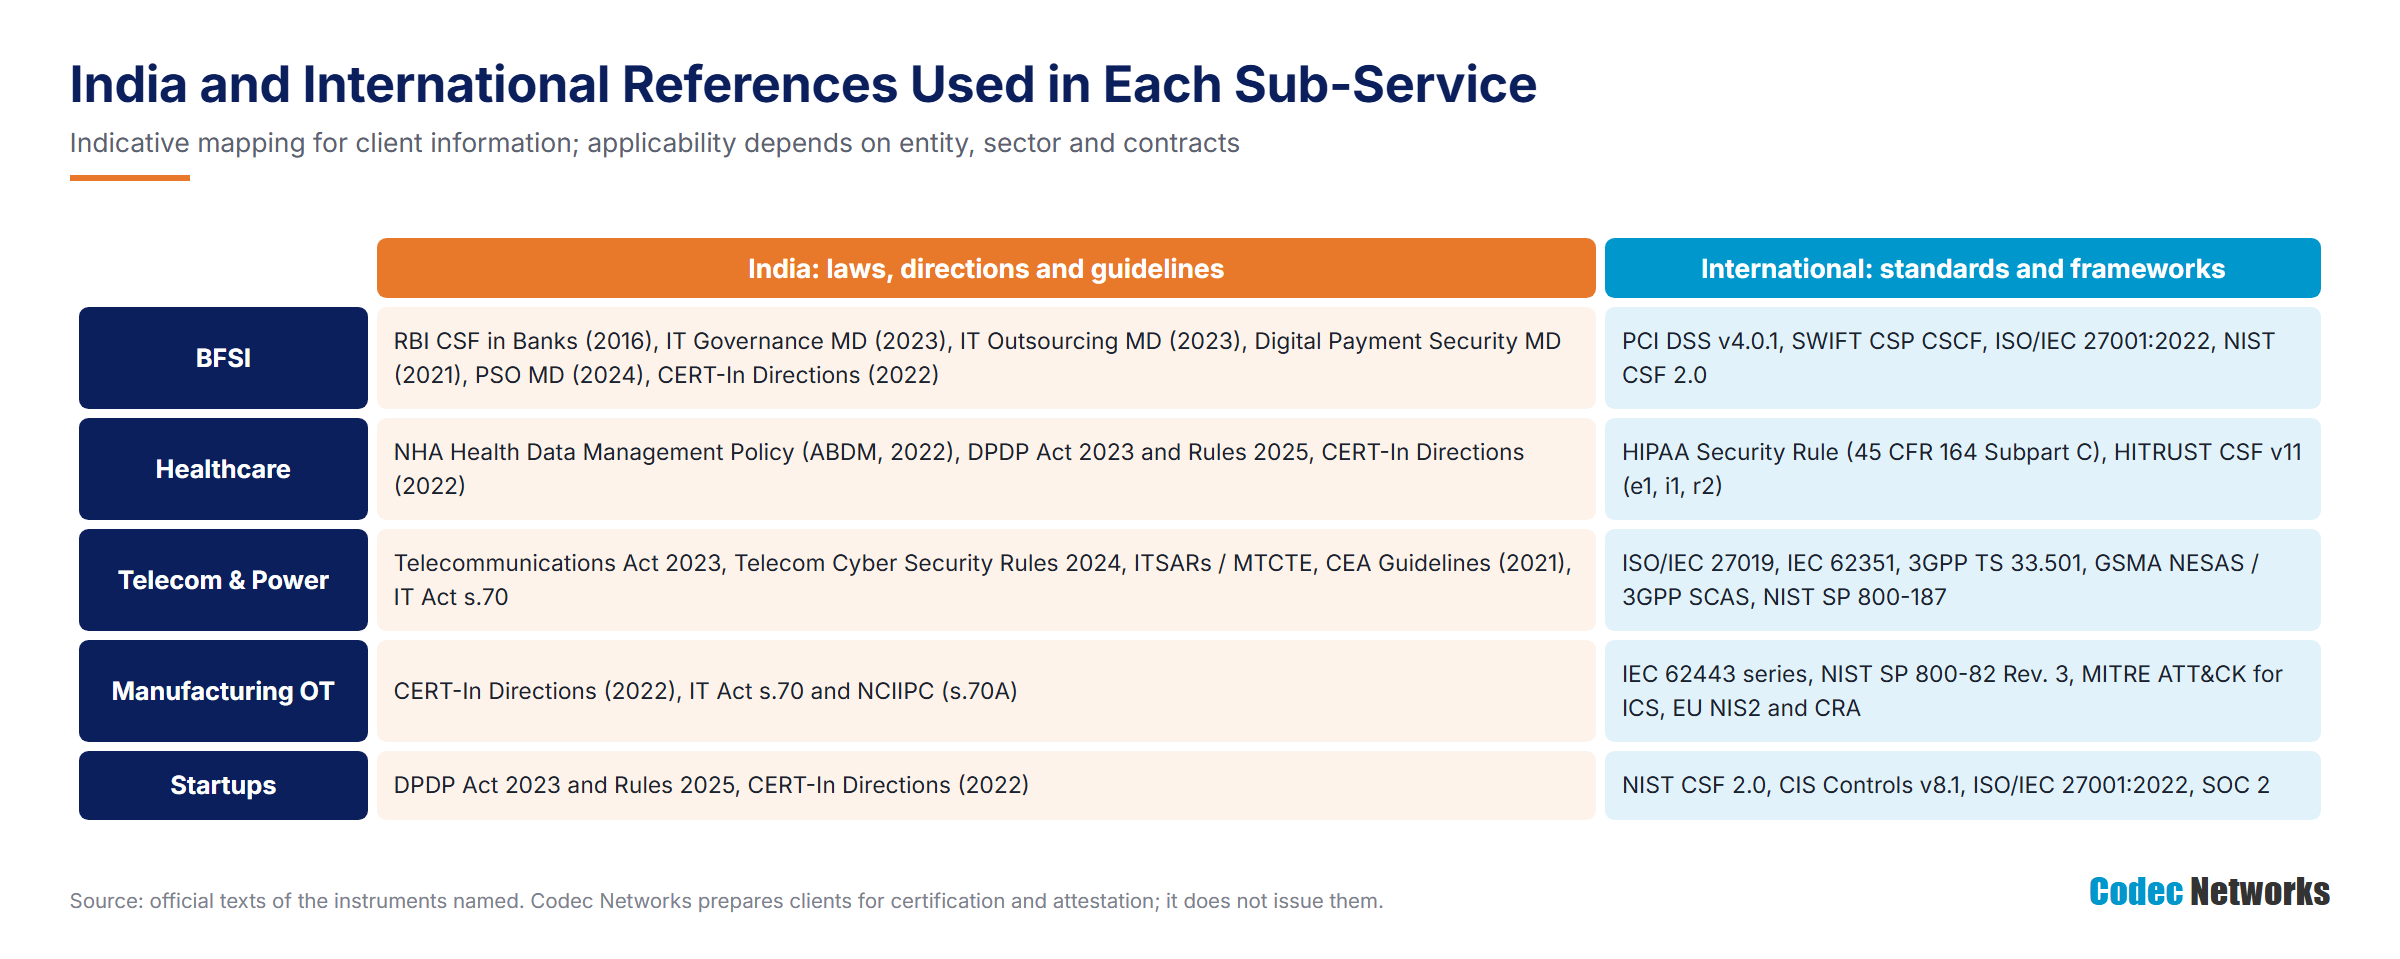
As general information for clients: RBI's Cyber Security Framework in Banks (DBS.CO/CSITE/BC.11/33.01.001/2015-16, 2 June 2016); the Master Direction on IT Governance, Risk, Controls and Assurance Practices (7 November 2023, effective 1 April 2024); the Master Direction on Outsourcing of IT Services (10 April 2023); the Master Direction on Digital Payment Security Controls (18 February 2021); and, for non-bank payment system operators, the Master Direction of 30 July 2024. Which apply depends on the entity; refer to the official text for applicability.
BFSI
B2What changed with PCI DSS v4.0.1?
As general information: PCI SSC published PCI DSS v4.0.1 in June 2024, and the requirements that were future-dated became effective on 31 March 2025. Codec Networks runs readiness against them and works alongside your QSA, who performs the assessment.
BFSI
B3How does SWIFT CSP attestation work?
As general information: SWIFT publishes the Customer Security Controls Framework each year with mandatory and advisory controls. Users attest each year, by 31 December, through the KYC-SA tool, and the attestation must be supported by an independent assessment, internal or external. Codec Networks prepares the client for that assessment and attestation; the attestation remains the client's.
BFSI
B4Is HIPAA relevant to an Indian hospital or health-tech company?
As general information: the HIPAA Security Rule (45 CFR Part 164 Subpart C) sets administrative, physical and technical safeguards under US law, and Indian firms serving US healthcare clients are often asked to meet it by contract. HHS published a proposed rule to strengthen it in January 2025; it is proposed, not final. In India, the National Health Authority's Health Data Management Policy under ABDM (2022) and the DPDP Act 2023 are relevant references. Refer to the official texts for applicability.
Healthcare
B5What is the difference between HITRUST e1, i1 and r2?
Under HITRUST CSF v11, e1 is an essentials assessment valid for one year, i1 an implemented assessment valid for one year and r2 a risk-based assessment valid for two years. Codec Networks helps you choose and prepare; the assessment is performed by a HITRUST External Assessor.
Healthcare
B6Which references apply to telecom and power?
As general information: the Telecommunications Act 2023 and the Telecom Cyber Security Rules 2024 (November 2024), which include six-hour incident reporting for telecom entities; ITSARs issued by NCCS under DoT and tested under the MTCTE regime; and CEA's Guidelines on Cyber Security in Power Sector (October 2021). International references include ISO/IEC 27019, IEC 62351, 3GPP TS 33.501, GSMA NESAS and 3GPP SCAS, with NERC CIP as a reference model.
Telecom & Power
B7Which parts of IEC 62443 do you use?
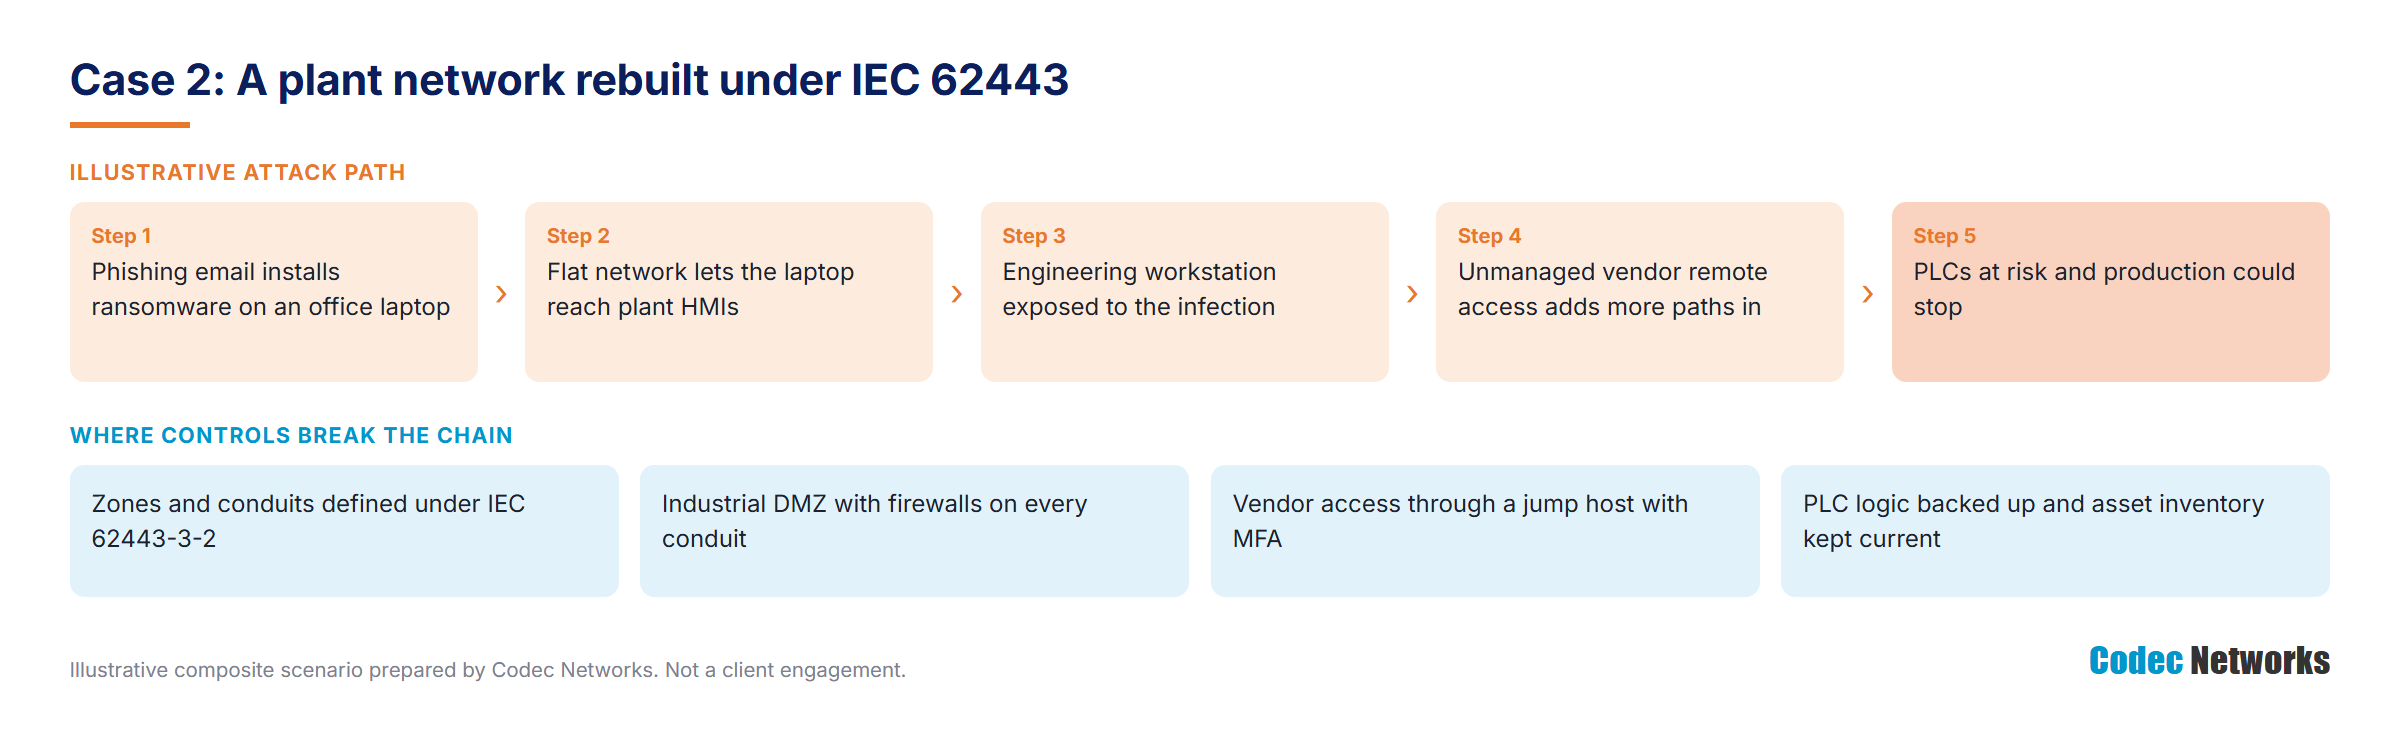
IEC 62443-2-1 for the asset owner's security programme, 62443-3-2 for risk assessment, zones and conduits, 62443-3-3 for system requirements and security levels SL1 to SL4, and 62443-4-1 and 4-2 for product makers. NIST SP 800-82 Rev. 3 and MITRE ATT&CK for ICS support the assessment.
Manufacturing OT
B8Do EU rules affect Indian exporters?
They can. As general information: the NIS2 Directive (transposition deadline 17 October 2024) raises supply-chain expectations on EU entities, which often reach suppliers through contracts. The Cyber Resilience Act (in force December 2024, vulnerability reporting from September 2026, main obligations December 2027) covers products with digital elements sold in the EU. Refer to the official texts for applicability.
Manufacturing OT
C. Engagement Approach and Delivery
C1How does an engagement start?
With a scoping call to confirm your sector, entity type and business lines. Codec Networks then lists the instruments and standards likely to be relevant, for your legal and compliance team to confirm, and agrees the scope and level.
C2What is a sector playbook?
A ready set for each sector: the relevant regulations and standards, a sector control library mapped to the unified control set, sector threat scenarios and a Board reporting template in that sector's language.
C3How do you avoid duplicate audits across frameworks?
Each requirement is mapped once to the unified control set. A single control, such as access review, then carries evidence for RBI, PCI DSS, SWIFT CSP, ISO/IEC 27001 and customer questionnaires at the same time.
BFSIMulti-sector group
C4How do you assess an OT plant?
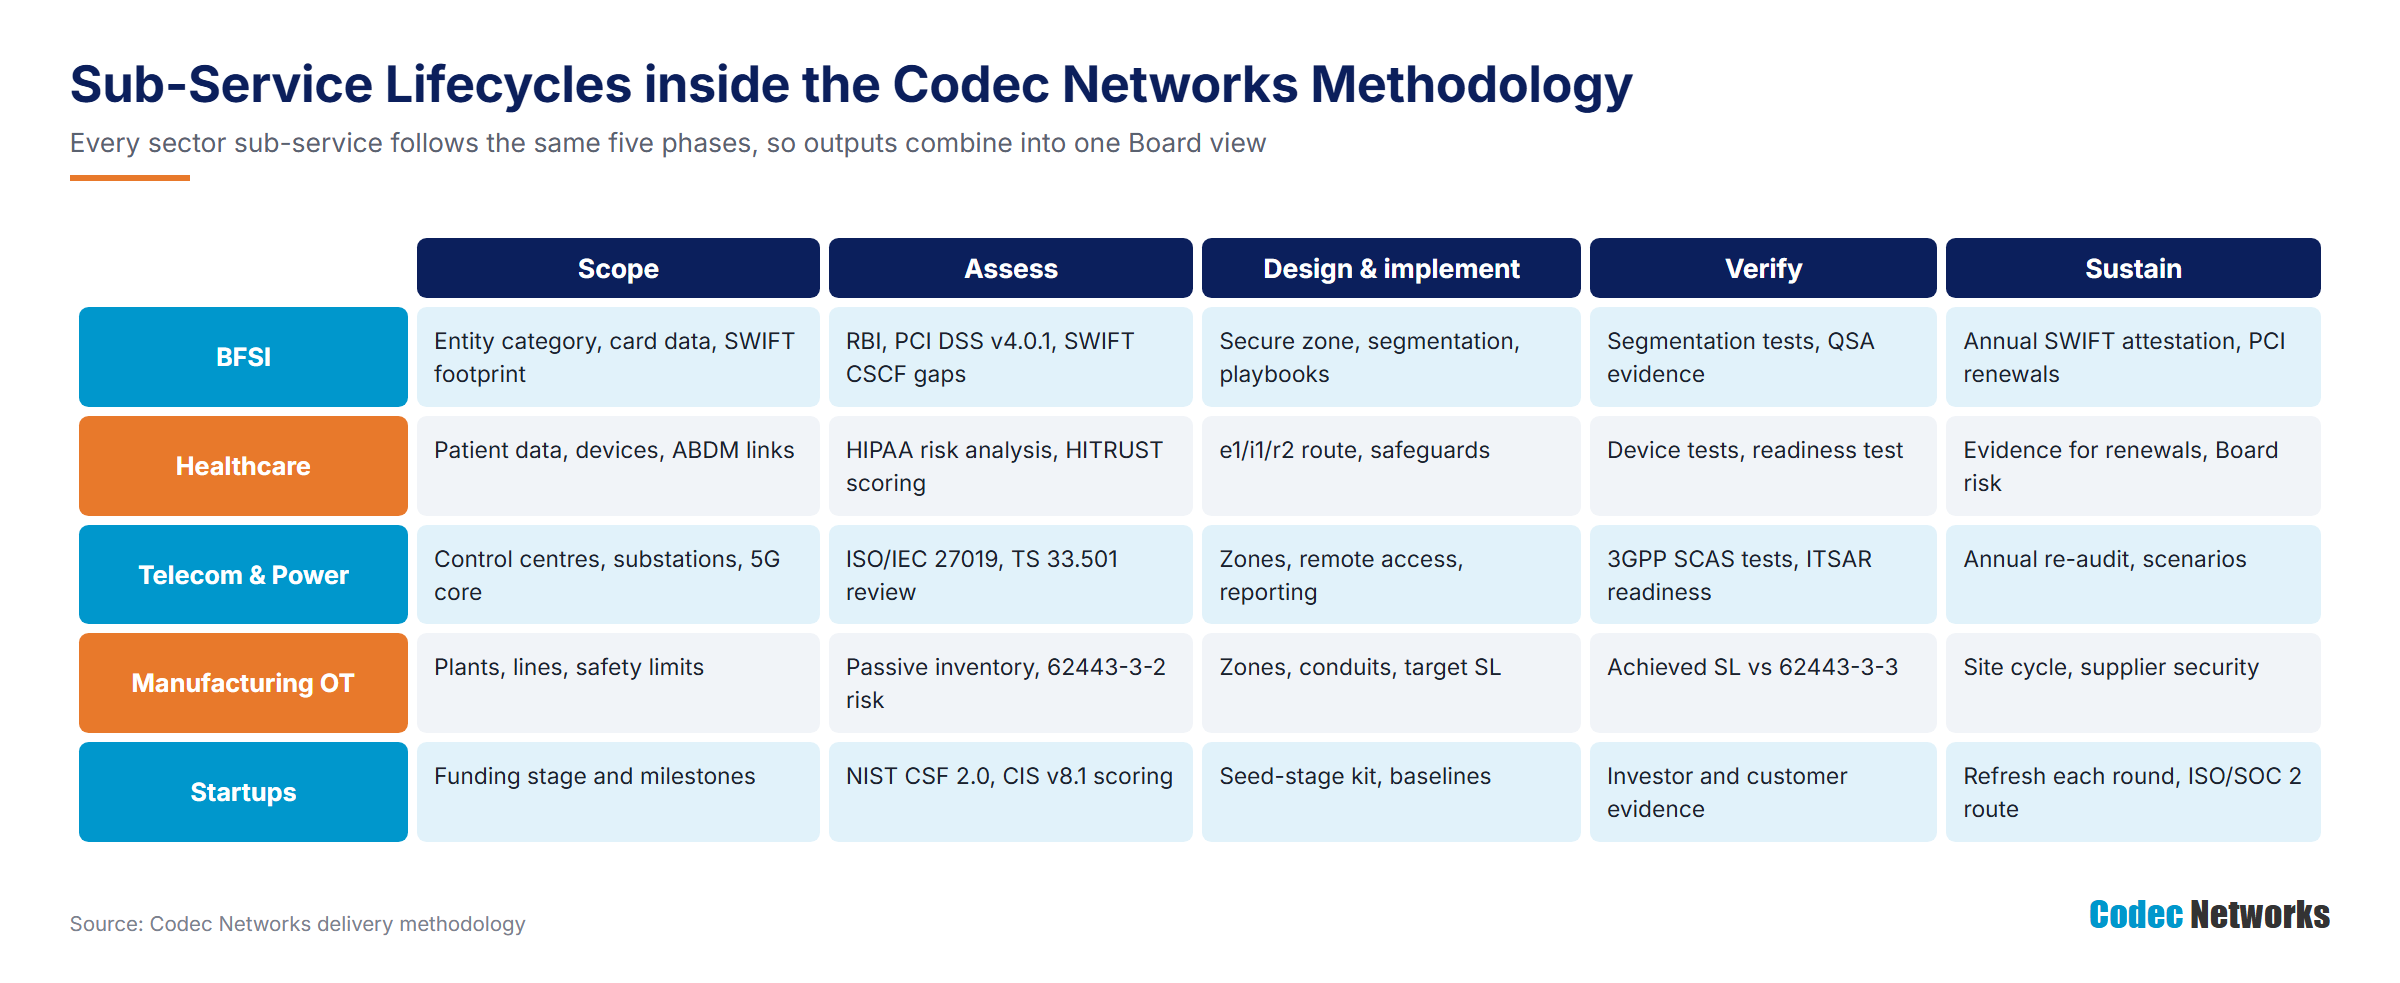
Following IEC 62443-3-2: build the asset inventory, define zones and conduits, assess risk, set target security levels, compare against IEC 62443-3-3 and agree a phased roadmap with the plant head. A site typically takes three to six weeks.
Manufacturing OT
C5How do you run a 5G security audit?
By reviewing the architecture against 3GPP TS 33.501, using GSMA NESAS and 3GPP SCAS as references for equipment assurance, checking ITSAR test evidence and testing with Codec Networks' in-house 5G testing team.
Telecom & Power
C6How do you treat third-party risk in BFSI?
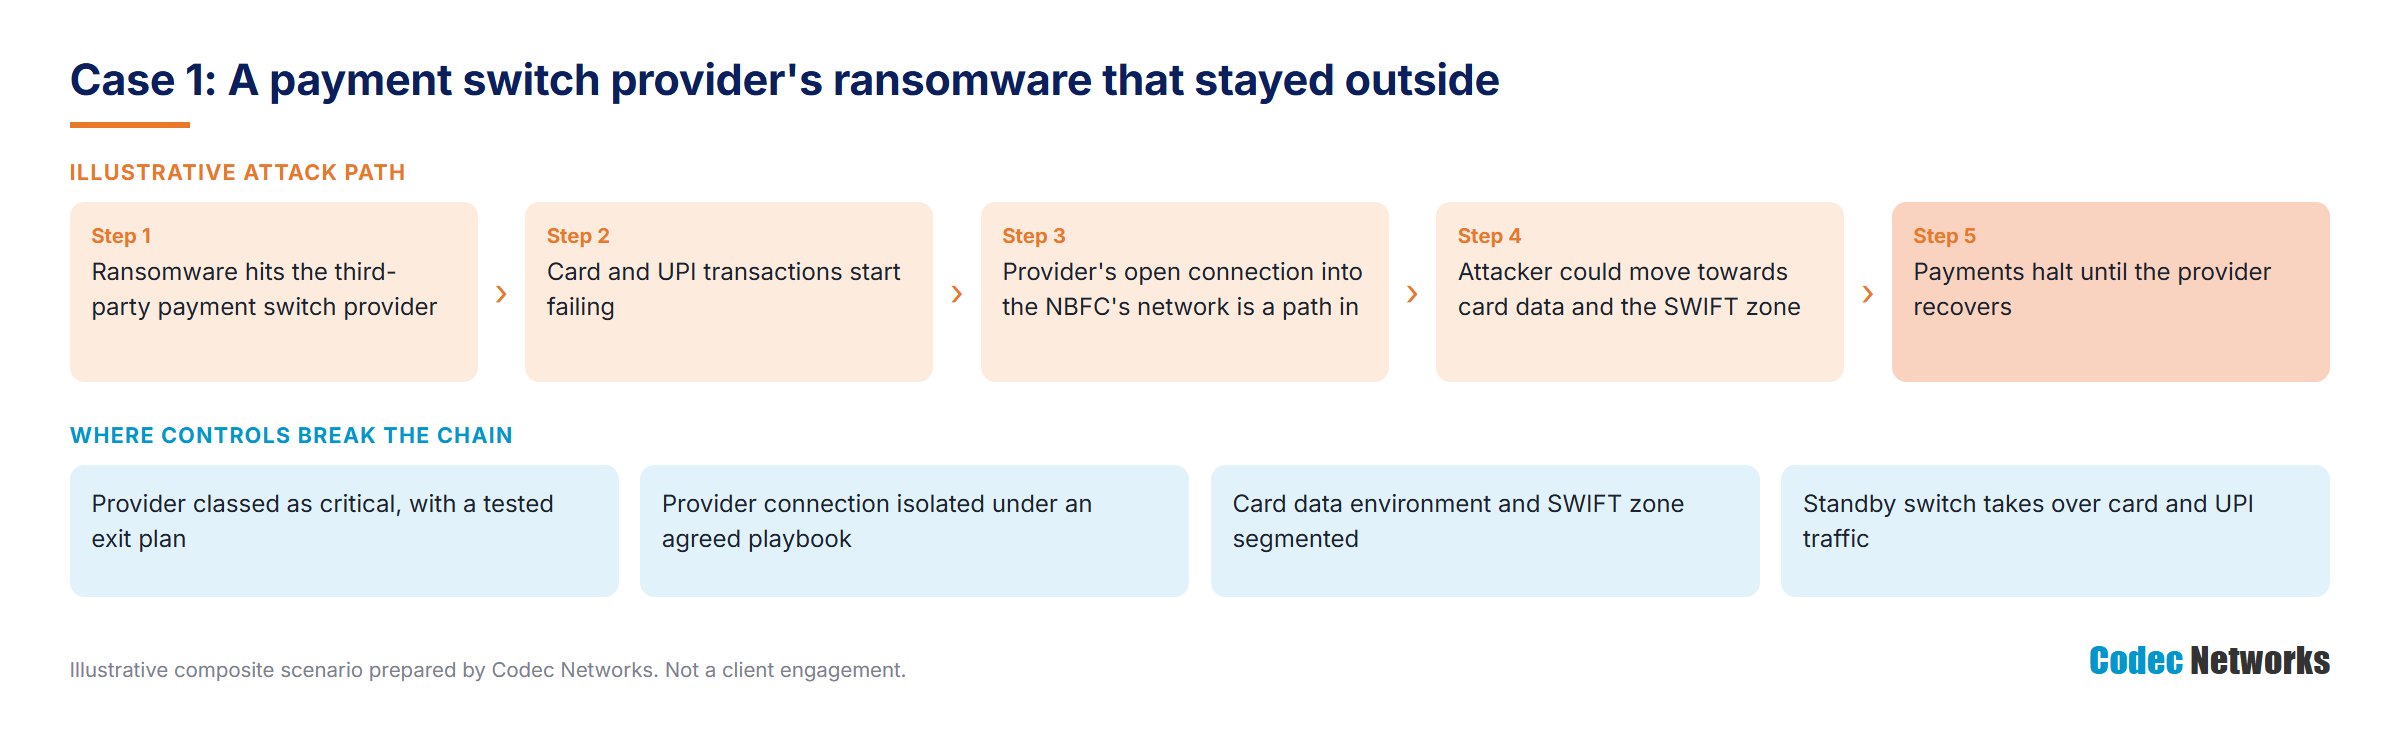
Critical providers such as payment switches, cloud and core banking vendors are identified, assessed and given tested exit plans. The C-Edge Technologies ransomware of July 2024, which disrupted payment services at around 300 small co-operative and regional rural banks, shows why.
BFSI
C7Who does the work?
Consultants holding CISSP, CISA, CISM, CRISC, CEH, OSCP and CHFI, ISO 27001 Lead Auditors and Implementers, DPOs and ICS/OT specialists, supported by in-house VAPT, OT/IoT testing, 5G testing, forensics, SOC, GRC and privacy teams.
C8Can you train our teams?
Yes. CoPE, Codec Networks' education wing, runs sector awareness and role-based training for Boards, compliance teams, plant engineers, clinicians and developers.
D. Commercials, Timelines and Effort
D1How is the service priced?
By sub-service, enterprise size and level. Document 7 gives indicative bands, for example from ₹6–9 lakh for a small BFSI Basic engagement to ₹45–70 lakh for a large Telecom & Power Advanced engagement, and from ₹2–4 lakh for a seed-stage startup.
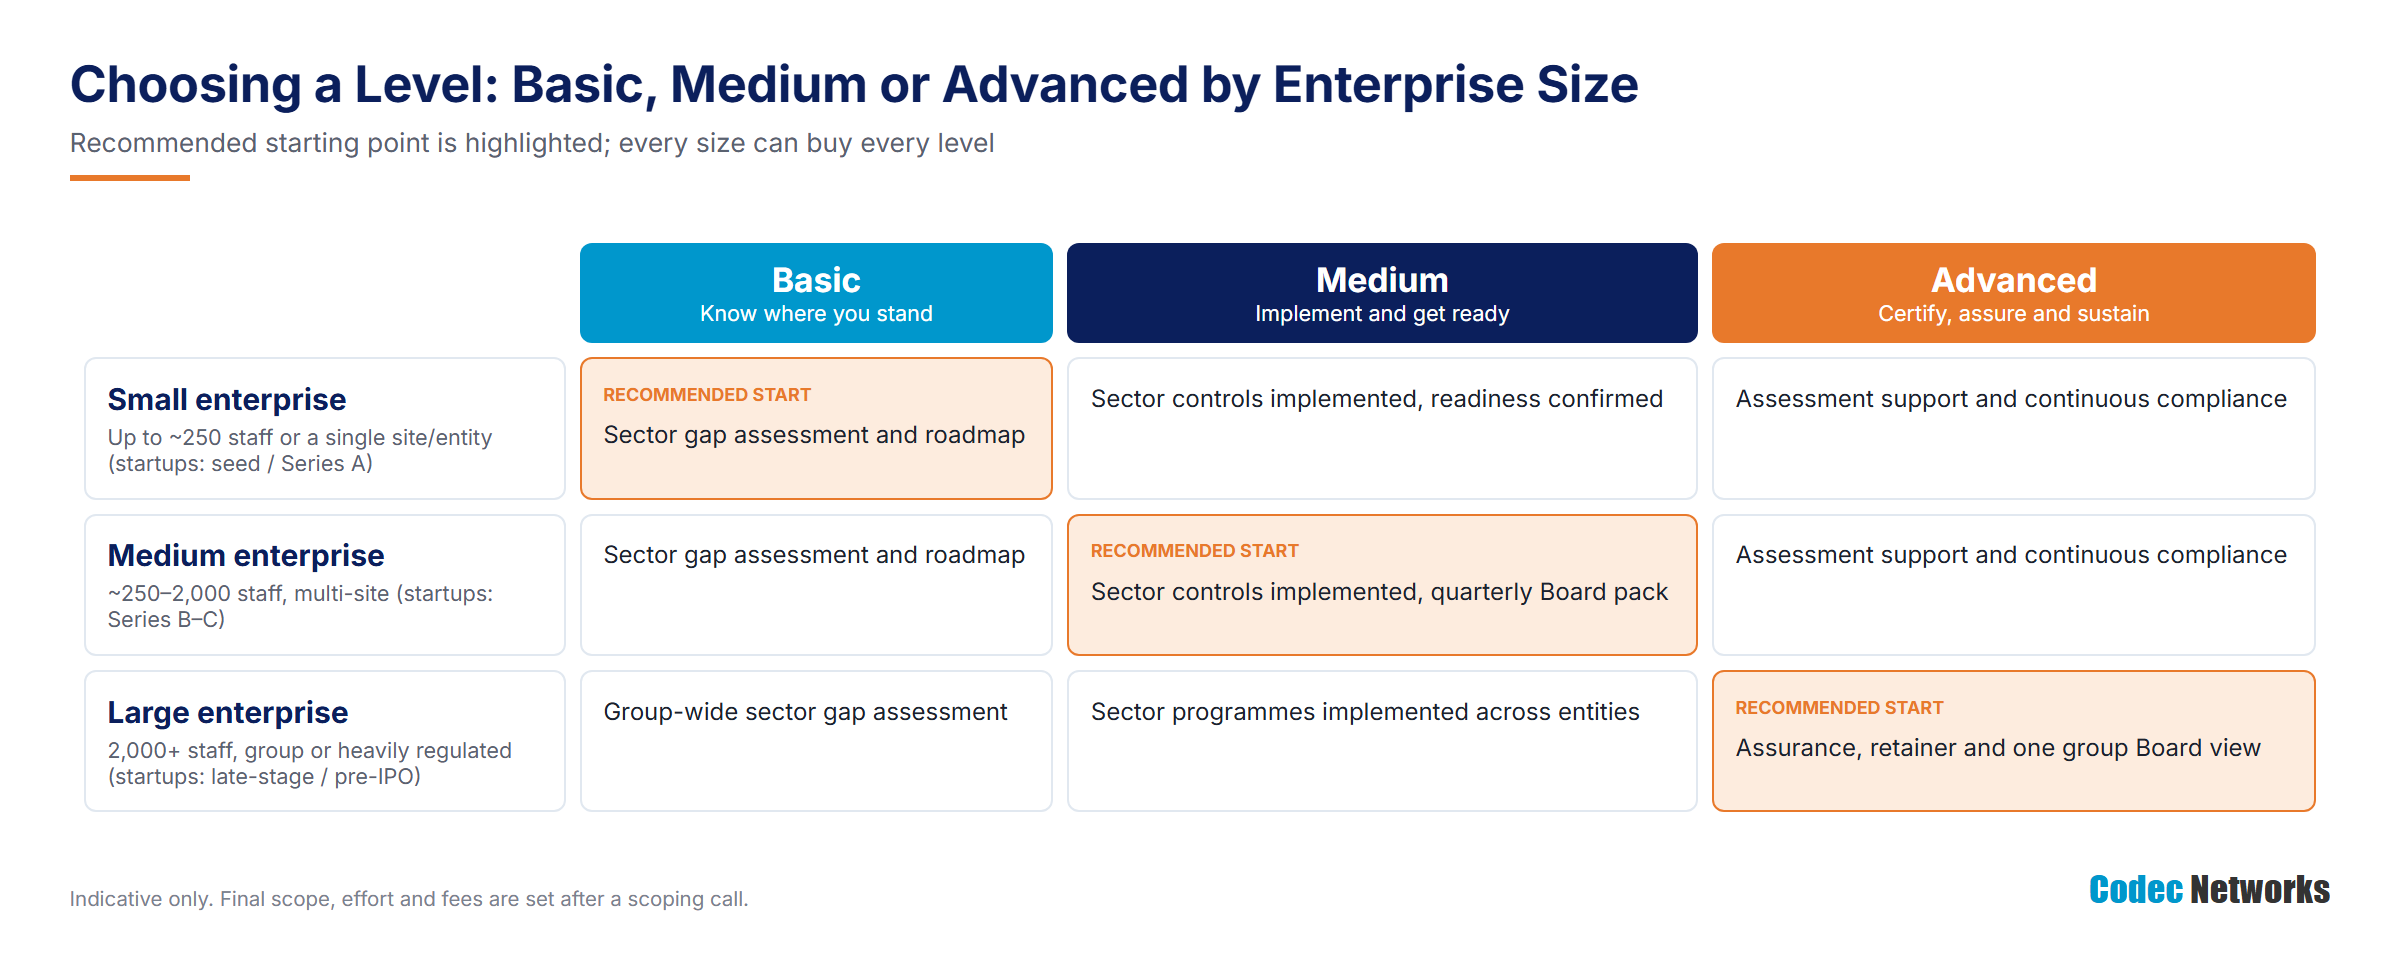
D2What do Basic, Medium and Advanced mean?
Basic is "Know where you stand": a gap assessment and roadmap. Medium is "Implement and get ready": controls, policies and evidence built. Advanced is "Certify, assure and sustain": support through audit, assessment or attestation and ongoing assurance.
D3How long does it take?
Typically four to six weeks for a BFSI gap assessment, eight to sixteen weeks for HIPAA or HITRUST readiness, six to ten weeks for an ISO/IEC 27019 or 5G audit, three to six weeks per OT site and two to four weeks for a startup baseline and kit.
BFSIHealthcareTelecom & PowerManufacturing OTStartups
D4How are OT assessments priced for many plants?
Per site, from ₹3–8 lakh per plant or substation depending on complexity. The first site sets the method, and later sites reuse it.
Manufacturing OTTelecom & Power
D5Can we pay per attestation each year?
Yes. Annual readiness for SWIFT CSP or PCI DSS can be priced per assessment, typically ₹4–8 lakh.
BFSI
D6Are bundles available?
Yes. Sector Starter (₹8–12 lakh) for startups and small regulated firms, Sector Assurance (₹30–50 lakh) for medium enterprises and Multi-Sector Group (from ₹90 lakh per year) for conglomerates under one Board view.
StartupsMulti-sector group
D7Do you offer a retainer?
Yes. A sector vCISO or compliance retainer costs ₹2–6 lakh per month. Hybrid models combine a fixed-scope project with a retainer.
D8Are QSA, HITRUST or certification body fees included?
No. Fees of your QSA, HITRUST External Assessor, certification body and any third-party tools are separate and paid by the client to those parties.
BFSIHealthcare
E. Reporting, Evidence and Ongoing Support
E1What will the Board pack show?
For each sector: status against relevant requirements, top sector threats, open gaps with owners, the attestation and audit calendar, and decisions the Board needs to take.
Multi-sector group
E2What evidence will auditors and assessors receive?
Requirement-to-control maps, policies and procedures, test and assessment reports, and an evidence register that links each control to its records.
E3How do you track changing rules and standards?
Codec Networks keeps a regulatory and standards watch for each sector and updates the control library each quarter. Changes are flagged to the client with their reference and date.
E4What happens in a major incident?
Codec Networks' forensics and incident response team supports containment and facts for reporting. As general information: CERT-In's Directions of 28 April 2022 (No. 20(3)/2022-CERT-In) provide for reporting specified incidents within six hours and keeping ICT logs for 180 days; refer to the official text for applicability.
E5How do you support annual attestations?
Through an attestation calendar: SWIFT CSP by 31 December, PCI DSS each year, HITRUST e1 and i1 each year and r2 every two years, with readiness checks planned ahead of each date.
BFSIHealthcare
E6Can you support investor due diligence?
Yes. Codec Networks prepares a security data room, answers investor questionnaires with evidence and briefs founders before diligence calls.
Startups
E7How does the DPDP Act fit into the plan?
As general information: the DPDP Act 2023 is in force and the DPDP Rules 2025 were notified in November 2025, with most Data Fiduciary obligations commencing in May 2027. Codec Networks builds privacy controls into each sector programme so they are ready in time.
Startups
E8How do you keep improving?
Through quarterly reviews, annual reassessments, new sector threat scenarios and updates for new rules and standard versions.