The 40 questions below are those Codec Networks hears most often from clients considering its GRC services. Each question is unique.
A. Service scope and client fit
A1We already have an IT security team. Why do we need GRC services?
Security teams run controls; GRC makes sure those controls match the organisation's risks, laws and contracts, are owned and evidenced, and are reported to leadership. Codec Networks works alongside your team, adding structure, independent validation and Board reporting rather than replacing anyone.
A2Which of the six sub-services should we start with?
It depends on your most pressing driver. Customer or tender demands usually point to ISO 27001 or SOC 2; personal data at scale points to DPDPA readiness; RBI or SEBI regulation points to a framework audit; heavy outsourcing points to TPRM. Codec Networks recommends an integrated gap assessment when several drivers apply.
A3We are a small company. Is GRC only for large enterprises?
No. Codec Networks' Basic level is designed for small enterprises: a focused gap assessment, core policies and a roadmap. Many small firms need ISO 27001 or DPDPA readiness to win contracts with larger customers.
A4Can you cover all our group companies in one engagement?
Yes. Codec Networks scopes multi-entity programmes with a common control set and group policies, and then assesses each entity against it, so the Board receives one consolidated view.
A5Does NIST CSF replace ISO 27001?
No. ISO 27001 is a certifiable management system standard; NIST CSF 2.0 is a voluntary framework for describing and governing cyber risk outcomes. Codec Networks often uses both: ISO 27001 to run security, and NIST CSF to explain risk to the Board.
A6We serve US and EU customers from India. Which frameworks apply?
Usually GDPR for EU personal data, CCPA / CPRA if you handle Californian consumer data for a covered business, HIPAA if you process US health data for a covered entity, PCI DSS if you handle card data, and SOC 2 if customers ask for an attestation. Codec Networks confirms this in an applicability assessment.
A7Do we still need DPDPA work if we are already GDPR compliant?
Yes, but less of it. GDPR work gives a strong base, yet the DPDP Act and Rules differ on consent, legitimate uses, children's data, breach intimation and Significant Data Fiduciary duties. Codec Networks maps your GDPR controls and closes only the differences.
A8How do we know which vendors need a deep assessment?
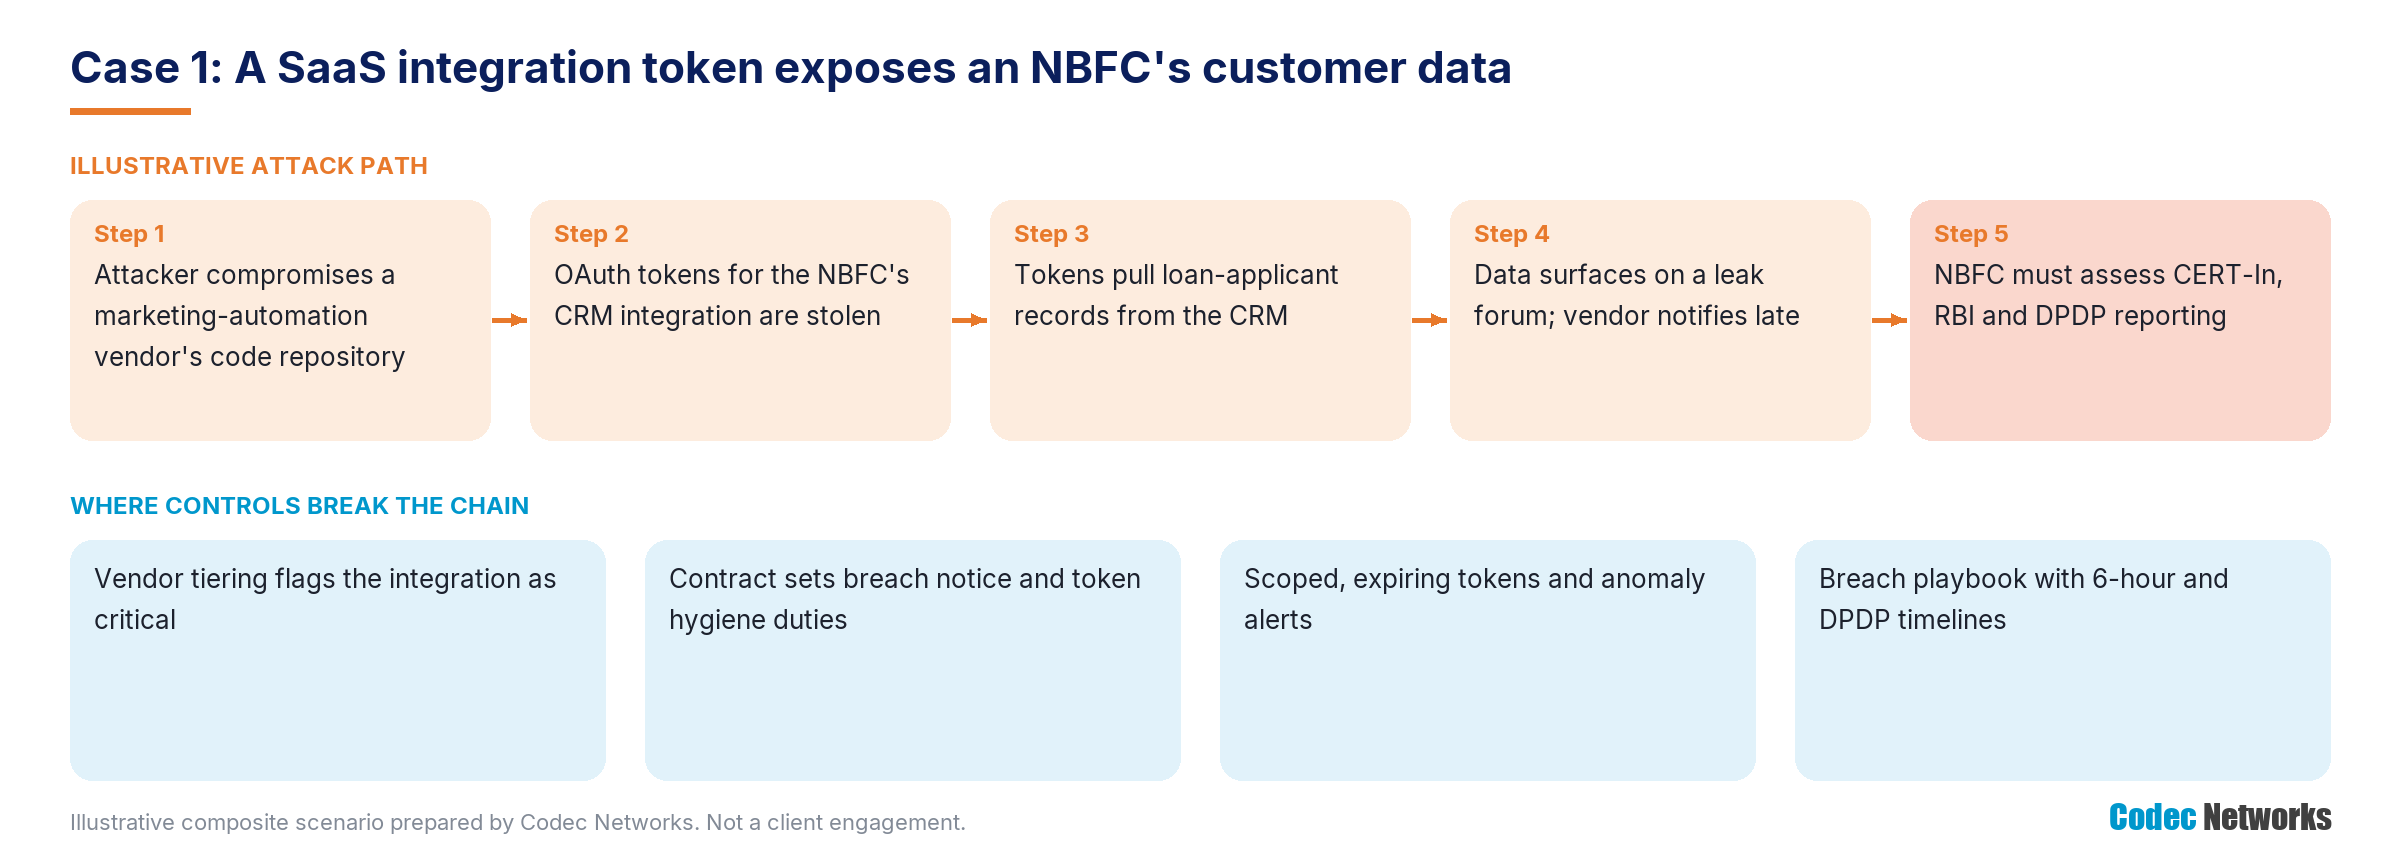
Codec Networks tiers every vendor by inherent risk: the data it handles, its access to your systems and how critical its service is. Only critical and high-risk vendors receive evidence reviews or on-site assessments; low-risk vendors get a light questionnaire.
B. Standards, laws and regulatory alignment
B1Our ISO 27001 certificate was on the 2013 version. What now?
Certificates to ISO/IEC 27001:2013 expired at the end of the transition period on 31 October 2025. If your certificate has lapsed, Codec Networks can perform a gap assessment against the 2022 version and support you through a fresh certification audit.
B2What changed in NIST CSF 2.0?
Version 2.0, published in February 2024, added a sixth function, Govern, covering strategy, roles, policy, oversight and cyber supply-chain risk management. It also extended the framework explicitly to organisations of all sizes and sectors.
B3When do DPDP obligations apply to us?
The DPDP Rules 2025 were notified on 13 November 2025 with phased commencement: consent manager provisions after twelve months and most Data Fiduciary obligations after eighteen months, in May 2027. Codec Networks plans readiness programmes to finish before those dates.
B4Is SEBI's CSCRF the same for every regulated entity?
No. As described in SEBI's circular of 20 August 2024 (SEBI/HO/ITD-1/ITD_CSC_EXT/P/CIR/2024/113) and later clarifications, expectations are graded by category of regulated entity. Codec Networks first confirms your category and then audits against the requirements for it.
B5Which RBI instruments do you audit against?
This depends on your licence and category. Commonly relevant instruments include the Cyber Security Framework in Banks (RBI/2015-16/418, 2016), the Master Direction on IT Governance, Risk, Controls and Assurance Practices (RBI/2023-24/107, 2023) and the Master Direction on Outsourcing of IT Services (RBI/2023-24/102, 2023), read with RBI's November 2025 consolidated directions. These are cited for client information only.
B6Can you certify us to ISO 27001 or issue our SOC 2 report?
No, and no consultant should. Certificates are issued by accredited certification bodies, SOC 2 reports by licensed CPA firms and PCI DSS Reports on Compliance by QSAs. Codec Networks prepares you, runs readiness tests and supports you during those independent audits.
B7How does PCI DSS v4.0.1 affect us?
Version 4.0.1 is the current standard, and requirements that were future-dated became effective on 31 March 2025, including stronger authentication and controls over scripts on payment pages. Codec Networks reviews your cardholder data scope and readiness against them.
B8Do CERT-In's 2022 Directions affect GRC work?
Yes. CERT-In's Directions of 28 April 2022 cover reporting specified incidents within six hours and retaining logs for 180 days. Codec Networks builds these into incident procedures, logging controls and breach playbooks.
C. Engagement approach and Codec Networks delivery
C1How does a typical engagement start?
With a scoping call and a document request, followed by a kick-off with your sponsor and control owners. Codec Networks then agrees the scope, plan, RACI and reporting cadence before assessment begins.
C2How much of our team's time will you need?
Most time is needed from control owners during interviews and evidence collection, typically a few hours per owner per phase. Codec Networks schedules work in blocks so day-to-day operations are not disrupted.
C3Can the work be done remotely?
Most of it, yes. Interviews, document review and many control tests are done remotely through secure sharing. On-site visits are planned for physical controls, data centres, critical vendors or where you prefer them.
C4How do you protect our evidence and documents?
Client evidence is handled under Codec Networks' own ISO/IEC 27001:2022 certified ISMS, with NDAs, need-to-know access and agreed retention and deletion at the end of the engagement.
C5Will you implement the controls for us?
Codec Networks designs controls, drafts policies and procedures, guides your teams and verifies implementation. Your teams own and operate the controls, which is also what certification bodies and regulators expect.
C6How do you avoid duplicate work across frameworks?
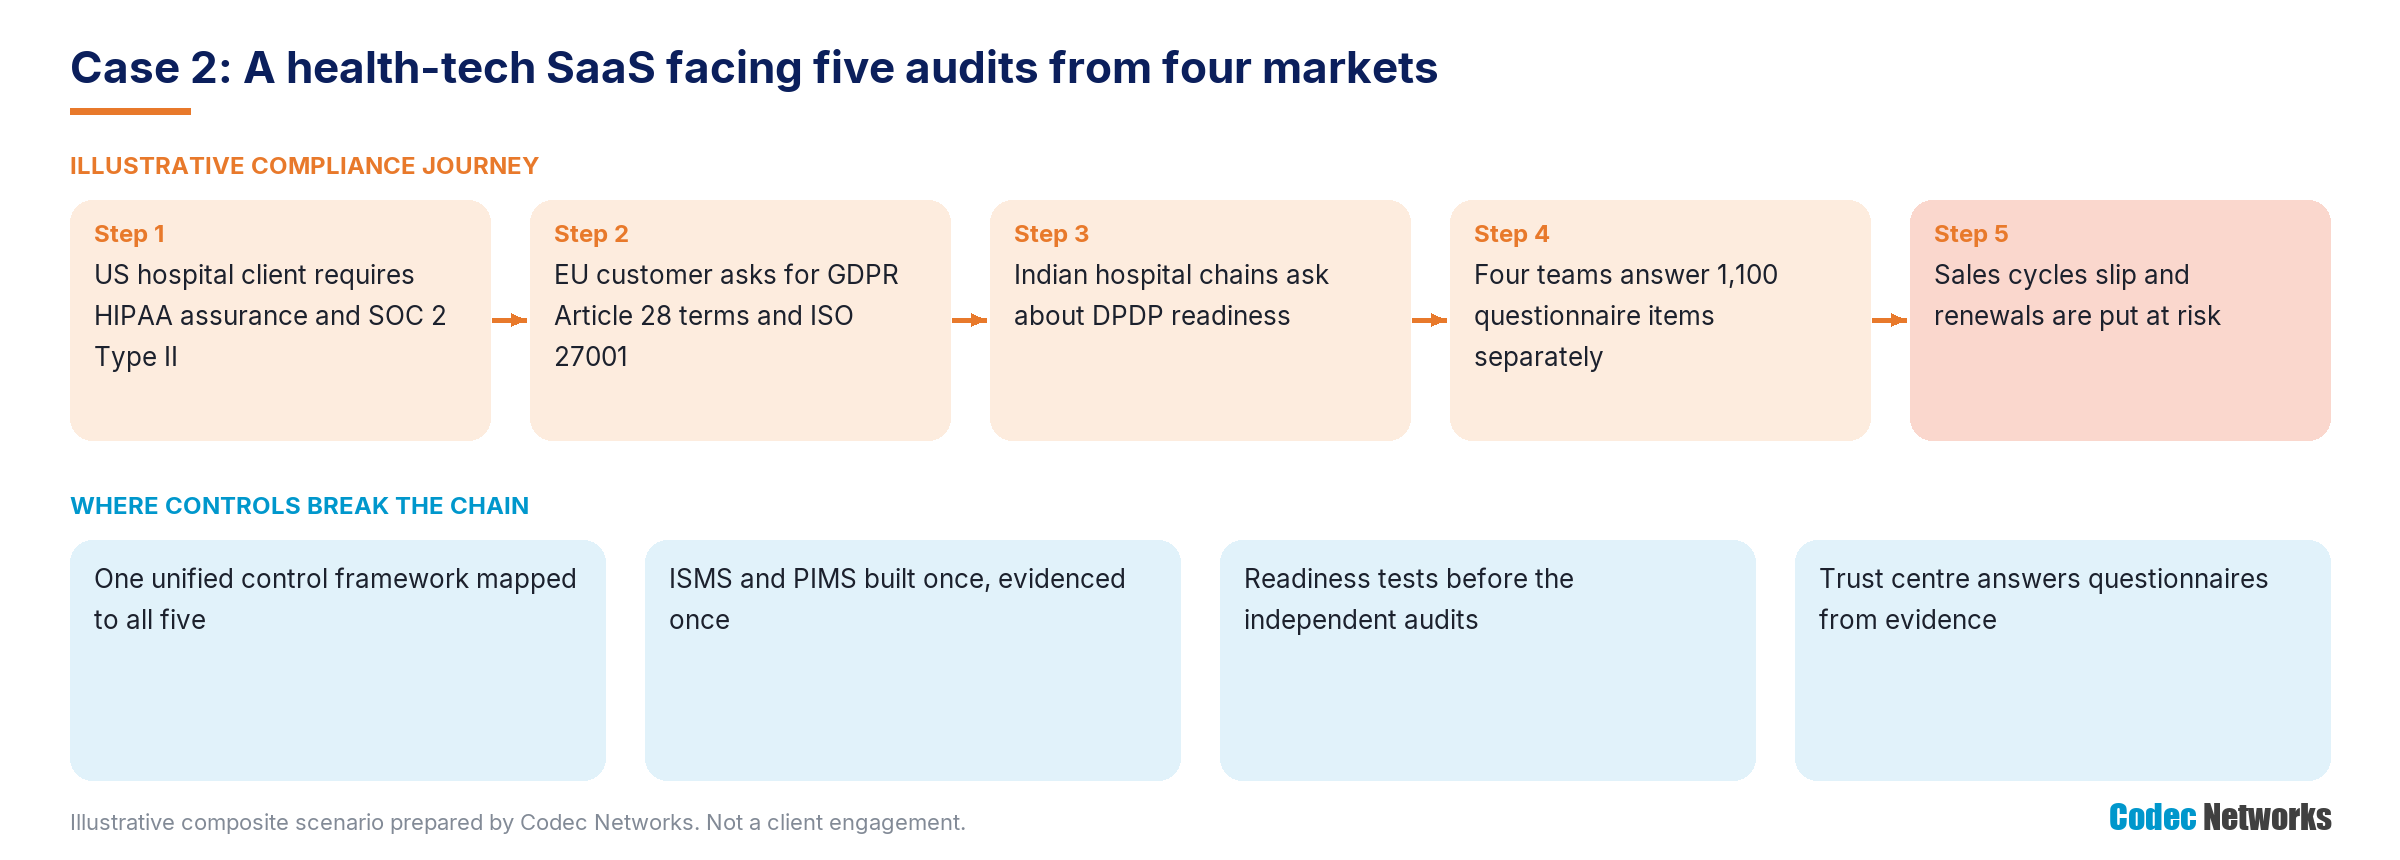
Codec Networks builds one unified control framework and maps each requirement of every applicable framework to it. Each control is tested and evidenced once and reused wherever it applies.
C7What happens if an audit finds a serious gap?
Codec Networks informs your sponsor promptly, records management's response and agrees a remediation plan. Critical findings are not held back for the final report.
C8Do you use technical testing in GRC engagements?
Where a control needs technical proof, yes: VAPT, configuration reviews, cloud posture reviews or phishing simulation, all done by Codec Networks' own teams with your written approval.
D. Commercials, timelines and effort
D1How is pricing decided?
By the level you choose (Basic, Medium or Advanced) and by scope drivers such as entities, locations, headcount, applications, frameworks and vendors. Document 7 gives indicative fee bands; a written proposal confirms them after scoping.
D2How long does ISO 27001 take from start to certificate?
Typically four to eight months to certification readiness, depending on scope and how quickly controls are implemented, followed by the certification body's Stage 1 and Stage 2 audits.
D3Are certification body or CPA fees included?
No. Fees paid to certification bodies, CPA firms, QSAs and tool vendors are paid by the client directly. Codec Networks' proposals list them separately so the total cost is clear.
D4Can we pay monthly instead of a large project fee?
Yes. Codec Networks offers retainers for continuous compliance, vCISO and DPO-as-a-service, and hybrid models where implementation is followed by a monthly retainer.
D5How is TPRM priced?
Either per vendor assessment, from about ₹25,000 to ₹2 lakh depending on tier, or as a monthly retainer for running the programme. Large vendor populations are usually handled in batches.
D6Do bundles cost less than individual services?
Yes. Because data mapping, risk assessment and evidence collection are done once, Codec Networks' Essentials, Professional and Enterprise bundles are priced below the sum of the individual services.
D7What if our scope changes mid-engagement?
Codec Networks raises a written change note with the effect on effort, fee and timeline, and proceeds only after your approval.
D8How quickly can you start?
Start dates are agreed in the proposal based on your timelines and consultant availability. Urgent needs, such as a customer audit deadline, can be scoped as a focused first phase.
E. Evidence, certification, Board reporting and ongoing support
E1What will our Board actually receive?
A short quarterly pack: top risks against appetite, KRIs, audit findings and closure, regulatory developments and decisions required. Codec Networks can present it to the Board or committee.
E2Can you put our cyber risk in rupee terms?
Yes, at the Advanced level of NIST CSF alignment. Codec Networks uses the FAIR model to estimate the likely frequency and size of losses for your top risks, which helps compare investments.
E3How do we keep compliant between audits?
Through an evidence calendar, periodic internal audits and a retainer under which Codec Networks reviews controls, tracks regulatory changes and updates policies and registers.
E4Will the outputs help with customer questionnaires?
Yes. The unified control framework and evidence library let your team answer customer security questionnaires consistently; at the Advanced level Codec Networks also supports a trust-centre style response pack.
E5Can Codec Networks act as our DPO or CISO?
Codec Networks provides DPO-as-a-service and vCISO support. Where the law requires a named officer, such as a Significant Data Fiduciary's Data Protection Officer based in India, Codec Networks advises on the appointment and supports the officer.
E6What do we get at the end of an RBI or SEBI audit?
An audit report with risk-rated findings and management responses, followed by closure validation. Codec Networks can also support your responses to regulator or exchange queries about the audit.
E7How do you track vendor risk after onboarding?
Vendors are reassessed on a schedule set by their tier, and incidents, certificate expiries and remediation items are tracked on a dashboard that Codec Networks summarises for management.
E8Will Codec Networks help with a real incident?
Yes. Codec Networks' incident response and forensics teams can support you, and the breach playbooks built in GRC engagements set out the CERT-In, DPDP and contractual notification steps to follow.