

On this page
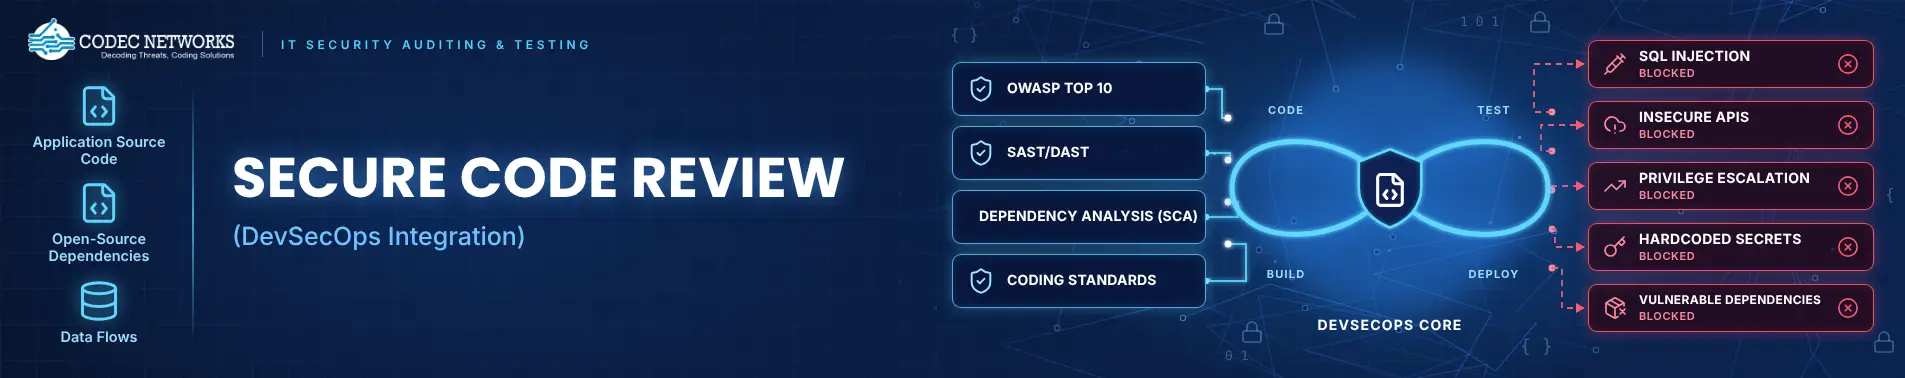
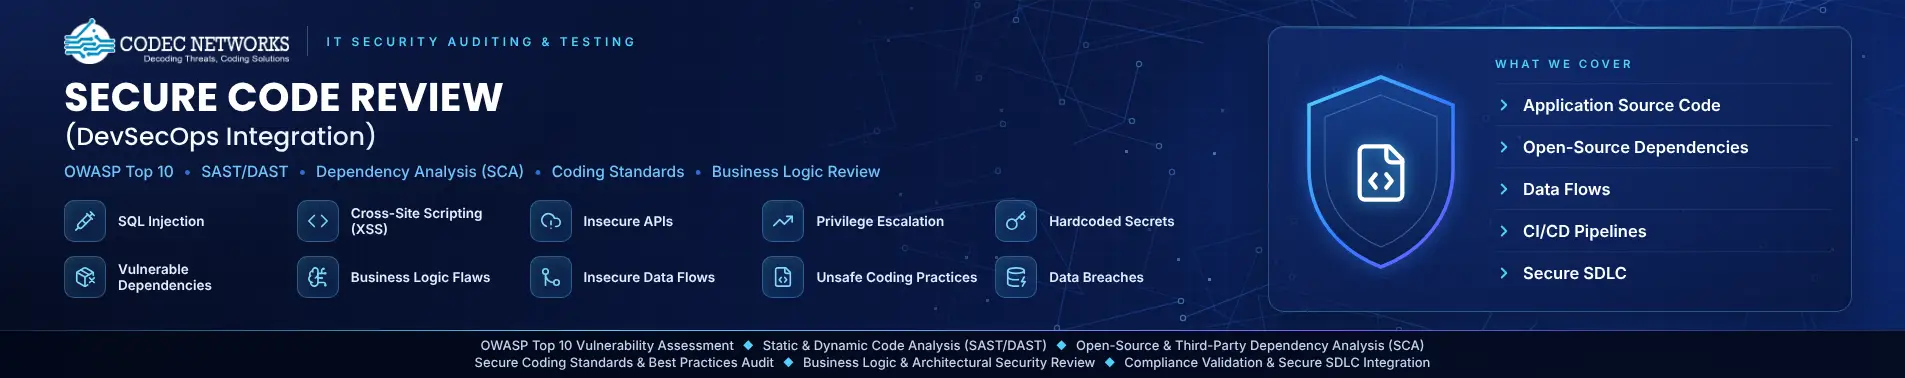

Secure Code Review (DevSecOps Integration)
The purpose of Secure Code Reviews is to identify and remediate security vulnerabilities hidden within the source code before they can be exploited. In today’s digital-first environment, where applications form the backbone of business operations, ensuring secure code is crucial to prevent data breaches, maintain compliance, and protect organizational reputation.
Secure Code Review is a systematic process of examining application source code to uncover security flaws, logic errors, and deviations from secure coding standards. Unlike functional testing, which validates what an application does, Secure Code Review focuses on how it does it—ensuring that code logic, data flows, and dependencies are resilient against common attack vectors such as SQL injection, cross-site scripting (XSS), insecure APIs, and privilege escalation.
Codec Networks’ Secure Code Review service integrates automated scanning tools with deep manual analysis by security experts to ensure comprehensive coverage of both known and hidden vulnerabilities. Our methodology aligns with OWASP standards, secure SDLC practices, and compliance frameworks like ISO 27001 and PCI DSS. By embedding security early in the development lifecycle, organizations can drastically reduce remediation costs, strengthen their software integrity, and achieve faster, safer deployments in dynamic DevSecOps environments.
Ultimately, this service empowers development teams to produce secure, high-quality code that upholds business continuity and customer trust in an increasingly threat-driven digital landscape.
Industry Significance
Secure Code Reviews protect software integrity by identifying and fixing vulnerabilities within source code. As businesses adopt software-driven operations, this service becomes essential for preventing cyberattacks, safeguarding intellectual property, strengthening reliability, and ensuring compliance across modern digital environments.
Read More
Service Relevance
Secure Code Reviews identify and fix hidden source-code vulnerabilities, ensuring application integrity and compliance. As organizations rely on software-driven operations, this service strengthens security, supports resilient digital transformation, and enables development teams to deliver trustworthy, high-performing, and secure applications.
Read More
Benefits to Customers
Secure Code Reviews help customers detect and fix code-level vulnerabilities early, improving application security, quality, and compliance. This ensures resilient, high-performing software that protects sensitive data, meets regulatory demands, reduces breach risks, and builds stronger customer trust in a fast-evolving digital environment.
Read More
Secure Code Review (DevSecOps Integration)
SERVICE FEATURES AND DELIVERY FRAMEWORK
Codec Networks delivers Secure Code Reviews through globally aligned methodologies, measurable outcomes,
and industry-leading standards that fortify software integrity and business resilience.
Secure Code Reviews identify and fix hidden source-code vulnerabilities, ensuring application integrity and compliance. As organizations rely on software-driven operations, this service strengthens security, supports resilient digital transformation, and enables development teams to deliver trustworthy, high-performing, and secure applications.
Codec Networks’ Secure Code Reviews service delivers a comprehensive evaluation of application source code to uncover security vulnerabilities, design flaws, and compliance gaps before software reaches production. By combining automated scanning with expert manual review, the service ensures that applications are secure by design, compliant with global standards, and resilient against modern cyber threats.
Our Secure Code Review features are built to help organizations improve software assurance, achieve early vulnerability detection, and maintain trust across digital products and development ecosystems.
Codec Networks offers these services across the following segments:
1. OWASP Top 10 Vulnerability Assessment
- Comprehensive Code Analysis: Examines application code for high-risk vulnerabilities aligned with OWASP Top 10 categories, including injection flaws and insecure authentication.
- Logic Flaw Identification: Detects business logic vulnerabilities that automated tools often miss, preventing abuse of workflows or privilege escalations.
- Cross-Site & Injection Testing: Validates input handling to prevent XSS, SQL, and command injection attacks.
- Error & Exception Handling Review: Ensures secure logging and exception management to prevent information disclosure.
- Automated Risk Prioritization: Categorizes issues by severity and exploitability for efficient remediation planning.
- Developer Remediation Guidance: Provides tailored fixes and recommendations to eliminate OWASP Top 10 vulnerabilities from codebases.
2. Static & Dynamic Code Analysis (SAST/DAST)
- Static Application Security Testing (SAST): Scans source code for syntax-level vulnerabilities, insecure coding patterns, and unsafe APIs.
- Dynamic Application Security Testing (DAST): Simulates runtime attacks to validate how applications behave under real-world threat scenarios.
- Integration with DevSecOps: Embeds automated testing within CI/CD pipelines for continuous vulnerability detection.
- Secure Code Validation: Ensures functions, data flows, and logic paths follow security best practices across modules.
- False Positive Reduction: Combines static and dynamic results for precise vulnerability validation and minimal noise.
- Risk-Based Reporting: Generates actionable findings with severity scoring and exploitability context for prioritized remediation.
3. Open-Source & Third-Party Dependency Analysis (SCA)
- Dependency Vulnerability Mapping: Identifies outdated, vulnerable, or malicious open-source libraries within the application.
- License & Compliance Validation: Reviews third-party components for licensing risks and regulatory conflicts.
- Automated Component Tracking: Continuously monitors dependency changes across development cycles.
- Exploit Intelligence Integration: Correlates vulnerabilities with real-world threat intelligence for timely mitigation.
- Version Management Recommendations: Suggests secure upgrade paths and patch strategies for risky components.
- Software Bill of Materials (SBOM): Generates an SBOM for visibility and compliance in software supply chain management.
4. Secure Coding Standards & Best Practices Audit
- Code Quality & Maintainability Review: Assesses structure, readability, and maintainability to support long-term security hygiene.
- Input Validation & Output Encoding Checks: Ensures safe handling of user data and protection against injection vectors.
- Session & Authentication Validation: Reviews session management and access controls for proper enforcement.
- Error Handling & Logging Practices: Ensures sensitive data isn’t exposed in logs or error messages.
- Documentation & Coding Consistency: Promotes standardized practices to strengthen developer collaboration and audit readiness.
5. Business Logic & Architectural Security Review
- Application Flow Assessment: Analyzes business logic for potential abuse scenarios or design flaws leading to privilege misuse.
- Threat Modeling Integration: Identifies attack surfaces using STRIDE and PASTA frameworks for architecture-level defense.
- API & Microservice Security Review: Validates access controls, rate limiting, and data validation in service interactions.
- Data Flow & Trust Boundary Validation: Ensures proper handling of sensitive data between internal and external components.
- Authentication & Authorization Checks: Confirms robust identity enforcement and session token handling.
- Architecture Hardening Recommendations: Provides structural improvements for secure and scalable application design.
6. Compliance Validation & Secure SDLC Integration
- Regulatory Framework Alignment: Maps code review findings to PCI DSS, GDPR, HIPAA, and ISO 27001 requirements.
- Secure Development Lifecycle (SDLC) Integration: Embeds code review checkpoints across design, build, and deployment phases.
- Continuous Monitoring Enablement: Establishes recurring review cycles for ongoing assurance in agile and DevSecOps environments.
- Metrics & Maturity Tracking: Measures code quality, vulnerability density, and remediation performance over time.
- Developer Awareness Programs: Provides training on secure coding principles, reinforcing long-term application security culture.
- Audit-Ready Reporting: Delivers comprehensive reports for compliance audits, executive summaries, and technical validation.
Codec Networks follows a structured and standards-aligned Secure Code Review Delivery Methodology, designed to integrate security seamlessly into the software development lifecycle (SDLC). This methodology is aligned with global best practices and frameworks such as OWASP ASVS, ISO/IEC 27034, NIST SP 800-53, ensuring that every engagement delivers measurable security assurance, compliance readiness, and resilient application architectures. Codec Networks’ overall Service Delivery Methodology comprises of:
1. Project Initiation & Scoping
- Requirement Gathering: Engage with stakeholders to define objectives, application scope, languages, and technology stacks under review.
- Engagement Definition: Identify code modules, repositories, APIs, and third-party components in scope.
- Risk Prioritization: Classify applications based on criticality, data sensitivity, and business impact.
- Project Charter Finalization: Establish scope of work, timelines, communication cadence, and escalation matrix.
- Governance Framework Setup: Define reporting hierarchy, review checkpoints, and documentation standards.
2. Pre-Engagement Compliance & Environment Preparation
- Authorization & Legal Readiness: Execute NDAs, testing agreements, and secure access protocols.
- Rules of Engagement (RoE): Define testing scope boundaries, data handling requirements, and rollback procedures.
- Environment Validation: Verify that code repositories and test environments are isolated and pre-approved for analysis.
- Access Provisioning: Establish secure access credentials for version control systems (e.g., Git, SVN).
- Toolchain Preparation: Configure automated SAST, SCA, and manual review utilities in controlled environments.
3. Application Architecture & Threat Modeling
- Architecture Understanding: Review application flow diagrams, components, and data exchange mechanisms.
- Trust Boundary Mapping: Identify sensitive data flows, external interfaces, and API endpoints.
- Threat Modeling: Apply STRIDE or PASTA methodologies to predict potential attack vectors.
- Security Control Review: Assess implementation of existing security mechanisms and libraries.
- Architecture Hardening Inputs: Recommend design-level improvements to reduce exposure and attack surfaces.
4. Static Application Security Testing (SAST)
- Automated Source Code Scanning: Analyze code using SAST tools to detect insecure functions and syntax-level issues.
- Rule Set Customization: Tailor scanning policies for language, framework, and application type.
- Pattern Detection: Identify vulnerabilities such as SQL injection, XSS, buffer overflows, and insecure API calls.
- Result Validation: Manually verify automated findings to reduce false positives.
- Preliminary Reporting: Deliver initial findings highlighting high-severity issues for early mitigation.
5. Manual Secure Code Review
- Line-by-Line Analysis: Conduct deep manual inspection to uncover logic flaws missed by automated tools.
- Authentication & Authorization Review: Validate access control enforcement, session management, and privilege boundaries.
- Data Validation & Encoding Checks: Ensure secure handling of input/output to prevent injection attacks.
- Error Handling & Logging Assessment: Review exception management and logging practices for sensitive data exposure.
6. Open-Source & Dependency Risk Analysis (SCA)
- Third-Party Library Review: Identify outdated, vulnerable, or unlicensed open-source components.
- Dependency Chain Validation: Analyze nested dependencies for transitive risks.
- License & Compliance Review: Ensure adherence to open-source license policies and regulations.
- Patch & Version Recommendations: Suggest safe upgrade paths for outdated libraries.
- SBOM Generation: Provide Software Bill of Materials (SBOM) for transparency and compliance validation.
7. Business Logic & API Security Review
- Logic Flow Validation: Examine functional processes for flaws in authorization and transaction handling.
- API Security Testing: Review API endpoints for authentication, rate limiting, and data leakage.
- Data Flow Analysis: Assess integrity and confidentiality of data exchanged between services.
- Session Management Review: Validate timeout policies, token handling, and cookie security.
- Abuse Case Simulation: Identify potential misuse or circumvention scenarios through logic manipulation.
8. Risk Analysis & Vulnerability Validation
- Vulnerability Classification: Assign severity levels based on CVSS and OWASP risk ratings.
- Correlation & Consolidation: Merge results from automated, manual, and SCA findings.
- False Positive Elimination: Re-validate vulnerabilities to confirm exploitability and relevance.
- Root Cause Identification: Analyze coding patterns or development practices causing recurring issues.
- Impact Analysis: Map vulnerabilities to potential data, compliance, or operational risks.
9. Reporting, Recommendations & Compliance Mapping
- Comprehensive Technical Report: Document identified vulnerabilities, root causes, and proof-of-concept validations.
- Executive Summary: Provide risk overview, mitigation priorities, and strategic insights for management.
- Compliance Mapping: Correlate vulnerabilities to ISO 27001, PCI DSS, GDPR, and NIST controls.
- Remediation Roadmap: Recommend short-term fixes and long-term secure coding improvements.
- Stakeholder Presentation: Conduct review sessions to explain findings and strategic implications.
10. Remediation Support, Retesting & Continuous Improvement
- Remediation Workshops: Collaborate with developers to implement secure fixes and code improvements.
- Re-Testing & Verification: Validate corrected vulnerabilities and ensure closure of findings.
- Continuous Code Assurance: Integrate review processes into SDLC for ongoing security validation.
- Metrics & Performance Evaluation: Track KPIs such as vulnerability density, MTTD, and MTTR.
- Knowledge Transfer & Training: Conduct secure coding workshops to enhance in-house developer security awareness.
|
Standard / Framework |
Standard Title / Description |
Relevance to Secure Code Review (DevSecOps Integration) |
Application in Service Delivery |
|
ISO/IEC 27001:2022 |
Information Security, Cybersecurity and Privacy Protection – ISMS |
Establishes a framework for implementing and maintaining robust information security controls. |
Ensures secure code review and data handling processes adhere to ISMS controls (Annex A.14 – System Acquisition, Development & Maintenance). |
|
ISO/IEC 27034:2011 |
Application Security – Secure Software Development Lifecycle Framework |
Defines principles and processes for integrating security throughout the software lifecycle. |
Forms the foundation for secure coding practices, process validation, and DevSecOps integration. |
|
ISO/IEC 27005:2022 |
Information Security Risk Management |
Provides methodologies for assessing and managing information security risks. |
Applied to evaluate and prioritize vulnerabilities identified during secure code reviews. |
|
NIST SP 800-53 Rev.5 |
Security and Privacy Controls for Information Systems and Organizations |
Offers a comprehensive catalog of security and privacy controls. |
Used to map vulnerabilities and controls within SA (System & Services Acquisition) and SC (System & Communication Protection). |
|
NIST SP 800-64 Rev.2 |
Security Considerations in the System Development Life Cycle |
Guides integration of security practices throughout SDLC phases. |
Ensures security is built into the design, development, testing, and deployment stages. |
|
NIST SP 800-218 (SSDF) |
Secure Software Development Framework |
Establishes secure design and coding practices for developers and organizations. |
Applied to align DevSecOps pipelines and secure coding standards with U.S. and global practices. |
|
OWASP ASVS v4.0.3 |
Application Security Verification Standard |
Provides structured levels of verification for assessing application security. |
Used to benchmark application security maturity and review code against ASVS control requirements. |
|
OWASP Top 10 (2021) |
The ten most critical web application security risks. |
Identifies the most common and impactful coding vulnerabilities. |
Serves as a baseline for detecting, classifying, and mitigating common application security risks. |
|
SANS CWE Top 25 |
Common Weakness Enumeration – Most Dangerous Software Errors |
Lists the most frequent and severe software vulnerabilities. |
Used to prioritize remediation of high-impact code weaknesses during reviews. |
|
CERT Secure Coding Standards |
Language-specific secure coding guidelines (C/C++, Java, .NET, etc.) |
Promotes consistency and safety in coding practices. |
Enforced during manual code review to eliminate unsafe coding constructs and logic flaws. |
|
ISO/IEC 12207:2017 |
Systems and Software Engineering – Software Life Cycle Processes |
Establishes standardized processes for software development and maintenance. |
Ensures code review activities are integrated into structured SDLC governance and QA processes. |
|
CIS Controls v8 |
Center for Internet Security Critical Security Controls |
Defines prioritized best practices for safeguarding systems and applications. |
Aligns secure code review outcomes with critical controls such as secure configuration and vulnerability management. |
|
MITRE ATT&CK Framework |
Adversarial Tactics, Techniques, and Common Knowledge |
Documents real-world attacker tactics and exploit techniques. |
Used to simulate adversarial behaviors during dynamic testing and correlate vulnerabilities with attack vectors. |
|
PCI DSS v4.0 |
Payment Card Industry Data Security Standard |
Specifies security requirements for applications handling cardholder data. |
Ensures reviewed applications in payment ecosystems meet PCI DSS software and data security standards. |
|
ISO/IEC 27017:2015 |
Code of Practice for Information Security Controls for Cloud Services |
Provides guidance for securing cloud-based applications and environments. |
Applied to assess and review applications deployed in cloud and SaaS environments for compliance and security. |
Please Note:
- Services are aligned with recognized international standards; however, alignment does not constitute formal certification or guarantee of compliance.
- Applicable standards are adopted based on scope, and not all controls or requirements may be fully covered within the engagement.
- Interpretations of standards are based on industry best practices and may vary depending on regulatory or jurisdictional expectations.
- Deliverables represent point-in-time assessments and may not reflect ongoing compliance with evolving international standards.
- Codec Networks does not assume responsibility for client implementation of controls required to achieve or maintain compliance.
- Use of international standards frameworks does not eliminate all security risks or ensure immunity from cyber incidents.
- Any references to standards are advisory and should not be considered as legal, regulatory, or certification authority endorsement.
- Client environments, configurations, and operational practices may impact the applicability and effectiveness of standard-based recommendations.
- Total liability for all services is strictly limited to the international standards as far as possible as agreed in contracted engagement value. Codec Networks expressly excludes any indirect, financial, operational, incidental, punitive, or consequential damages, which may arise due to any coincidental events, or changes in international standards guidelines time to time
Secure Code Reviews identify and fix hidden source-code vulnerabilities, ensuring application integrity and compliance. As organizations rely on software-driven operations, this service strengthens security, supports resilient digital transformation, and enables development teams to deliver trustworthy, high-performing, and secure applications.
Codec Networks’ Secure Code Reviews service delivers a comprehensive evaluation of application source code to uncover security vulnerabilities, design flaws, and compliance gaps before software reaches production. By combining automated scanning with expert manual review, the service ensures that applications are secure by design, compliant with global standards, and resilient against modern cyber threats.
Our Secure Code Review features are built to help organizations improve software assurance, achieve early vulnerability detection, and maintain trust across digital products and development ecosystems.
Codec Networks offers these services across the following segments:
1. OWASP Top 10 Vulnerability Assessment
- Comprehensive Code Analysis: Examines application code for high-risk vulnerabilities aligned with OWASP Top 10 categories, including injection flaws and insecure authentication.
- Logic Flaw Identification: Detects business logic vulnerabilities that automated tools often miss, preventing abuse of workflows or privilege escalations.
- Cross-Site & Injection Testing: Validates input handling to prevent XSS, SQL, and command injection attacks.
- Error & Exception Handling Review: Ensures secure logging and exception management to prevent information disclosure.
- Automated Risk Prioritization: Categorizes issues by severity and exploitability for efficient remediation planning.
- Developer Remediation Guidance: Provides tailored fixes and recommendations to eliminate OWASP Top 10 vulnerabilities from codebases.
2. Static & Dynamic Code Analysis (SAST/DAST)
- Static Application Security Testing (SAST): Scans source code for syntax-level vulnerabilities, insecure coding patterns, and unsafe APIs.
- Dynamic Application Security Testing (DAST): Simulates runtime attacks to validate how applications behave under real-world threat scenarios.
- Integration with DevSecOps: Embeds automated testing within CI/CD pipelines for continuous vulnerability detection.
- Secure Code Validation: Ensures functions, data flows, and logic paths follow security best practices across modules.
- False Positive Reduction: Combines static and dynamic results for precise vulnerability validation and minimal noise.
- Risk-Based Reporting: Generates actionable findings with severity scoring and exploitability context for prioritized remediation.
3. Open-Source & Third-Party Dependency Analysis (SCA)
- Dependency Vulnerability Mapping: Identifies outdated, vulnerable, or malicious open-source libraries within the application.
- License & Compliance Validation: Reviews third-party components for licensing risks and regulatory conflicts.
- Automated Component Tracking: Continuously monitors dependency changes across development cycles.
- Exploit Intelligence Integration: Correlates vulnerabilities with real-world threat intelligence for timely mitigation.
- Version Management Recommendations: Suggests secure upgrade paths and patch strategies for risky components.
- Software Bill of Materials (SBOM): Generates an SBOM for visibility and compliance in software supply chain management.
4. Secure Coding Standards & Best Practices Audit
- Code Quality & Maintainability Review: Assesses structure, readability, and maintainability to support long-term security hygiene.
- Input Validation & Output Encoding Checks: Ensures safe handling of user data and protection against injection vectors.
- Session & Authentication Validation: Reviews session management and access controls for proper enforcement.
- Error Handling & Logging Practices: Ensures sensitive data isn’t exposed in logs or error messages.
- Documentation & Coding Consistency: Promotes standardized practices to strengthen developer collaboration and audit readiness.
5. Business Logic & Architectural Security Review
- Application Flow Assessment: Analyzes business logic for potential abuse scenarios or design flaws leading to privilege misuse.
- Threat Modeling Integration: Identifies attack surfaces using STRIDE and PASTA frameworks for architecture-level defense.
- API & Microservice Security Review: Validates access controls, rate limiting, and data validation in service interactions.
- Data Flow & Trust Boundary Validation: Ensures proper handling of sensitive data between internal and external components.
- Authentication & Authorization Checks: Confirms robust identity enforcement and session token handling.
- Architecture Hardening Recommendations: Provides structural improvements for secure and scalable application design.
6. Compliance Validation & Secure SDLC Integration
- Regulatory Framework Alignment: Maps code review findings to PCI DSS, GDPR, HIPAA, and ISO 27001 requirements.
- Secure Development Lifecycle (SDLC) Integration: Embeds code review checkpoints across design, build, and deployment phases.
- Continuous Monitoring Enablement: Establishes recurring review cycles for ongoing assurance in agile and DevSecOps environments.
- Metrics & Maturity Tracking: Measures code quality, vulnerability density, and remediation performance over time.
- Developer Awareness Programs: Provides training on secure coding principles, reinforcing long-term application security culture.
- Audit-Ready Reporting: Delivers comprehensive reports for compliance audits, executive summaries, and technical validation.
SECURE CODE REVIEW (DEVSECOPS INTEGRATION)-CODEC NETWORK’S INDUSTRY OFFERINGS
Codec Networks delivers bundled security offerings integrating DevSecOps, risk advisory, and compliance for scalable, enterprise-grade protection.
Foundation Tier
Target Clients:
Small enterprises, startups, and early-stage technology firms developing web or mobile applications seeking essential code security hygiene and vulnerability prevention.
Sub-Services in Scope :
- Automated Static Code Analysis (Essential SAST)
- Open-Source Dependency Review (SCA Lite)
- Secrets & Credential Exposure Detection
- OWASP Top 10 Vulnerability Check
- Basic Compliance & Reporting Alignment
- Quick-Fix Recommendations & Developer Briefing
Objective:
Establish baseline application security by identifying coding flaws, insecure dependencies, and common vulnerabilities early in the software development lifecycle (SDLC).
Value Delivered:
Ideal for cost-conscious or emerging organizations, this tier provides affordable, foundational code assurance — improving visibility, developer awareness, and security posture before application deployment.
Enhanced Protection Tier
Target Clients:
Mid-sized enterprises, SaaS providers, and regulated-sector organizations with growing applications and increasing compliance obligations seeking a deeper and continuous code assurance model.
Sub-Services in Scope:
- Comprehensive Static & Manual Code Review (SAST + Expert Validation)
- Software Composition Analysis (SCA Advanced)
- Business Logic & Authentication Review
- Secure Coding Standards Assessment
- Compliance & Risk Governance Alignment
- Remediation Advisory & Developer Enablement Workshop
Objective:
Enhance the security maturity of software by integrating manual and automated reviews, logic validation, and compliance alignment with global standards.
Value Delivered:
Designed for maturing organizations, this tier combines automation with expert review to strengthen resilience, ensure compliance, and embed security in DevSecOps workflows.
Enterprise Resilience Tier
Target Clients:
Large enterprises, government agencies, financial institutions, and technology service providers managing critical, high-volume, or multi-application environments requiring continuous assurance and governance-level reporting.
Sub-Services in scope:
- Full-Spectrum Secure Code Audit (Automated + Manual)
- Threat Modeling & Architecture Risk Analysis
- Advanced Business Logic & API Security Assessment
- Continuous Secure Code Assurance Integration
- Regulatory & Compliance Assurance Review
- Strategic Secure Development & Governance Program
Objective:
Deliver comprehensive, enterprise-grade code security assurance — integrating advanced threat modeling, continuous code validation, and compliance-driven governance into global development operations.
Value Delivered:
This tier provides holistic, end-to-end code assurance with measurable security metrics, proactive threat modeling, and executive-level visibility for sustained resilience and compliance excellence.
Foundation Tier
Target Clients:
Small enterprises, startups, and early-stage technology firms developing web or mobile applications seeking essential code security hygiene and vulnerability prevention.
Sub-Services in Scope :
- Automated Static Code Analysis (Essential SAST)
- Open-Source Dependency Review (SCA Lite)
- Secrets & Credential Exposure Detection
- OWASP Top 10 Vulnerability Check
- Basic Compliance & Reporting Alignment
- Quick-Fix Recommendations & Developer Briefing
Objective:
Establish baseline application security by identifying coding flaws, insecure dependencies, and common vulnerabilities early in the software development lifecycle (SDLC).
Value Delivered:
Ideal for cost-conscious or emerging organizations, this tier provides affordable, foundational code assurance — improving visibility, developer awareness, and security posture before application deployment.
Enhanced Protection Tier
Target Clients:
Mid-sized enterprises, SaaS providers, and regulated-sector organizations with growing applications and increasing compliance obligations seeking a deeper and continuous code assurance model.
Sub-Services in Scope:
- Comprehensive Static & Manual Code Review (SAST + Expert Validation)
- Software Composition Analysis (SCA Advanced)
- Business Logic & Authentication Review
- Secure Coding Standards Assessment
- Compliance & Risk Governance Alignment
- Remediation Advisory & Developer Enablement Workshop
Objective:
Enhance the security maturity of software by integrating manual and automated reviews, logic validation, and compliance alignment with global standards.
Value Delivered:
Designed for maturing organizations, this tier combines automation with expert review to strengthen resilience, ensure compliance, and embed security in DevSecOps workflows.
Enterprise Resilience Tier
Target Clients:
Large enterprises, government agencies, financial institutions, and technology service providers managing critical, high-volume, or multi-application environments requiring continuous assurance and governance-level reporting.
Sub-Services in scope:
- Full-Spectrum Secure Code Audit (Automated + Manual)
- Threat Modeling & Architecture Risk Analysis
- Advanced Business Logic & API Security Assessment
- Continuous Secure Code Assurance Integration
- Regulatory & Compliance Assurance Review
- Strategic Secure Development & Governance Program
Objective:
Deliver comprehensive, enterprise-grade code security assurance — integrating advanced threat modeling, continuous code validation, and compliance-driven governance into global development operations.
Value Delivered:
This tier provides holistic, end-to-end code assurance with measurable security metrics, proactive threat modeling, and executive-level visibility for sustained resilience and compliance excellence.
CODEC NETWORKS VALUE PROPOSITION
Codec Networks enables secure software delivery by embedding automated code review and
DevSecOps practices, reducing risks without slowing innovation.
Industry Value Propositions / Benefits – Secure Code Review (DevSecOps Integration)
Codec Networks delivers high-impact, enterprise-grade Secure Code Review (DevSecOps Integration) services that align cybersecurity with business agility, compliance, and innovation. The value proposition is built on a risk-driven delivery approach, deep technical expertise, and globally aligned security practices, ensuring organizations can scale securely in complex digital environments.
1. Strategic & Risk-Driven Delivery Approach
- Boardroom-Aligned Security Execution
Services are aligned with enterprise risk appetite, providing leadership with visibility into application security posture and business impact. - Shift-Left & Continuous Security Model
Security is embedded early in development and continuously enforced across CI/CD pipelines, reducing late-stage vulnerabilities and costs. - Outcome-Focused Engagements
Emphasis on measurable outcomes such as reduced vulnerability density, faster remediation, and secure release cycles. - Scalable & Adaptive Delivery Framework
Methodology supports cloud-native, microservices, and hybrid environments, adapting to evolving enterprise architectures. - Integrated DevSecOps Enablement
Seamless integration of security into development workflows ensures minimal disruption to developer productivity and delivery timelines.
2. Advanced Technical Competency
- Comprehensive Application Security Expertise
Strong capabilities across SAST, DAST, SCA, API security, and manual code review ensure deep and broad vulnerability coverage. - Multi-Technology & Platform Proficiency
Expertise across programming languages, frameworks, cloud platforms (AWS, Azure, GCP), and containerized environments. - Secure Architecture & Design Validation
Ability to assess and strengthen application architecture, ensuring security is built into system design, not just code. - Automation-Driven Security Engineering
Advanced integration of automated security tools into CI/CD pipelines for continuous and scalable security validation. - Threat Intelligence & Attack Simulation Integration
Leverages real-world threat intelligence to identify emerging risks and validate application resilience against modern attack vectors.
3. Cyber Security Skills of Professionals
- Highly Skilled Security Engineers & Consultants
Teams possess deep expertise in secure coding, vulnerability analysis, penetration testing, and DevSecOps practices. - Industry-Recognized Certifications & Standards Alignment
Professionals are aligned with global standards such as OWASP, ISO 27001, NIST, and secure development frameworks. - Developer-Centric Security Mindset
Ability to translate complex security findings into actionable, developer-friendly remediation guidance. - Business Logic & Advanced Threat Analysis Skills
Expertise in identifying complex vulnerabilities beyond automated tools, including logic flaws and privilege escalation risks. - Continuous Skill Enhancement & Research-Driven Approach
Teams stay updated with evolving threats, zero-day vulnerabilities, and secure coding advancements.
4. Business & Industry Benefits
- Accelerated Secure Software Delivery
Enables faster releases without compromising security, supporting agile and DevOps-driven organizations. - Reduced Risk Exposure & Breach Probability
Early detection and remediation significantly lower the likelihood of application-layer attacks and data breaches. - Cost Optimization in Security Operations
Identifying vulnerabilities early reduces expensive rework and incident response costs in later stages. - Enhanced Regulatory Compliance & Audit Readiness
Aligns application security practices with global standards, simplifying audits and regulatory adherence. - Improved Customer Trust & Brand Reputation
Secure applications enhance user confidence, protecting brand value in competitive digital markets.
5. Governance, Visibility & Measurable Outcomes
- Real-Time Security Dashboards & Reporting
Provides actionable insights into vulnerabilities, remediation status, and overall security posture. - Data-Driven Decision Making
Metrics and analytics enable leadership to prioritize investments and track security improvements over time. - Continuous Improvement & DevSecOps Maturity Growth
Establishes long-term security culture within development teams through training and feedback loops. - End-to-End Security Lifecycle Coverage
Covers design, development, testing, deployment, and monitoring—ensuring holistic application security.
Conclusion
Codec Networks positions Secure Code Review (DevSecOps Integration) as a strategic enabler of secure digital transformation, not just a technical control. By combining deep technical expertise, structured delivery methodology, and business-aligned risk management, the company empowers enterprises to build, deploy, and scale applications with confidence, compliance, and resilience in an increasingly complex threat landscape
Founded in 2008 with 17+ Years of Industry Experience in Information and Cyber Security domain
Codec Networks Full-Spectrum Cybersecurity Expertise across all Industry Domains:
- Security Vulnerability Assessment & Penetration Testing (VAPT): Covering Web, Mobile, API, IoT, Blockchain, Cloud-Native, and smart infrastructure environments, with a focus on OWASP, MITRE ATT&CK, and real-world exploit simulation.
- Offensive Security & Deep Level Security Assessments: Advanced Red Team, Blue Team and Purple Team Exercises, Threat Simulations, Social Engineering Campaigns, and Secure Code Review.
- IT Security Audit & Compliance Services: Implementation and audit support for ISO/IEC 27001, ISO 27701, NIST CSF, RBI-CSF, SEBI, IRDAI, PCI DSS, HIPAA, SOC 2, GDPR, and India’s DPDPA 2023.
- Data Privacy & Strategic Risk Advisory: ISO 27701, GDPR, DPDPA, Cross-border compliance, DPIA, DPO-as-a-service, supply chain risk management, and digital transformation risk consulting.
- Emerging Technology Security (Web3.0 | AI | Blockchain): Specialized testing for smart contracts, DeFi platforms, Metaverse applications, AI/ML models, quantum readiness, and blockchain nodes.
- Managed SOC & Threat Monitoring Services: End-to-end SOC operations, SIEM/EDR/XDR/SOAR integration, threat intelligence, cloud security monitoring, and 24/7 incident response.
- Cyber Forensics & Threat Analysis: Investigation services including Device forensics, Malware Analysis, Cloud and Mobile forensics, insider threat detection, and Forensic support.
- Board-Level Cybersecurity Advisory Services to build governance, quantify risks, and align with enterprise-wide digital priorities : Codec Networks enables this transformation by offering Integrated Cyber Risk Management, GRC Program Advisory, Reputation Management, Crisis Communication Readiness, and CISO Support, tailored for CXOs and board members seeking to integrate cybersecurity into strategic decision-making.
- Cyber Security Education & Global Certifications - Through the Codec Centre for Professional Excellence, we deliver Post Graduate Certification in Advanced Cybersecurity (PGCAC), Graduate Certification in Advanced Cybersecurity (GCAC), Accredited Trainings & Certifications from EC Council, PECB, TUV, Quality Austria, ISACA and ISC2 - building the next generation of cybersecurity leaders.
- CERT-IN empaneled Information Security Auditing Organization
- NICSI empaneled for providing Application Audit and Compliance Services under Start-Up Category


- An ISO/IEC 27001:2022 certified company, has established Information Security Management System (ISMS), demonstrating a structured approach to manage and protect sensitive information from cyber threats.
- An ISO 9001 certified company, has established and maintains a certified Quality Management System (QMS) that meets international standards for quality and consistency
At Codec Networks, our foundation is built on deep technical mastery, certified expertise, and an unrelenting pursuit of cyber excellence. With a team of globally accredited professionals, advanced methodologies, and next-generation tools, we deliver measurable security outcomes across assessment, compliance, monitoring, and forensic domains.
Our competency-driven approach ensures every engagement is governed by precision, accountability, and alignment with international standards — empowering enterprises to stay secure, compliant, and resilient.
Governance, Risk & Compliance (GRC) Competency
Codec Networks’ dedicated Governance, Risk & Compliance (GRC) group specializes in security assessments, risk management, regulatory compliance, and audit readiness. The team partners with organizations to strengthen governance frameworks and ensure end-to-end compliance in a complex regulatory landscape.
Key Attributes:
- Team of certified auditors and consultants with credentials including ISO 27001 LA/LI, ISO 31000 Risk Specialist, ISO 27701 PIMS, GDPR, SOC 2, HIPAA, CCPA, DPO, CISA, CISM, CRISC, CISSP and other advanced industry certifications.
- Expertise in enterprise risk quantification, privacy impact assessment (PIA/DPIA), audit automation, and supply chain risk mapping.
- Proven track record in implementing ISO-based ISMS/PIMS frameworks, RBI/SEBI/IRDAI audits, and cross-border data compliance projects.
Vulnerability Assessment & Penetration Testing (VAPT) Expertise
Our VAPT teams bring extensive technical depth across Web, Mobile, API, Cloud, Network, Database, Infrastructure, IoT, and People & Process domains.
Every engagement is mapped to OWASP, NIST, MITRE ATT&CK, ISO 27001, PCI DSS, HIPAA, RBI, and GDPR frameworks — ensuring real-world relevance and compliance alignment.
Core Strengths:
- Certified professionals with CEH, C-PENT, LPT, OSCP, OSWE, OSEE, and CREST credentials, averaging 7–10 years of offensive security experience.
- Proven expertise in Red/Blue/Purple Teaming, DevSecOps, secure SDLC, and threat emulation.
- Continuous skill enhancement through CTFs, hackathons, and product certifications (on case to case basis) such as CCNA, CCNP, Juniper, Fortinet, McAfee, RSA etc
Managed SOC & Threat Intelligence Operations
Codec Networks operates a 24/7 Managed Security Operations Center (SOC) delivering continuous visibility, detection, and response across hybrid environments.
Our SOC integrates SIEM, SOAR, EDR/XDR, and Cloud-Native Analytics to ensure rapid threat detection, incident containment, and business continuity.
Key Capabilities:
- Certified SOC analysts with credentials such as CHFI, CEH, CompTIA CySA+, GCIA, GCFA, and Splunk Certified Architect.
- Integration with platforms like Splunk, QRadar, SentinelOne, CrowdStrike, Elastic, Microsoft Sentinel, and Cortex XSOAR.
- Advanced use cases include cloud posture management, insider threat analytics, MITRE ATT&CK–aligned detections, and threat hunting automation.
- Comprehensive SOC Maturity Assessments and Threat Intelligence Fusion through integration with global feeds and dark web monitoring.
Cyber Forensics & Threat Analysis Expertise
Our Cyber Forensic Division delivers end-to-end investigation, evidence preservation, and digital analysis services — designed to support law enforcement, corporate forensics, and internal response teams.
We combine forensic science with cyber intelligence to identify root causes, trace adversaries, and restore operational integrity.
Core Expertise Areas:
- Device, Network, Cloud, and Mobile Forensics – leveraging latest forensic tools (wherever applicable) such as Autopsy, Cyber Triage, Kape, EnCase, FTK, Magnet AXIOM, and Cellebrite.
- Malware Reverse Engineering and Memory Forensics for incident containment and threat attribution.
- Blockchain & Crypto Forensics – tracing DeFi fraud, NFT manipulation, and crypto laundering activities using Chainalysis, TRM Labs, and Elliptic (wherever applicable).
- Incident Response Support – forensic readiness, eDiscovery, evidence preservation, aligned with ISO/IEC 27037 & 27043.
- Certified experts including CHFI, eCIR, eCDFP, GCFE, GCFA, EnCE, CFCE and ECIH, ensuring investigations meet both technical and legal standards.
Advanced Tools, Frameworks & Continuous Innovation
Codec Networks leverages industry-leading tools and platforms such as Burp Suite Pro, Nessus, Prisma Cloud, Splunk, QRadar, CrowdStrike, SentinelOne, Autopsy, Chainalysis, MythX, and Prowler, (wherever applicable) ensuring accuracy, scalability, and efficiency.
Our methodologies align with globally recognized frameworks including:
- MITRE ATT&CK & D3FEND
- OWASP Top 10 / MASVS / ASVS
- NIST Cybersecurity Framework & SP 800-115
- ISO/IEC 27001, 27701, 31000, 22301
Through ongoing research, Codec Networks continually evolves to address modern threats — from Generative AI prompt attacks and smart contract exploits to IoT zero-days, metaverse impersonation, and quantum-era vulnerabilities.
Compliance-Driven Deliverables
All technical engagements and reports are mapped to major global and Indian compliance frameworks — including ISO 27001, PCI DSS, HIPAA, GDPR, RBI-CSF, SEBI, IRDAI, and DPDPA 2023.
Our structured technical and executive reports support board-level visibility, audit evidence, and certification readiness, ensuring that every engagement drives both technical assurance and regulatory confidence.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
At Codec Networks, we believe that cybersecurity excellence is not achieved through tools alone — it is built through methodical delivery, risk-based insight, and measurable outcomes.
Our Agile and Modular 8-Stage Delivery Methodology ensures that every engagement — from rapid risk assessments to full-scale ISMS implementations - is structured, standards-aligned, and business-focused.
Agile & Modular Methodology
Our delivery framework integrates global best practices with localized regulatory insight, ensuring each engagement is executed with clarity, accountability, and precision. Clients benefit from seamless onboarding, milestone-driven execution, and transparent reporting throughout the lifecycle.
- Discovery & Scoping: Collaborative workshops to understand business context, IT landscape, compliance obligations, and risk appetite, forming the foundation of a well-defined project scope.
- Risk Profiling & Gap Assessment: Comprehensive evaluation of people, process, and technology controls aligned with ISO 27001, NIST CSF, GDPR, HIPAA, DPDPA 2023, RBI, and PCI DSS.
- Regulatory Mapping & Framework Alignment: Mapping organizational obligations against applicable standards and laws — from ISO & NIST to RBI, SEBI, IRDAI, UIDAI, and DPDPA — including new-age frameworks like ISO 42001 (AI) and FATF for emerging technologies.
- Security Architecture & Control Design: Designing or refining network, cloud, and data security architectures with controls tailored for cloud, AI, OT/ICS, and Web3.0 environments.
- Documentation & Policy Development: Creation and refinement of Policies, SOPs, Risk Registers, DPIAs, Incident Response Plans, and Governance Documents, ensuring audit readiness and legal compliance.
- Implementation & Risk Treatment: Execution of remediation roadmaps, vendor risk management, privacy engineering, and workforce training to mitigate gaps and operationalize security controls.
- Validation, Testing & Audit Readiness: Conducting mock audits, VAPT, forensic readiness, and compliance testing to validate effectiveness and prepare for certifications.
- Governance Reporting & Continual Improvement: Delivering executive dashboards, compliance scorecards, and board-level insights with ongoing advisory through vCISO and DPO-as-a-Service models.
Risk-Based & Business-Oriented Audit Approach
Our methodology goes beyond testing systems — it focuses on how vulnerabilities translate into business, reputational, and compliance risks.
- Deliver Deep Insight: Actionable intelligence into vulnerabilities, attack paths, business impact, and remediation priorities.
- Extend Beyond Tools: Manual and contextual assessments combining automation with human expertise across government, financial, and commercial sectors.
- Actionable Reporting: Executive-friendly reports that translate complex findings into strategic, risk-aware recommendations.
- Efficient Execution: Critical assets prioritized for testing to deliver maximum value within tight engagement windows.
Outcome-Driven Engagements for Security Maturity
Each stage is modular yet interconnected, adaptable to enterprises of any scale or industry. Whether it’s a cloud-native fintech pursuing SOC 2, a healthcare provider ensuring HIPAA alignment, or a bank meeting RBI-CSF requirements, Codec Networks ensures consistency, compliance, and measurable improvement.
Beyond certification checklists, our Post-Audit Support and Continuous Risk Monitoring provide remediation guidance, breach response playbooks, staff training, and ongoing compliance tracking — building sustainable security posture and resilient business continuity.
Codec Networks – Turning Compliance into a Competitive Advantage.
Structured. Measurable. Secure. Always Aligned with Your Business Goals.
At Codec Networks, our clients are not just audit subjects—they are long-term partners in a shared cybersecurity journey. Every engagement is designed around the client’s business priorities, security maturity, and risk appetite, ensuring solutions that are relevant, practical, and results-driven.
With a legacy of 650+ successful engagements across industries such as Banking, Fintech, Healthcare, Telecom, Energy, Aviation, Manufacturing, E-commerce, and Government, Codec Networks has attempted to become a trusted advisor for organizations seeking to transform compliance into resilience.
Our engagement philosophy extends beyond conventional audits. We integrate strategic advisory, technical assurance, remediation support, and continuous compliance monitoring, creating a full lifecycle relationship rather than a one-time service. Clients benefit from:
- Personalized advisory frameworks tailored to their business model and operational scale.
- Collaborative engagement models featuring joint workshops, stakeholder training, and compliance awareness sessions.
- Board-level guidance and reporting that translates complex technical findings into actionable business intelligence.
- Transparent communication channels with dedicated project managers, secure digital workspaces, and real-time status dashboards.
By combining the objectivity of an auditor with the empathy of an advisor, Codec Networks builds trust, accountability, and measurable security growth. Our commitment is simple — to deliver cybersecurity as a continuous partnership, not a periodic project.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
At Codec Networks, integrity, professionalism, and ethical responsibility form the cornerstone of every engagement. As a trusted strategic partner in cybersecurity, we operate within the highest standards of ethical conduct, legal compliance, and regulatory governance, ensuring our services strengthen both our clients’ defenses and their reputations.
We adhere to a strict ethical code of conduct, driven by transparency, independence, and accountability. Every consultant, auditor, and engineer within Codec Networks upholds the core security triad of Confidentiality, Integrity, and Availability (CIA) — ensuring data protection, operational reliability, and business continuity at all times.
Our professional ethos blends technical excellence with moral responsibility, following structured processes, defined service standards, and adherence to international and national regulatory frameworks.
Our Ethical & Professional Commitments
- Zero-Compromise Consulting: We maintain independence, neutrality, and confidentiality across all audits and advisory engagements.
- Legal & Regulatory Conformance: We assist clients to conform strictly within the boundaries of applicable cyber laws, privacy regulations, and data protection statutes.
- Client-First Philosophy: Every recommendation is designed to safeguard stakeholder interests, minimize legal exposure, and build sustainable resilience.
- Outcome-Driven Security Maturity: Our modular yet integrated delivery approach supports organizations of all sizes in achieving measurable improvements in security posture.
- Global Delivery, Local Integrity: Our Global Network Delivery Model integrates international best practices with local regulatory expertise — ensuring value-driven, compliant outcomes.
Industry-Specific Security Advisory
Recognizing that every sector faces distinct threats and compliance challenges, Codec Networks provides customized, industry-aligned security advisory across BFSI, Fintech, Telecom, Healthcare, Energy, Aviation, E-commerce, Government, and Critical Infrastructure domains.
Our sector-specific consulting translates regulatory complexity into practical, business-aware strategies, ensuring risk mitigation plans are compliant, auditable, and operationally feasible.
Our Commitment
With a zero-tolerance approach to ethical compromise, Codec Networks stands for trust, transparency, and truth in cybersecurity. We are more than consultants — we are custodians of digital integrity, committed to helping organizations navigate risk, maintain compliance, and enable secure business growth.
Codec Networks – Where Integrity Meets Innovation. Trusted. Ethical. Future-Ready.
At Codec Networks, we combine the strength of a global delivery ecosystem with the precision of local regulatory insight to deliver cybersecurity solutions that are both internationally benchmarked and regionally compliant.
Our Global Delivery Capability enables clients across continents to access specialized cybersecurity expertise, advanced technologies, and globally aligned methodologies. Through a distributed network of certified professionals, partner alliances, and intelligence centers, Codec Networks ensures consistent service quality and rapid response across time zones and geographies.
What truly differentiates us is our Local Expertise—a deep understanding of national regulations, industry frameworks, and operational nuances that shape cybersecurity implementation in each region.
Our hybrid delivery model blends remote and on-site collaboration, combining the agility of digital operations with the contextual understanding of local consultants. This ensures culturally aligned communication, faster problem resolution, and seamless coordination with client teams.
With a presence across India, Codec Networks empowers global enterprises to manage cybersecurity uniformly while adapting to local risks, regulations, and realities.
Codec Networks – Global Vision. Local Precision. Consistent Cyber Resilience.
“With Codec Networks, you’re not just buying a service — you’re investing in a cybersecurity ally who understands your business, defends your reputation, and strengthens your future.”
At Codec Networks, we believe cybersecurity is not a project — it’s a partnership.
Our approach is built on trust, transparency, and transformation, helping clients evolve from compliance readiness to cyber resilience.
Your Strategic Security Partner
Codec Networks acts as a strategic security partner, providing continuous roadmap development, architecture reviews, and improvement programs that evolve with your business and the threat landscape.
“We don’t just secure businesses — we empower them to lead with confidence in a digital-first world.”
Our strength lies in the fusion of technical depth, regulatory insight, industry specialization, and future readiness — providing unmatched cybersecurity value to enterprises across India and beyond.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Every engagement reflects our belief that advisory must meet assurance — a promise we deliver through partnership, integrity, and measurable impact.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
And above all —
“Decoding Threats. Coding Solutions.”
That’s the Codec Networks Advantage.
Industry Value Propositions / Benefits – Secure Code Review (DevSecOps Integration)
Codec Networks delivers high-impact, enterprise-grade Secure Code Review (DevSecOps Integration) services that align cybersecurity with business agility, compliance, and innovation. The value proposition is built on a risk-driven delivery approach, deep technical expertise, and globally aligned security practices, ensuring organizations can scale securely in complex digital environments.
1. Strategic & Risk-Driven Delivery Approach
- Boardroom-Aligned Security Execution
Services are aligned with enterprise risk appetite, providing leadership with visibility into application security posture and business impact. - Shift-Left & Continuous Security Model
Security is embedded early in development and continuously enforced across CI/CD pipelines, reducing late-stage vulnerabilities and costs. - Outcome-Focused Engagements
Emphasis on measurable outcomes such as reduced vulnerability density, faster remediation, and secure release cycles. - Scalable & Adaptive Delivery Framework
Methodology supports cloud-native, microservices, and hybrid environments, adapting to evolving enterprise architectures. - Integrated DevSecOps Enablement
Seamless integration of security into development workflows ensures minimal disruption to developer productivity and delivery timelines.
2. Advanced Technical Competency
- Comprehensive Application Security Expertise
Strong capabilities across SAST, DAST, SCA, API security, and manual code review ensure deep and broad vulnerability coverage. - Multi-Technology & Platform Proficiency
Expertise across programming languages, frameworks, cloud platforms (AWS, Azure, GCP), and containerized environments. - Secure Architecture & Design Validation
Ability to assess and strengthen application architecture, ensuring security is built into system design, not just code. - Automation-Driven Security Engineering
Advanced integration of automated security tools into CI/CD pipelines for continuous and scalable security validation. - Threat Intelligence & Attack Simulation Integration
Leverages real-world threat intelligence to identify emerging risks and validate application resilience against modern attack vectors.
3. Cyber Security Skills of Professionals
- Highly Skilled Security Engineers & Consultants
Teams possess deep expertise in secure coding, vulnerability analysis, penetration testing, and DevSecOps practices. - Industry-Recognized Certifications & Standards Alignment
Professionals are aligned with global standards such as OWASP, ISO 27001, NIST, and secure development frameworks. - Developer-Centric Security Mindset
Ability to translate complex security findings into actionable, developer-friendly remediation guidance. - Business Logic & Advanced Threat Analysis Skills
Expertise in identifying complex vulnerabilities beyond automated tools, including logic flaws and privilege escalation risks. - Continuous Skill Enhancement & Research-Driven Approach
Teams stay updated with evolving threats, zero-day vulnerabilities, and secure coding advancements.
4. Business & Industry Benefits
- Accelerated Secure Software Delivery
Enables faster releases without compromising security, supporting agile and DevOps-driven organizations. - Reduced Risk Exposure & Breach Probability
Early detection and remediation significantly lower the likelihood of application-layer attacks and data breaches. - Cost Optimization in Security Operations
Identifying vulnerabilities early reduces expensive rework and incident response costs in later stages. - Enhanced Regulatory Compliance & Audit Readiness
Aligns application security practices with global standards, simplifying audits and regulatory adherence. - Improved Customer Trust & Brand Reputation
Secure applications enhance user confidence, protecting brand value in competitive digital markets.
5. Governance, Visibility & Measurable Outcomes
- Real-Time Security Dashboards & Reporting
Provides actionable insights into vulnerabilities, remediation status, and overall security posture. - Data-Driven Decision Making
Metrics and analytics enable leadership to prioritize investments and track security improvements over time. - Continuous Improvement & DevSecOps Maturity Growth
Establishes long-term security culture within development teams through training and feedback loops. - End-to-End Security Lifecycle Coverage
Covers design, development, testing, deployment, and monitoring—ensuring holistic application security.
Conclusion
Codec Networks positions Secure Code Review (DevSecOps Integration) as a strategic enabler of secure digital transformation, not just a technical control. By combining deep technical expertise, structured delivery methodology, and business-aligned risk management, the company empowers enterprises to build, deploy, and scale applications with confidence, compliance, and resilience in an increasingly complex threat landscape
Founded in 2008 with 17+ Years of Industry Experience in Information and Cyber Security domain
Codec Networks Full-Spectrum Cybersecurity Expertise across all Industry Domains:
- Security Vulnerability Assessment & Penetration Testing (VAPT): Covering Web, Mobile, API, IoT, Blockchain, Cloud-Native, and smart infrastructure environments, with a focus on OWASP, MITRE ATT&CK, and real-world exploit simulation.
- Offensive Security & Deep Level Security Assessments: Advanced Red Team, Blue Team and Purple Team Exercises, Threat Simulations, Social Engineering Campaigns, and Secure Code Review.
- IT Security Audit & Compliance Services: Implementation and audit support for ISO/IEC 27001, ISO 27701, NIST CSF, RBI-CSF, SEBI, IRDAI, PCI DSS, HIPAA, SOC 2, GDPR, and India’s DPDPA 2023.
- Data Privacy & Strategic Risk Advisory: ISO 27701, GDPR, DPDPA, Cross-border compliance, DPIA, DPO-as-a-service, supply chain risk management, and digital transformation risk consulting.
- Emerging Technology Security (Web3.0 | AI | Blockchain): Specialized testing for smart contracts, DeFi platforms, Metaverse applications, AI/ML models, quantum readiness, and blockchain nodes.
- Managed SOC & Threat Monitoring Services: End-to-end SOC operations, SIEM/EDR/XDR/SOAR integration, threat intelligence, cloud security monitoring, and 24/7 incident response.
- Cyber Forensics & Threat Analysis: Investigation services including Device forensics, Malware Analysis, Cloud and Mobile forensics, insider threat detection, and Forensic support.
- Board-Level Cybersecurity Advisory Services to build governance, quantify risks, and align with enterprise-wide digital priorities : Codec Networks enables this transformation by offering Integrated Cyber Risk Management, GRC Program Advisory, Reputation Management, Crisis Communication Readiness, and CISO Support, tailored for CXOs and board members seeking to integrate cybersecurity into strategic decision-making.
- Cyber Security Education & Global Certifications - Through the Codec Centre for Professional Excellence, we deliver Post Graduate Certification in Advanced Cybersecurity (PGCAC), Graduate Certification in Advanced Cybersecurity (GCAC), Accredited Trainings & Certifications from EC Council, PECB, TUV, Quality Austria, ISACA and ISC2 - building the next generation of cybersecurity leaders.
- CERT-IN empaneled Information Security Auditing Organization
- NICSI empaneled for providing Application Audit and Compliance Services under Start-Up Category
- An ISO/IEC 27001:2022 certified company, has established Information Security Management System (ISMS), demonstrating a structured approach to manage and protect sensitive information from cyber threats.
- An ISO 9001 certified company, has established and maintains a certified Quality Management System (QMS) that meets international standards for quality and consistency
At Codec Networks, our foundation is built on deep technical mastery, certified expertise, and an unrelenting pursuit of cyber excellence. With a team of globally accredited professionals, advanced methodologies, and next-generation tools, we deliver measurable security outcomes across assessment, compliance, monitoring, and forensic domains.
Our competency-driven approach ensures every engagement is governed by precision, accountability, and alignment with international standards — empowering enterprises to stay secure, compliant, and resilient.
Governance, Risk & Compliance (GRC) Competency
Codec Networks’ dedicated Governance, Risk & Compliance (GRC) group specializes in security assessments, risk management, regulatory compliance, and audit readiness. The team partners with organizations to strengthen governance frameworks and ensure end-to-end compliance in a complex regulatory landscape.
Key Attributes:
- Team of certified auditors and consultants with credentials including ISO 27001 LA/LI, ISO 31000 Risk Specialist, ISO 27701 PIMS, GDPR, SOC 2, HIPAA, CCPA, DPO, CISA, CISM, CRISC, CISSP and other advanced industry certifications.
- Expertise in enterprise risk quantification, privacy impact assessment (PIA/DPIA), audit automation, and supply chain risk mapping.
- Proven track record in implementing ISO-based ISMS/PIMS frameworks, RBI/SEBI/IRDAI audits, and cross-border data compliance projects.
Vulnerability Assessment & Penetration Testing (VAPT) Expertise
Our VAPT teams bring extensive technical depth across Web, Mobile, API, Cloud, Network, Database, Infrastructure, IoT, and People & Process domains.
Every engagement is mapped to OWASP, NIST, MITRE ATT&CK, ISO 27001, PCI DSS, HIPAA, RBI, and GDPR frameworks — ensuring real-world relevance and compliance alignment.
Core Strengths:
- Certified professionals with CEH, C-PENT, LPT, OSCP, OSWE, OSEE, and CREST credentials, averaging 7–10 years of offensive security experience.
- Proven expertise in Red/Blue/Purple Teaming, DevSecOps, secure SDLC, and threat emulation.
- Continuous skill enhancement through CTFs, hackathons, and product certifications (on case to case basis) such as CCNA, CCNP, Juniper, Fortinet, McAfee, RSA etc
Managed SOC & Threat Intelligence Operations
Codec Networks operates a 24/7 Managed Security Operations Center (SOC) delivering continuous visibility, detection, and response across hybrid environments.
Our SOC integrates SIEM, SOAR, EDR/XDR, and Cloud-Native Analytics to ensure rapid threat detection, incident containment, and business continuity.
Key Capabilities:
- Certified SOC analysts with credentials such as CHFI, CEH, CompTIA CySA+, GCIA, GCFA, and Splunk Certified Architect.
- Integration with platforms like Splunk, QRadar, SentinelOne, CrowdStrike, Elastic, Microsoft Sentinel, and Cortex XSOAR.
- Advanced use cases include cloud posture management, insider threat analytics, MITRE ATT&CK–aligned detections, and threat hunting automation.
- Comprehensive SOC Maturity Assessments and Threat Intelligence Fusion through integration with global feeds and dark web monitoring.
Cyber Forensics & Threat Analysis Expertise
Our Cyber Forensic Division delivers end-to-end investigation, evidence preservation, and digital analysis services — designed to support law enforcement, corporate forensics, and internal response teams.
We combine forensic science with cyber intelligence to identify root causes, trace adversaries, and restore operational integrity.
Core Expertise Areas:
- Device, Network, Cloud, and Mobile Forensics – leveraging latest forensic tools (wherever applicable) such as Autopsy, Cyber Triage, Kape, EnCase, FTK, Magnet AXIOM, and Cellebrite.
- Malware Reverse Engineering and Memory Forensics for incident containment and threat attribution.
- Blockchain & Crypto Forensics – tracing DeFi fraud, NFT manipulation, and crypto laundering activities using Chainalysis, TRM Labs, and Elliptic (wherever applicable).
- Incident Response Support – forensic readiness, eDiscovery, evidence preservation, aligned with ISO/IEC 27037 & 27043.
- Certified experts including CHFI, eCIR, eCDFP, GCFE, GCFA, EnCE, CFCE and ECIH, ensuring investigations meet both technical and legal standards.
Advanced Tools, Frameworks & Continuous Innovation
Codec Networks leverages industry-leading tools and platforms such as Burp Suite Pro, Nessus, Prisma Cloud, Splunk, QRadar, CrowdStrike, SentinelOne, Autopsy, Chainalysis, MythX, and Prowler, (wherever applicable) ensuring accuracy, scalability, and efficiency.
Our methodologies align with globally recognized frameworks including:
- MITRE ATT&CK & D3FEND
- OWASP Top 10 / MASVS / ASVS
- NIST Cybersecurity Framework & SP 800-115
- ISO/IEC 27001, 27701, 31000, 22301
Through ongoing research, Codec Networks continually evolves to address modern threats — from Generative AI prompt attacks and smart contract exploits to IoT zero-days, metaverse impersonation, and quantum-era vulnerabilities.
Compliance-Driven Deliverables
All technical engagements and reports are mapped to major global and Indian compliance frameworks — including ISO 27001, PCI DSS, HIPAA, GDPR, RBI-CSF, SEBI, IRDAI, and DPDPA 2023.
Our structured technical and executive reports support board-level visibility, audit evidence, and certification readiness, ensuring that every engagement drives both technical assurance and regulatory confidence.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
At Codec Networks, we believe that cybersecurity excellence is not achieved through tools alone — it is built through methodical delivery, risk-based insight, and measurable outcomes.
Our Agile and Modular 8-Stage Delivery Methodology ensures that every engagement — from rapid risk assessments to full-scale ISMS implementations - is structured, standards-aligned, and business-focused.
Agile & Modular Methodology
Our delivery framework integrates global best practices with localized regulatory insight, ensuring each engagement is executed with clarity, accountability, and precision. Clients benefit from seamless onboarding, milestone-driven execution, and transparent reporting throughout the lifecycle.
- Discovery & Scoping: Collaborative workshops to understand business context, IT landscape, compliance obligations, and risk appetite, forming the foundation of a well-defined project scope.
- Risk Profiling & Gap Assessment: Comprehensive evaluation of people, process, and technology controls aligned with ISO 27001, NIST CSF, GDPR, HIPAA, DPDPA 2023, RBI, and PCI DSS.
- Regulatory Mapping & Framework Alignment: Mapping organizational obligations against applicable standards and laws — from ISO & NIST to RBI, SEBI, IRDAI, UIDAI, and DPDPA — including new-age frameworks like ISO 42001 (AI) and FATF for emerging technologies.
- Security Architecture & Control Design: Designing or refining network, cloud, and data security architectures with controls tailored for cloud, AI, OT/ICS, and Web3.0 environments.
- Documentation & Policy Development: Creation and refinement of Policies, SOPs, Risk Registers, DPIAs, Incident Response Plans, and Governance Documents, ensuring audit readiness and legal compliance.
- Implementation & Risk Treatment: Execution of remediation roadmaps, vendor risk management, privacy engineering, and workforce training to mitigate gaps and operationalize security controls.
- Validation, Testing & Audit Readiness: Conducting mock audits, VAPT, forensic readiness, and compliance testing to validate effectiveness and prepare for certifications.
- Governance Reporting & Continual Improvement: Delivering executive dashboards, compliance scorecards, and board-level insights with ongoing advisory through vCISO and DPO-as-a-Service models.
Risk-Based & Business-Oriented Audit Approach
Our methodology goes beyond testing systems — it focuses on how vulnerabilities translate into business, reputational, and compliance risks.
- Deliver Deep Insight: Actionable intelligence into vulnerabilities, attack paths, business impact, and remediation priorities.
- Extend Beyond Tools: Manual and contextual assessments combining automation with human expertise across government, financial, and commercial sectors.
- Actionable Reporting: Executive-friendly reports that translate complex findings into strategic, risk-aware recommendations.
- Efficient Execution: Critical assets prioritized for testing to deliver maximum value within tight engagement windows.
Outcome-Driven Engagements for Security Maturity
Each stage is modular yet interconnected, adaptable to enterprises of any scale or industry. Whether it’s a cloud-native fintech pursuing SOC 2, a healthcare provider ensuring HIPAA alignment, or a bank meeting RBI-CSF requirements, Codec Networks ensures consistency, compliance, and measurable improvement.
Beyond certification checklists, our Post-Audit Support and Continuous Risk Monitoring provide remediation guidance, breach response playbooks, staff training, and ongoing compliance tracking — building sustainable security posture and resilient business continuity.
Codec Networks – Turning Compliance into a Competitive Advantage.
Structured. Measurable. Secure. Always Aligned with Your Business Goals.
At Codec Networks, our clients are not just audit subjects—they are long-term partners in a shared cybersecurity journey. Every engagement is designed around the client’s business priorities, security maturity, and risk appetite, ensuring solutions that are relevant, practical, and results-driven.
With a legacy of 650+ successful engagements across industries such as Banking, Fintech, Healthcare, Telecom, Energy, Aviation, Manufacturing, E-commerce, and Government, Codec Networks has attempted to become a trusted advisor for organizations seeking to transform compliance into resilience.
Our engagement philosophy extends beyond conventional audits. We integrate strategic advisory, technical assurance, remediation support, and continuous compliance monitoring, creating a full lifecycle relationship rather than a one-time service. Clients benefit from:
- Personalized advisory frameworks tailored to their business model and operational scale.
- Collaborative engagement models featuring joint workshops, stakeholder training, and compliance awareness sessions.
- Board-level guidance and reporting that translates complex technical findings into actionable business intelligence.
- Transparent communication channels with dedicated project managers, secure digital workspaces, and real-time status dashboards.
By combining the objectivity of an auditor with the empathy of an advisor, Codec Networks builds trust, accountability, and measurable security growth. Our commitment is simple — to deliver cybersecurity as a continuous partnership, not a periodic project.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
At Codec Networks, integrity, professionalism, and ethical responsibility form the cornerstone of every engagement. As a trusted strategic partner in cybersecurity, we operate within the highest standards of ethical conduct, legal compliance, and regulatory governance, ensuring our services strengthen both our clients’ defenses and their reputations.
We adhere to a strict ethical code of conduct, driven by transparency, independence, and accountability. Every consultant, auditor, and engineer within Codec Networks upholds the core security triad of Confidentiality, Integrity, and Availability (CIA) — ensuring data protection, operational reliability, and business continuity at all times.
Our professional ethos blends technical excellence with moral responsibility, following structured processes, defined service standards, and adherence to international and national regulatory frameworks.
Our Ethical & Professional Commitments
- Zero-Compromise Consulting: We maintain independence, neutrality, and confidentiality across all audits and advisory engagements.
- Legal & Regulatory Conformance: We assist clients to conform strictly within the boundaries of applicable cyber laws, privacy regulations, and data protection statutes.
- Client-First Philosophy: Every recommendation is designed to safeguard stakeholder interests, minimize legal exposure, and build sustainable resilience.
- Outcome-Driven Security Maturity: Our modular yet integrated delivery approach supports organizations of all sizes in achieving measurable improvements in security posture.
- Global Delivery, Local Integrity: Our Global Network Delivery Model integrates international best practices with local regulatory expertise — ensuring value-driven, compliant outcomes.
Industry-Specific Security Advisory
Recognizing that every sector faces distinct threats and compliance challenges, Codec Networks provides customized, industry-aligned security advisory across BFSI, Fintech, Telecom, Healthcare, Energy, Aviation, E-commerce, Government, and Critical Infrastructure domains.
Our sector-specific consulting translates regulatory complexity into practical, business-aware strategies, ensuring risk mitigation plans are compliant, auditable, and operationally feasible.
Our Commitment
With a zero-tolerance approach to ethical compromise, Codec Networks stands for trust, transparency, and truth in cybersecurity. We are more than consultants — we are custodians of digital integrity, committed to helping organizations navigate risk, maintain compliance, and enable secure business growth.
Codec Networks – Where Integrity Meets Innovation. Trusted. Ethical. Future-Ready.
At Codec Networks, we combine the strength of a global delivery ecosystem with the precision of local regulatory insight to deliver cybersecurity solutions that are both internationally benchmarked and regionally compliant.
Our Global Delivery Capability enables clients across continents to access specialized cybersecurity expertise, advanced technologies, and globally aligned methodologies. Through a distributed network of certified professionals, partner alliances, and intelligence centers, Codec Networks ensures consistent service quality and rapid response across time zones and geographies.
What truly differentiates us is our Local Expertise—a deep understanding of national regulations, industry frameworks, and operational nuances that shape cybersecurity implementation in each region.
Our hybrid delivery model blends remote and on-site collaboration, combining the agility of digital operations with the contextual understanding of local consultants. This ensures culturally aligned communication, faster problem resolution, and seamless coordination with client teams.
With a presence across India, Codec Networks empowers global enterprises to manage cybersecurity uniformly while adapting to local risks, regulations, and realities.
Codec Networks – Global Vision. Local Precision. Consistent Cyber Resilience.
“With Codec Networks, you’re not just buying a service — you’re investing in a cybersecurity ally who understands your business, defends your reputation, and strengthens your future.”
At Codec Networks, we believe cybersecurity is not a project — it’s a partnership.
Our approach is built on trust, transparency, and transformation, helping clients evolve from compliance readiness to cyber resilience.
Your Strategic Security Partner
Codec Networks acts as a strategic security partner, providing continuous roadmap development, architecture reviews, and improvement programs that evolve with your business and the threat landscape.
“We don’t just secure businesses — we empower them to lead with confidence in a digital-first world.”
Our strength lies in the fusion of technical depth, regulatory insight, industry specialization, and future readiness — providing unmatched cybersecurity value to enterprises across India and beyond.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Every engagement reflects our belief that advisory must meet assurance — a promise we deliver through partnership, integrity, and measurable impact.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
And above all —
“Decoding Threats. Coding Solutions.”
That’s the Codec Networks Advantage.
WHAT OUR CUSTOMERS SAY
Codec Networks DevSecOps-driven secure code review significantly reduces vulnerabilities, improving our overall security
posture and accelerating product delivery timelines.
-
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Vijay
Developer -
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Deepak
Developer -

“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Sanjay
Security Analysts
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Vijay
Developer
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Deepak
Developer
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Sanjay
Security AnalystsINDUSTRY & SECURITY THREAT LANDSCAPE
Rapid DevOps adoption increases risk of insecure code deployment, making integrated
secure code review essential for modern application security.
Industry dynamics / trends / challenges / threats
- Always-on digital banking and core uptime. Core banking, RTGS/NEFT, payments, and treasury platforms demand near-zero downtime. Even small code regressions can trigger settlement failures and regulatory scrutiny, magnifying business impact.
- Rapid product innovation and Open Banking. APIs, UPI rails, and fintech partnerships accelerate feature velocity but widen trust boundaries. Poor token handling or weak API input validation becomes a high-value fraud vector.
- High-end adversaries and fraud ecosystems. Credential stuffing, BEC, mule networks, and targeted spear-phishing seek footholds through app flaws. Attack chains often start with logic bugs and escalate to funds diversion.
- Legacy–cloud coexistence. Mainframes, ESBs, microservices, and SaaS blend into complex estates. Inconsistent secure coding norms across stacks create subtle authorization and data-leak issues.
How Secure code reviews help
- Regulatory-grade code assurance. Reviews map findings to PCI DSS, SWIFT, and internal ISMS controls with audit-ready evidence, strengthening exam readiness and compliance narratives.
- API and payments security hardening. Deep checks for idempotency, race conditions, JWT/OAuth misuse, and strong input validation reduce fraud vectors on high-value payment paths.
- Threat-modeled design reviews. Banking use-case threat models (authorization, ledger integrity, non-repudiation) expose logic abuse early, lowering defect escape into production.
- Pipeline gates and segregation of duties. CI/CD security gates enforce four-eyes principles for risky changes; SAST/SCA/DAST automation prevents insecure builds from shipping.
- Secure secrets and crypto hygiene. Eliminates hardcoded keys, enforces HSM/KMS usage, and standardizes cryptographic configurations, reducing lateral movement and data exposure.
INDUSTRY & SECURITY THREAT LANDSCAPE
Rapid DevOps adoption increases risk of insecure code deployment, making integrated
secure code review essential for modern application security.
Industry Landscape
Industry dynamics / trends / challenges / threats
- Always-on digital banking and core uptime. Core banking, RTGS/NEFT, payments, and treasury platforms demand near-zero downtime. Even small code regressions can trigger settlement failures and regulatory scrutiny, magnifying business impact.
- Rapid product innovation and Open Banking. APIs, UPI rails, and fintech partnerships accelerate feature velocity but widen trust boundaries. Poor token handling or weak API input validation becomes a high-value fraud vector.
- High-end adversaries and fraud ecosystems. Credential stuffing, BEC, mule networks, and targeted spear-phishing seek footholds through app flaws. Attack chains often start with logic bugs and escalate to funds diversion.
- Legacy–cloud coexistence. Mainframes, ESBs, microservices, and SaaS blend into complex estates. Inconsistent secure coding norms across stacks create subtle authorization and data-leak issues.
How Secure code reviews help
- Regulatory-grade code assurance. Reviews map findings to PCI DSS, SWIFT, and internal ISMS controls with audit-ready evidence, strengthening exam readiness and compliance narratives.
- API and payments security hardening. Deep checks for idempotency, race conditions, JWT/OAuth misuse, and strong input validation reduce fraud vectors on high-value payment paths.
- Threat-modeled design reviews. Banking use-case threat models (authorization, ledger integrity, non-repudiation) expose logic abuse early, lowering defect escape into production.
- Pipeline gates and segregation of duties. CI/CD security gates enforce four-eyes principles for risky changes; SAST/SCA/DAST automation prevents insecure builds from shipping.
- Secure secrets and crypto hygiene. Eliminates hardcoded keys, enforces HSM/KMS usage, and standardizes cryptographic configurations, reducing lateral movement and data exposure.
Industry dynamics / trends / challenges / threats
- Explosive release velocity. Continuous product pushes and A/B tests raise the odds of insecure toggles and leaked tokens. Minor missteps can cascade through partner ecosystems.
- API-first monetization. Webhooks, partner tokens, and service accounts expand attack surfaces. Compromise of one integration can pivot into transaction manipulation.
- Partner assurance pressure. Banks/PSPs demand rapid evidence of secure development and remediation capability. Weak proof delays onboarding and revenue.
- Cloud-native complexity. Misunderstood shared responsibility leads to permissive IAM or overly broad secrets distribution. Ephemeral environments can re-introduce old flaws.
- Fraud-tech arms race. Bots and social engineering exploit code paths like refunds or KYC resets, blending technical and human weaknesses.
How Secure code reviews help
- Release-aware review cadence. Code reviews synchronized with sprint demos and feature flags catch insecure defaults and authorization drift before rollout.
- API and token governance. Patterns for token scoping, rotation, and mTLS/OAuth hardening prevent partner and service-account abuse.
- Evidence packs for partners. Control matrices, remediation trackers, and pen-test parity reports accelerate bank/PSP due diligence and partnerships.
- Cloud guardrails as code. IaC reviews and policy-as-code enforce least privilege, network egress control, and secret management across ephemeral stacks.
- Abuse-case testing. Scenario testing of refund loops, id collisions, and rate-limit bypasses reduces fraud leakage without harming conversion.
Industry dynamics / trends / challenges / threats
- Patient safety and availability. Scheduling, EHR, and device integrations must not fail; ransomware or small logic bugs can disrupt care.
- Sensitive PHI/PII obligations. Privacy regulations (GDPR/In-country regulatory norms, guidelines and sectoral norms) require tight data minimization and audit trails. Coding errors often surface as over-collection or insecure transmission.
- Legacy devices and vendors. OEM firmware and non-patchable devices constrain remediation, pushing risk to connected apps and gateways.
- Complex referral ecosystems. Labs, imaging centers, and insurers share data via human-operated channels, increasing integration error rates.
- Growing IoMT/telehealth. Rapidly built companion apps and wearables expand attack surface and consent/retention challenges.
How Secure code reviews help
- Data-protection-by-design. Reviews enforce least-data patterns, field-level encryption, consent checks, and secure logging to limit PHI exposure.
- Secure integration controls. FHIR/HL7 parser hardening, schema validation, and queue idempotency prevent injection and duplication risks across referrals.
- Compensating controls guidance. When devices can’t be patched, app-side isolation, rate limits, and anomaly detection reduce blast radius.
- Threat-informed triage. Prioritizes defects that could interrupt clinical workflows or leak PHI, aligning security work with patient safety.
- Privacy audit evidence. Traceability from code change to control proves compliance posture during investigations and certification.
Industry dynamics / trends / challenges / threats
- 5G core and edge sprawl. Virtualized network functions and orchestration create vast token and API surfaces susceptible to misuse.
- Subscriber data sensitivity. Billing, CDRs, and lawful intercept systems are high-impact targets; access bugs have national-security concerns.
- Multi-vendor supply chain. NEP diversity complicates consistent code quality and firmware provenance, increasing integration risk.
- Nation-state interest. APTs target NOC tooling and orchestrators with tailored phishing and token theft.
- Automation hazards. CI/CD and IaC mistakes can propagate misconfigurations across thousands of nodes.
How Secure code reviews help
- Orchestration/API hardening. Reviews focus on mutual auth, token binding, and privilege boundaries for NFV/SDN controllers.
- Supply-chain verification. SBOM/SCA and signature checks detect tampered components and license risks before deployment.
- High-privilege path protection. Strong approval workflows and just-in-time access patterns reduce blast radius for NOC and admin tools.
- Secure configuration as code. Golden templates and policy enforcement prevent drift and unauthorized changes at scale.
- Operational evidence for regulators. Code-to-control mapping and remediation SLAs ease compliance disclosures.
Industry dynamics / trends / challenges / threats
- Mission-critical citizen services. Identity, subsidies, and land records must be resilient; regressions can stall public programs.
- Procurement and audit traceability. Multi-vendor builds and strict audits require end-to-end evidence of secure development.
- High threat profile. State actors target applications and software supply chains; zero-days meet legacy stacks.
- Heterogeneous estates. Bespoke apps and varying maturity across departments complicate standardization.
- Data sovereignty and privacy. Sensitive citizen data mandates strict access control and transparent processing.
How Secure code reviews help
- Standardized secure SDLC. Common review playbooks and templates normalize security across ministries and integrators.
- Supply-chain scrutiny. SBOM policies, reproducible builds, and attestation reduce tampering risk in third-party components.
- Legacy-aware remediation. Pragmatic fixes (wrappers, proxies, policy controls) mitigate risk where refactors are slow.
- Evidence-rich reporting. Control mappings and artifact trails satisfy CAG/internal audit expectations.
- Zero-trust patterns. Strong authN/Z, segmentation, and service-to-service controls reduce lateral movement in mixed environments.
Industry dynamics / trends / challenges / threats
- Peak-event pressure. Sales spikes compress change windows and tolerance for rollback, making small defects catastrophic.
- Third-party plugin sprawl. Payments, analytics, and logistics SDKs introduce code and data exfil paths.
- Omnichannel parity. Web, mobile, POS, and marketplace integrations complicate session and token consistency.
- Brand and trust dependency. Breaches immediately impact conversion and LTV; privacy violations trigger churn.
- Shadow IT and rapid frameworks. Fast migrations leave stale images, weak CSPs, and missing security headers.
How Secure code reviews help
- Checkout-path hardening. CSRF, session fixation, and mixed-content checks on critical funnels protect GMV.
- Plugin and SDK review. SCA/SBOM and runtime guards block risky third-party code paths and sensitive event leaks.
- Token/session consistency. Unified auth flows and secure cookie handling reduce cross-channel abuse.
- Secure front-end patterns. CSPs, SRI, and anti-skimming defenses protect against Magecart-style attacks.
- Event-aware release gates. Pre-peak reviews and feature-flag hygiene reduce risk during high-revenue windows.
Industry dynamics / trends / challenges / threats
- IP protection and trade secrets. PLM/MES/SCADA integrations expose sensitive designs; code flaws can leak crown-jewel data.
- Long lifecycles, slow patching. Legacy HMIs and controllers persist; compensating software controls are essential.
- IT/OT convergence. Bridge apps and gateways become pivot points for attackers.
- Third-party integrators. Vendor code and field-engineer tools vary in quality, creating uneven risk.
- Ransomware impact. Small footholds can halt production lines and safety systems.
How Secure code reviews help
- Gateway and protocol validation. Input parsing, memory safety, and auth on OT bridge code reduce pivot risk.
- Design-time threat modeling. Protects IP by enforcing least privilege and secure data paths in PLM/MES integrations.
- Compensating control blueprints. Network segmentation, app allow-listing, and command validation mitigate unpatchable endpoints.
- Secure updater pipelines. Signed firmware/app updates and attestation prevent counterfeit loads.
- Vendor code acceptance criteria. Contractual secure coding requirements and review artifacts raise baseline across suppliers.
Industry dynamics / trends / challenges / threats
- Safety-critical operations. Reliability and human safety trump rapid patching; insecure code may remain in service longer.
- Legacy ICS/SCADA. Proprietary stacks and vendor constraints complicate secure development and testing.
- Convergence and remote access. Enterprise–plant connectivity and remote maintenance enlarge the attack surface.
- Regulatory reliability mandates. Demonstrable risk management and event reporting are expected for public confidence.
- Third-party service risk. Contractors and OEMs often hold wide privileges with uneven security hygiene.
How Secure code reviews help
- Plant-safe code assurance. Review patterns emphasize deterministic behavior, fail-safe defaults, and command authorization.
- Remote access hardening. Strong auth, jump-host patterns, and session recording reduce misuse of privileged pathways.
- Change-control integration. Security gates align with outage windows and MOP/SOP approvals to minimize disruption.
- Evidence for regulators. Code-to-control mapping and timeline tracking demonstrate reliability improvements.
- Contractor onboarding standards. Secure coding acceptance and artifact sharing raise bar across OEMs/service vendors.
Industry dynamics / trends / challenges / threats
- Multi-tenant complexity. Tenant isolation, noisy-neighbor risks, and cross-tenant data leaks demand rigorous code isolation.
- Rapid feature flags and experimentation. Entitlement checks and conditional logic drift become common bug classes.
- Supply-chain and open source reliance. Dependency sprawl introduces transitive CVEs and license exposures.
- Infrastructure as code. A mis-templated module can propagate misconfigurations across regions.
- Trust and certification demands. SOC 2/ISO 27001 customers expect evidence of secure SDLC and timely remediation.
How Secure code reviews help
- Tenant-isolation verification. Code reviews validate boundary checks, object scoping, and per-tenant encryption regimes.
- Entitlement and policy engines. Pattern reviews for ABAC/RBAC logic prevent privilege escalation through feature flags.
- SBOM and SCA discipline. Transitive dependency risk is tracked and patched with automated advisories and upgrade paths.
- IaC policy enforcement. Pre-merge checks catch public buckets, open SGs, or over-privileged roles before deploy.
- Assurance for certifications. Evidence packs and control mappings support SOC 2/ISO attestations and enterprise procurement.
Industry dynamics / trends / challenges / threats
- Software-Defined Vehicles & OTA Updates
Modern vehicles rely heavily on software and over-the-air updates, increasing exposure to vulnerabilities in embedded and backend applications. - Connected Ecosystems & V2X Communication
Integration with mobile apps, cloud platforms, and vehicle-to-everything (V2X) communication expands the attack surface across multiple entry points. - Safety-Critical Systems & Regulatory Pressure
Compliance with standards such as ISO 21434 and UNECE WP.29 mandates secure development practices for automotive cybersecurity. - Supply Chain & Third-Party Software Risks
Extensive use of third-party components and open-source libraries introduces hidden vulnerabilities within vehicle software stacks.
How Secure Code Review Helps
- Early Detection of Embedded & Application Vulnerabilities
Identifies security flaws in vehicle software and backend systems during development, reducing risks before deployment. - Secure OTA & API Ecosystem Validation
Ensures that update mechanisms and connected services are protected against unauthorized access and tampering. - Compliance Alignment with Automotive Security Standards
Embeds secure coding practices aligned with ISO 21434 and regulatory requirements, supporting audit readiness. - Supply Chain Risk Mitigation through SCA
Detects vulnerabilities in third-party libraries and components, strengthening overall vehicle software integrity.
Threat landscape
Threat / Challenge:
Broken access control remains the most exploited application weakness because it hides in business logic, object references, and ad-hoc checks. Missing or inconsistent authorization lets attackers escalate privileges, read other users’ data, or perform actions reserved for admins or service accounts. In distributed microservices, token propagation, trust boundaries, and policy drift make authorization failures easier to introduce and harder to spot. The impact is often high—silent, long-lived data exposure and integrity loss that evade basic perimeter controls.
How Codec Networks Secure Code Review & DevSecOps Services Help:
- Policy- and design-first reviews. Threat modeling and architectural assessment align authorization design with business rules (RBAC/ABAC), ensuring checks live at the right enforcement points. This roots out ad-hoc “if” checks and centralizes decisions using vetted policy engines (e.g., OPA), improving consistency across services.
- Code-level verification of every sensitive action. Reviewers trace sensitive flows, ensuring both authentication and authorization guard each resource method and ID. They test for IDORs, horizontal/vertical privilege escalation, and multi-tenant boundary breaks, reducing silent data crossovers.
- Automated tests and CI/CD gates. Unit/integration tests are generated to assert “deny by default” and policy outcomes; pipeline gates fail builds when routes lack guards. Over time, this prevents regression and normalizes secure patterns for new modules.
- Token and session hardening. Services validate JWT scopes, token lifetimes, and audience claims across microservices, eliminating insecure trust assumptions. This limits replay, confused-deputy, and impersonation risks in distributed systems.
- Developer enablement. Targeted coaching and secure coding playbooks translate findings into reusable authorization patterns. Teams learn to externalize policy, prune duplicate checks, and measure coverage, improving velocity and safety together.
Threat / Challenge:
Hardcoded credentials, plaintext API keys in repos, and over-privileged cloud roles are common root causes of breaches. In fast-moving teams, “temporary” keys become permanent, commit history keeps secrets alive, and shared credentials blur accountability. Build logs, crash dumps, and IaC templates also leak secrets inadvertently. Compromise of a single secret frequently enables lateral movement and data exfiltration.
How Codec Networks Secure Code Review & DevSecOps Services Help:
- Secret discovery at scale. Reviews combine scanners and manual inspection to find hardcoded secrets in source, configs, containers, and logs, including history and forks. Findings are triaged with blast-radius analysis so high-impact keys are rotated first.
- Vault integration and least privilege. Consultants move teams to KMS/HSM-backed storage, short-lived tokens, and role-scoped access. They enforce brokered access patterns and eliminate static shared secrets, shrinking the attack window and audit scope.
- Lifecycle controls in pipelines. Pre-commit hooks, protected branches, and CI policies block secret commits and prevent printing tokens in logs. Pipeline secrets are scoped to jobs and rotated automatically, curbing reuse and sprawl.
- Telemetry and response playbooks. Secret-finding alerts integrate with SIEM and ticketing, triggering rotation, revocation, and credential hygiene tasks. Playbooks cut mean time to contain secret leaks and reduce secondary compromise.
- Training and culture. Developers get concise patterns for local dev, test data, and “no secrets in code” rules. This replaces ad-hoc workarounds with safe defaults that don’t slow delivery.
Threat / Challenge:
Open-source reliance introduces transitive CVEs, malicious packages, and typosquats that can subvert build pipelines. SBOM gaps make it hard to know what’s in production, and slow patching leaves exploitable versions deployed for months. Build integrity issues—unsigned artifacts, mutable registries—invite tampering. A single compromised dependency can impact every customer simultaneously.
How Codec Networks Secure Code Review & DevSecOps Services Help:
- SCA + SBOM discipline. Software Composition Analysis inventories all components and versions; SBOMs provide auditable visibility for customers and regulators. This enables fast impact assessment when new CVEs land.
- Trust and provenance controls. Teams adopt signed artifacts, immutable tags, and verified sources for dependencies and base images. Reproducible builds and policy checks prevent unauthorized components from entering the supply chain.
- Risk-based patching SLAs. Consulting establishes severity-tiered SLAs, automated pull requests, and safe rollouts with canaries to minimize disruption. Prioritization aligns with exploitability, not just CVSS headlines.
- Registry and pipeline hardening. Private registries, scoped tokens, and admission controllers block untrusted images at deploy time. This reduces the chance that a malicious image reaches production.
- Third-party attestation. Evidence packs (SBOMs, signing proofs, SLSA levels) accelerate enterprise procurement and compliance reviews, strengthening customer trust.
Threat / Challenge:
Classic yet persistent flaws—SQL/NoSQL/LDAP injection, unsafe deserialization, SSRF, template injection—still yield data theft and remote code execution. Framework misconfigurations and custom serializers widen exposure, especially when apps compose user-supplied inputs into backend calls. Cloud metadata endpoints and internal control planes make SSRF particularly damaging.
How Codec Networks Secure Code Review & DevSecOps Services Help:
- Context-aware code inspection. Reviewers trace tainted data end-to-end, validating parameterization, whitelist validation, and safe encoders. They look past scanners to business logic and custom frameworks where risky patterns lurk.
- Secure libraries and patterns. The service standardizes ORM parameterization, safe template engines, and hardened HTTP clients with SSRF protections. Central patterns replace ad-hoc code, reducing variance and error.
- Exploit reproduction and proof. Hands-on validation (DAST/fuzzing) demonstrates exploitability so fixes get prioritized and verified. Re-tests ensure the defect class—not just one instance—was eliminated.
- Defense-in-depth hooks. Query allow-lists, serializer restrictions, and egress policies limit blast radius even if a flaw survives. Cloud metadata protections and network egress controls blunt SSRF impact.
- Targeted training. Engineers learn anti-pattern recognition in their specific languages and stacks, improving pre-review code quality.
Threat / Challenge:
APIs expose rich, predictable endpoints that adversaries enumerate to lift other users’ data or modify objects they don’t own. Mobile and SPAs intensify API reliance; weak object scoping, over-broad responses, and leaky error messages enable scraping and data exposure. Rate limiting and abuse detection are often an afterthought.
How Codec Networks Secure Code Review & DevSecOps Services Help:
- Object- and tenant-scope verification. Reviews enforce per-object ownership checks, strict field filtering, and multi-tenant isolation. They test IDOR/BOLA paths and confirm errors don’t reveal sensitive internals.
- Contract-first API governance. Schemas (OpenAPI/GraphQL) become security contracts; linting and CI rules catch risky changes before merge. This reduces accidental exposure of new fields or debug routes.
- Abuse-case testing & rate controls. Services add tests for scraping, mass enumeration, and write amplification; rate limits and anomaly detection throttle abuse without hurting legitimate traffic.
- Token scopes and least privilege. Access tokens are narrowed to specific operations and audiences; backend trust is explicitly configured, not implied. This blocks confused-deputy issues across microservices.
- Developer guidance and playbooks. Repeatable patterns for pagination, filtering, and partial responses prevent over-sharing by default.
Threat / Challenge:
Compromised runners, poisoned caches, or stolen CI tokens let attackers insert backdoors at build time. Over-privileged automations and shared credentials magnify impact across many services. Without signed outputs and verified promotion, it’s hard to prove artifacts are unmodified, undermining incident response and customer confidence.
How Codec Networks Secure Code Review & DevSecOps Services Help:
- Principle-of-least-privilege automations. Reviews right-size CI roles, isolate runners, and separate build from deploy permissions. Compartmentalization prevents a single foothold from controlling the whole pipeline.
- Artifact integrity and provenance. Mandatory signing, attestations, and checksum verification protect from tampering; promotion requires verification at each stage. This creates defensible chains of custody.
- Dependency and toolchain pinning. Locked versions and verified sources reduce “build today, break tomorrow” risk from auto-updates or supply-chain swaps.
- Secrets and cache hygiene. Ephemeral credentials, masked logs, and sanitized caches curb credential leakage and replay.
- Red team scenarios for pipelines. Simulated pipeline attacks teach teams to detect suspicious job behavior and to respond quickly, improving resilience to real attempts.
Threat / Challenge:
Public buckets, overly permissive security groups, broad IAM roles, and debug endpoints typically arise from rushed changes and copy-paste IaC. Drift between templates and live environments accumulates quietly, expanding the attack surface. When apps assume the cloud fabric is safe, code-level protections erode.
How Codec Networks Secure Code Review & DevSecOps Services Help:
- IaC review and policy-as-code. Terraform/K8s manifests are scanned and reviewed; OPA/Conftest/Admission policies block risky patterns before apply. Guardrails turn best practices into enforced defaults.
- Golden baselines and drift detection. Baseline modules encode secure patterns for networking, storage, and identity; drift monitors flag deviations for review. This keeps reality aligned with intent.
- Service-to-service trust minimization. Short-lived, scoped roles and explicit network egress reduce lateral movement paths. Apps stop assuming “inside means trusted.”
- Runtime validation. Post-deploy checks confirm that effective permissions match templates and that controls function as designed.
- Developer enablement. Concise IaC patterns and reusable modules help teams move fast without sacrificing security.
Threat / Challenge:
Attackers don’t need CVEs to cause damage—abusing discounts, refunds, onboarding, or limit-checking logic can yield fraud and revenue loss. These issues rarely appear in scanners because they’re contextual and latent in flows and edge cases. As products evolve, new logic paths emerge faster than controls are updated.
How Codec Networks Secure Code Review & DevSecOps Services Help:
- Abuse-case threat modeling. Reviews enumerate high-value workflows and specify invariants (limits, dual approvals, idempotency) that must never break. This frames security in business terms leaders understand.
- Test harnesses for invariants. Property-based and scenario tests enforce invariants across edge cases and concurrency, preventing regressions as features ship.
- Telemetry and guardrails. Application metrics and anomaly detection alert on abnormal refund, coupon, or KYC activity. Guardrails block suspicious bursts until reviewed.
- Separation of duties by design. Critical actions require multi-party approval or time-based release, making single-user abuse impractical.
- Rapid feedback into product. Findings are translated into product backlog items with clear ROI, aligning fraud reduction with growth goals.
Threat / Challenge:
Unnecessary data collection, weak field-level protections, verbose logs, and insecure backups create regulatory and reputational landmines. Multi-region deployments complicate residency, retention, and cross-border transfer rules. During incidents, lack of traceability and evidence intensifies fines and customer churn.
How Codec Networks Secure Code Review & DevSecOps Services Help:
- Privacy-by-design reviews. Data maps ensure collection is minimal, purpose-bound, and consent-aware; sensitive fields get encryption/tokenization and strict access paths. This reduces breach blast radius and legal exposure.
- Logging and redaction standards. Structured logging with redaction and sampling prevents sensitive data in logs and APM traces. Backups and analytics exports are checked for inadvertent exposure.
- Regionalization and residency controls. Code and infra patterns (data sharding, KMS per region, lawful transfer mechanisms) align processing with residency mandates.
- Evidence-ready reporting. Control mappings, SBOMs, remediation SLAs, and training artifacts create a defensible posture for auditors and customers.
- Secure deletion and retention. Automations enforce lifecycle policies and verifiable erasure, reducing storage risk and compliance scope.
Threat / Challenge:
RCE vulnerabilities allow attackers to execute arbitrary code on target systems. These attacks can lead to full system takeover and data compromise. They often arise from insecure deserialization or improper input handling. RCE is one of the most critical application-level threats.
How Codec Networks Secure Code Review & DevSecOps Services Help:
- Secure Coding for Input Handling
Ensures strict validation and sanitization of inputs. Prevents execution of malicious code. Reduces attack vectors significantly. - Manual Code Review for Complex Flaws
Identifies advanced vulnerabilities that automated tools may miss. Focuses on business logic and execution paths. Enhances detection of high-risk issues. - Automated SAST & DAST Testing
Detects potential RCE vulnerabilities during development and runtime testing. Ensures continuous validation of application security. Reduces risk before deployment. - Secure Library & Framework Usage
Encourages use of secure and updated components. Minimizes exposure to known RCE vulnerabilities. Strengthens application integrity.
BLOGS & ARTICLES
Secure code review is no longer optional-DevSecOps integration ensures continuous
protection across modern, fast-paced application development lifecycles.
Blog 1: Banking and Financial services
Invisible Vulnerabilities in Core Banking Code: The Silent Risk Behind Compliance Reports
Read FurtherBLOG 2: Powering and Energy
Securing the Code Behind the Grid: Hardening ICS Applications Before They’re Exploited
Read FurtherBlog 3: Healthcare & Healthtech
The Anatomy of a Healthcare Data Breach: How Insecure Code Enables PHI Exposure
Read FurtherBlog 4: E-Commerce, Retail & Public Sector
Checkout to Codebase: Securing the Digital Storefront with Continuous Code Review
Read FurtherFREQUENTLY ASKED QUESTION
How does Secure Code Review integrated with DevSecOps help identify vulnerabilities
early and improve overall application security posture?
CODEC NETWORKS OTHER RELATED SERVICES
Beyond a single solution - Codec Networks delivers an ecosystem of integrated cybersecurity,
compliance, and resilience services.
-
Assesses cloud environments for misconfigurations and compliance gaps. Ensures data protection and secure cloud architecture.
-
Evaluates network controls, firewall rules, and access policies. Strengthens protection against unauthorized access and lateral movement.
-
Identifies vulnerabilities in web and mobile applications. Helps prevent data breaches and application-level attacks.
-
Tests APIs for authentication, authorization, and data exposure risks. Secures critical integrations and data exchange points.
-
Simulates real-world attack scenarios to test overall security posture. Reveals gaps across people, process, and technology.
-
Evaluates security of operational and connected devices. Prevents disruption and unauthorized control of critical systems.
-
Assesses Wi-Fi networks and endpoint device security. Reduces risks from unauthorized access and compromised devices.
-
Simulates phishing attacks to measure employee awareness. Improves user behavior and reduces human-related risks.
Assesses cloud environments for misconfigurations and compliance gaps. Ensures data protection and secure cloud architecture.
Evaluates network controls, firewall rules, and access policies. Strengthens protection against unauthorized access and lateral movement.
Identifies vulnerabilities in web and mobile applications. Helps prevent data breaches and application-level attacks.
Tests APIs for authentication, authorization, and data exposure risks. Secures critical integrations and data exchange points.
Simulates real-world attack scenarios to test overall security posture. Reveals gaps across people, process, and technology.
Evaluates security of operational and connected devices. Prevents disruption and unauthorized control of critical systems.
Assesses Wi-Fi networks and endpoint device security. Reduces risks from unauthorized access and compromised devices.
Simulates phishing attacks to measure employee awareness. Improves user behavior and reduces human-related risks.